
Afrodita Ransomware — How to Remove Pc Virus?

What Is “Afrodita”? __Readme_Recovery_. Txt File, Which Can Be Found in Every Folder That Contains the Encrypted Files, Is a Ransom Note. Inside of It, You Can...
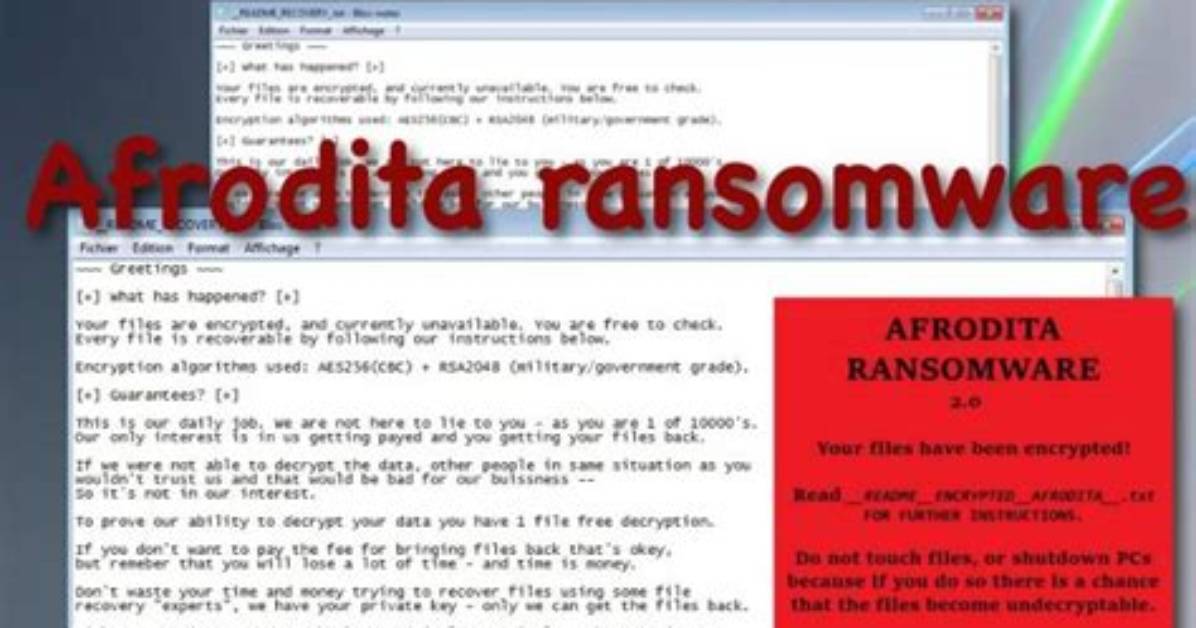
What is “Afrodita”?
__README_RECOVERY_.txt file, which can be found in every folder that contains the encrypted files, is a ransom note. Inside of it, you can find information about ways of contacting Afrodita ransomware developers, and instruction saying about purchasing the decryption tool. This decryption tool is created by ransomware developers, and can be obtained through the email, contacting , , .
| Ransomware family1 | LockerGoga ransomware |
| Ransomware note | __README_RECOVERY_.txt |
| Contact | , , |
| Detection2 | Trojan:Script/Casur.A!cl, TrojanDownloader:O97M/Obfuse.JX!MTB, Trojan.Injuke |
| Fix Tool | See If Your System Has Been Affected by Afrodita virus |
The __README_RECOVERY_.txt file by the Afrodita ransomware states the following frustrating information:
~~~ Greetings ~~~


[+] What has happened? [+]

Your files are encrypted, and currently unavailable. You are free to check.
Every file is recoverable by following our instructions below.

Encryption algorithms used: AES256(CBC) + RSA2048 (military/government grade).

[+] Guarantees? [+]

This is our daily job. We are not here to lie to you - as you are 1 of 10000's.
Our only interest is in us getting payed and you getting your files back.


If we were not able to decrypt the data, other people in same situation as you
wouldn't trust us and that would be bad for our buissness --
So it's not in our interest.

To prove our ability to decrypt your data you have 1 file free decryption.

If you don't want to pay the fee for bringing files back that's okey,
but remeber that you will lose a lot of time - and time is money.

Don't waste your time and money trying to recover files using some file
recovery "experts", we have your private key - only we can get the files back.

With our service you can go back to original state in less then 30 minutes.

[+] Service [+]

If you decided to use our service please follow instructions below.

Contact us:

Install Telegram(available for Windows,Android,iOS) and contact us on chat:
Telegram contact:

Also available at email  cc:

Make sure you are talking with us and not impostor by requiring free 1 file decryption to make sure we CAN decrypt!!
How did I get Afrodita ransomware on my computer?
However, nowadays there are only two ways of Afrodita injection – email spam and trojans. You may see a lot of messages on your email, stating that you need to pay different bills or to get your parcel from the local FedEx department. But all such messages are sent from unknown email addresses, not from familiar official emails of these companies. All such letters contain the attached file, which is used as a ransomware carrier. If you open this file – your system will get infected by Afrodita.
In case of trojans presence, you will be offered to download and install ransomware on your PC under the guise of something legit, like a Chrome update, or update for the software you are storing on your computer. Sometimes, trojan viruses can be masked as legit programs, and ransomware will be offered for download as an important update, or a big pack of extensions which are essential for proper program functioning.
There is also the third way of ransomware injection, however, it becomes less and less popular day-to-day. I am talking about peering networks, such as torrents or eMule. No one can control which files are packed in the seeding, so you can discover a huge pack of different malware after downloading. If circumstances force you to download something from peering networks – scan every downloaded folder or archive with antivirus software.
Alexander Ross has covered the video game industry for a decade, writing deep dives on game design, esports tournaments, VR developments, and gaming culture.
