
Allow All Content Security Policy?

Is It Possible to Configure the Content-Security-Policy to Not Block Anything at All? I'm Running a Computer Security Class, and Our Web Hacking Project Is...
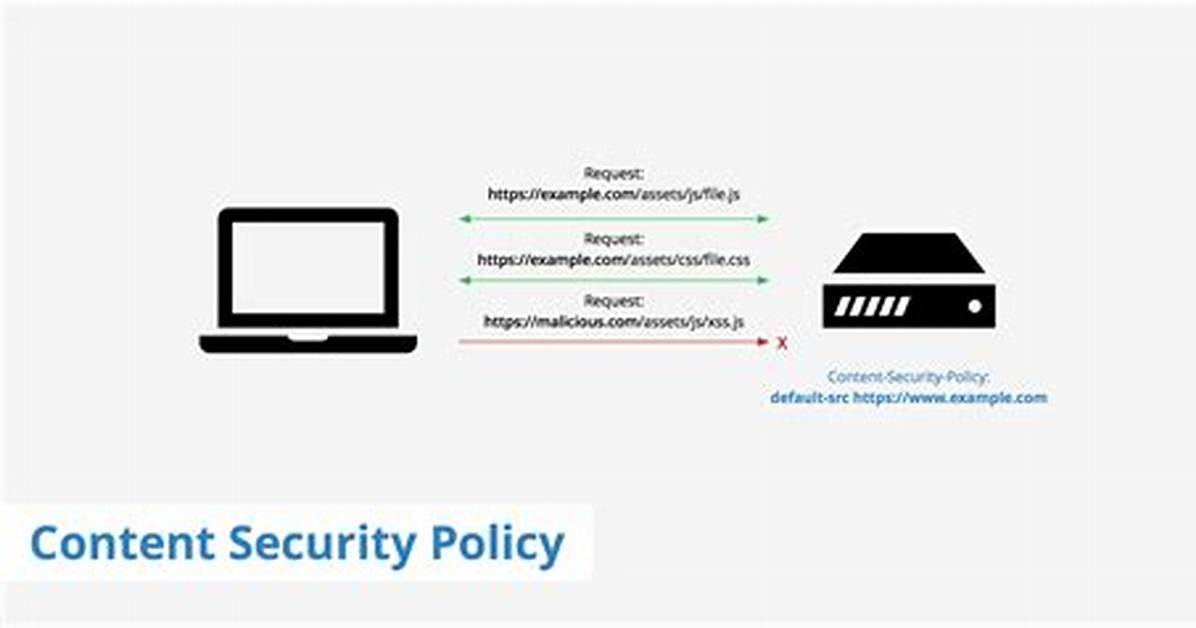
Is it possible to configure the Content-Security-Policy to not block anything at all? I'm running a computer security class, and our web hacking project is running into issues on newer versions of Chrome because without any CSP headers, it's automatically blocking certain XSS attacks.
4 Answers
For people who still want an even more permissive posts, because the other answers were just not permissive enough, and they must work with google chrome for which * is just not enough:
default-src *  data: blob: filesystem: about: ws: wss: 'unsafe-inline' 'unsafe-eval' 'unsafe-dynamic';
script-src * data: blob: 'unsafe-inline' 'unsafe-eval';
connect-src * data: blob: 'unsafe-inline';
img-src * data: blob: 'unsafe-inline';
frame-src * data: blob: ;
style-src * data: blob: 'unsafe-inline';
font-src * data: blob: 'unsafe-inline';
frame-ancestors * data: blob: 'unsafe-inline';
It's not secure at all, but as staring point the real allow all policy is:
default-src * 'unsafe-inline' 'unsafe-eval'; script-src * 'unsafe-inline' 'unsafe-eval'; connect-src * 'unsafe-inline'; img-src * data: blob: 'unsafe-inline'; frame-src *; style-src * 'unsafe-inline';
See: and this CSP migration guide.
The best way would be not applying any policy.
But to answer your question, an "allow all policy" would probably be:
default-src * 'unsafe-inline' 'unsafe-eval' data: blob:;
Note: untested
Here's the htaccess code to allow everything in CSP
Header add Content-Security-Policy "default-src * data: blob: filesystem: about: ws: wss: 'unsafe-inline' 'unsafe-eval' 'unsafe-dynamic'; script-src * data: blob: 'unsafe-inline' 'unsafe-eval'; connect-src * data: blob: 'unsafe-inline'; img-src * data: blob: 'unsafe-inline'; frame-src * data: blob: ; style-src * data: blob: 'unsafe-inline'; font-src * data: blob: 'unsafe-inline';"
Sarah Jenkins is a veteran tech journalist with over 12 years of experience covering artificial intelligence, mobile innovations, and digital ethics. Her insights have appeared in leading technology publications worldwide.
