
Altering Url for Spring Security Saml2 Login

I Have an Application with Multiple Authentication Types (I. E. Basic and a Special Preauthorized Login). I Am Attempting to Add a Saml2 Relyingparty...
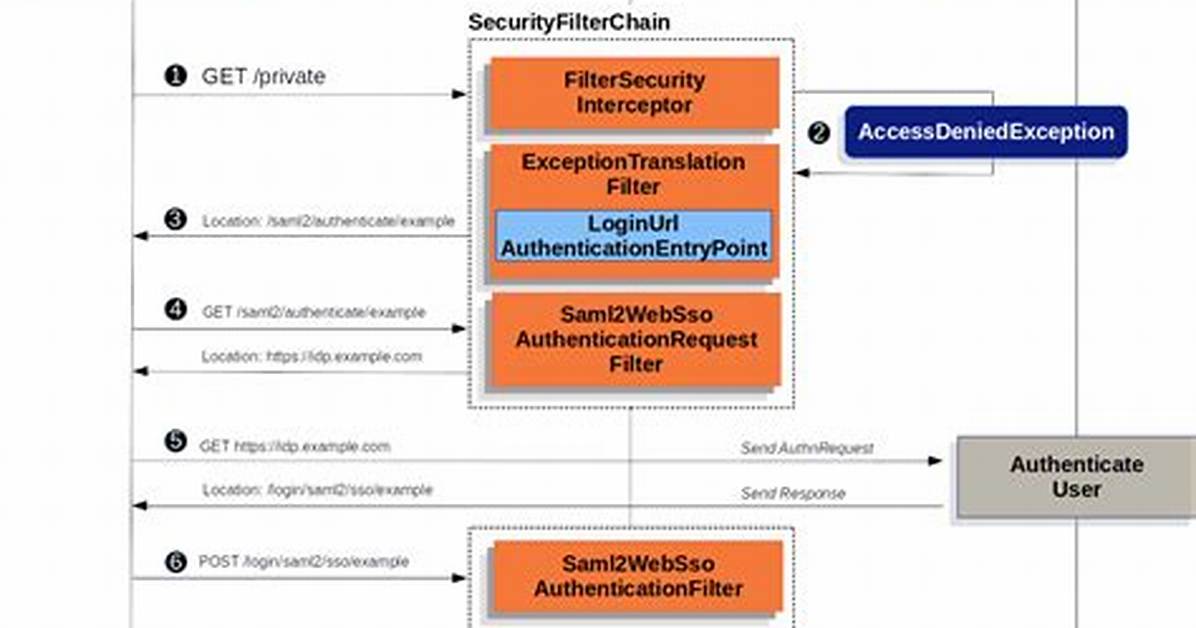
I have an application with multiple authentication types (i.e. Basic and a special Preauthorized login). I am attempting to add a SAML2 RelyingParty registration in my security configuration, where I am attempting to change the default path from:
/login/saml2/sso/{registrationId}
to
/auth/saml2/{registrationId}
So, I have the following setup:
    public RelyingPartyRegistration provder1RelyingPartyRegistration() {

        RelyingPartyRegistration registration = RelyingPartyRegistrations
                .fromMetadataLocation("classpath:provider1/metadata.xml")
                .registrationId("provider1")
                .assertionConsumerServiceLocation("{baseUrl}/auth/saml2/{registrationId}")
                .build();


        return registration;
    }

    // @Bean
    public RelyingPartyRegistrationRepository relyingPartyRegistrationRepository() {

        Collection<RelyingPartyRegistration> registrations = Collections.unmodifiableList(Arrays.asList(provider1RelyingPartyRegistration()));

        InMemoryRelyingPartyRegistrationRepository repository = new InMemoryRelyingPartyRegistrationRepository(registrations);

        return repository;
    }

// fluff

    @Override
    protected void configure(HttpSecurity http) throws Exception {

        final RequestMatcher filterRequestMatcher = new OrRequestMatcher(
                new AntPathRequestMatcher("/auth/basic"),
                new AntPathRequestMatcher("/auth/preauth")
        );

        ApplicationAuthenticationProcessingFilter filter = new ApplicationAuthenticationProcessingFilter(filterRequestMatcher, authenticationManagerBean());
        filter.setAuthenticationSuccessHandler(successHandler());
        filter.setAuthenticationFailureHandler(failureHandler());

        http
                .authorizeRequests()
                .antMatchers("/**").permitAll()
                .and()
                .addFilterAfter(filter, LogoutFilter.class)
                // fluff
                .and()
        .saml2Login()
            .relyingPartyRegistrationRepository(relyingPartyRegistrationRepository())
            .loginProcessingUrl("/auth/saml2/{registrationId}")
        ;
    }
Unfortunately, I get this:
14 Dec 10:55:34 WARN [https-openssl-nio-127.0.0.1-444-exec-2] (DispatcherServlet.java:1278) - No mapping for POST /svc/auth/saml2/provider1
Can anyone tell me what I'm doing wrong trying to change that path? My application does NOT use Spring Boot, so I'm stuck with manual configuration.
EDIT
Some debugging has led to this hitting this line in the Saml2LoginConfigurer:
            Map<String, String> providerUrlMap = getIdentityProviderUrlMap(
                    this.authenticationRequestEndpoint.filterProcessingUrl, this.relyingPartyRegistrationRepository);
Somehow, there's a default authenticationRequestEndpoint (since I didn't define one) setting the filterProcessingUrl to a value of /saml2/authenticate/{registrationId}. So, how do I override this?
1 Answer
The loginProcessingUrl is called by the asserting party after the authentication succeeds, which contains in the request the SAMLResponse parameter.
What you are trying to change is the URL to process an authentication request (create the SAMLRequest and send to the asserting party), this is done by the Saml2WebSsoAuthenticationRequestFilter class. To change the redirectMatcher you have to provide an ObjectPostProcessor, see this issue.
ObjectPostProcessor<Saml2WebSsoAuthenticationRequestFilter> p = new ObjectPostProcessor<>() {
        @Override
        public <O extends Saml2WebSsoAuthenticationRequestFilter> O postProcess(O filter) {
            filter.setRedirectMatcher(new AntPathRequestMatcher("/my/custom/url"));
            return filter;
        }
};
http.saml2Login().addObjectPostProcessor(processor);
Take a look at SAML 2.0 Login Overview for more detail about the flow.
Marcus Vance is a cybersecurity auditor and technology writer dedicated to educating the public about online safety, data privacy regulations, enterprise security, and emerging cyber threats.
