
Apache Giving 403 Forbidden Errors

Ok, So I've Previously Set up Two Virtual Hosts and They Are Working Cool. They Both House Simple Web Projects and Work Fine with and in the Browser. Anyway...
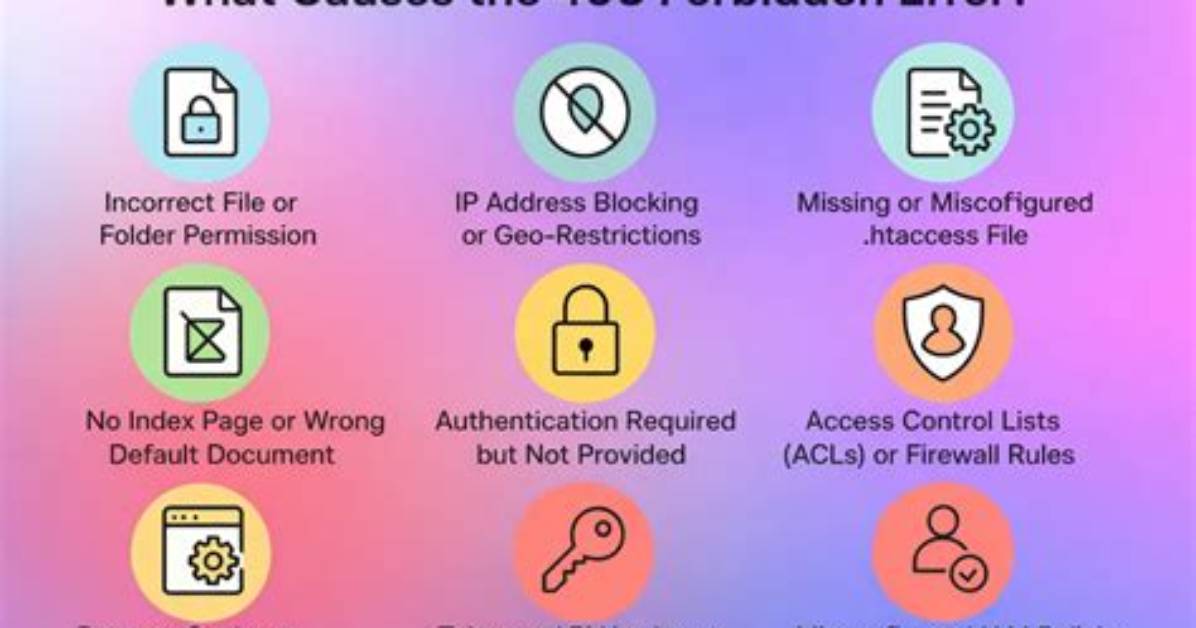
Ok, so i've previously set up two virtual hosts and they are working cool. they both house simple web projects and work fine with and in the browser.
Anyway, I've come to add another vhost. I edited the /etc/hosts file with 127.0.0.1 project3 and also updated the httpd-vhosts.conf file by copy and pasting the previous entries for project2 and editing the file path.
I've checked all the file and folder permissions (in fact I copied and pasted from project2) and simply put a "hello world" message in the index.php file.
I get a 403 forbidden permission denied message when accessing
Why is this, I just can figure out what step I've missed as everything seems to be set up correct.
8 Answers
Check that :
- Apache can physically access the file (the user that run apache, probably www-data or apache, can access the file in the filesystem)
- Apache can list the content of the folder (read permission)
- Apache has a "Allow" directive for that folder. There should be one for /var/www/, you can check default vhost for example.
Additionally, you can look at the error.log file (usually located at /var/log/apache2/error.log) which will describe why you get the 403 error exactly.
Finally, you may want to restart apache, just to be sure all that configuration is applied.
This can be generally done with /etc/init.d/apache2 restart. On some system, the script will be called httpd. Just figure out.
I just fixed this issue after struggling for a few days. Here's what worked for me:
First, check your Apache error_log file and look at the most recent error message.
If it says something like:
access to /mySite denied (filesystem path
'/Users/myusername/Sites/mySite') because search permissions
are missing on a component of the path
then there is a problem with your file permissions. You can fix them by running these commands from the terminal:
$ cd /Users/myusername/Sites/mySite
$ find . -type f -exec chmod 644 {} \;
$ find . -type d -exec chmod 755 {} \;
Then, refresh the URL where your website should be (such as
). If you're still getting a 403 error, and if your Apacheerror_logstill says the same thing, then progressively move up your directory tree, adjusting the directory permissions as you go. You can do this from the terminal by:$ cd .. $ chmod 755 mySiteIf necessary, continue with:
$ cd ..
$ chmod Sites
and, if necessary,
$ cd ..
$ chmod myusername
DO NOT go up farther than that. You could royally mess up your system. If you still get the error that says
search permissions are missing on a component of the path, I don't know what you should do. However, I encountered a different error (the one below) which I fixed as follows:If your
error_logsays something like:client denied by server configuration: /Users/myusername/Sites/mySitethen your problem is not with your file permissions, but instead with your Apache configuration.
Notice that in your
httpd.conffile, you will see a default configuration like this (Apache 2.4+):<Directory /> AllowOverride none Require all denied </Directory>or like this (Apache 2.2):
<Directory />
  Order deny,allow
  Deny from all
</Directory>
DO NOT change this! We will not override these permissions globally, but instead in your
httpd-vhosts.conffile. First, however, make sure that your vhostIncludeline inhttpd.confis uncommented. It should look like this. (Your exact path may be different.)# Virtual hosts Include etc/extra/httpd-vhosts.confNow, open the
httpd-vhosts.conffile that you justIncluded. Add an entry for your webpage if you don't already have one. It should look something like this. TheDocumentRootandDirectorypaths should be identical, and should point to wherever yourindex.htmlorindex.phpfile is located. For me, that's within thepublicsubdirectory.For Apache 2.2:
<VirtualHost *:80>
#     ServerAdmin
    DocumentRoot "/Users/myusername/Sites/mySite/public"
    ServerName mysite
#     ErrorLog "logs/dummy-host2.example.com-error_log"
#     CustomLog "logs/dummy-host2.example.com-access_log" common
    <Directory "/Users/myusername/Sites/mySite/public">
        Options Indexes FollowSymLinks Includes ExecCGI
        AllowOverride All
        Order allow,deny
        Allow from all
        Require all granted
    </Directory>
</VirtualHost>
The lines saying
AllowOverride All
Require all granted
are critical for Apache 2.4+. Without these, you will not be overriding the default Apache settings specified in
httpd.conf. Note that if you are using Apache 2.2, these lines should instead sayOrder allow,deny Allow from allThis change has been a major source of confusion for googlers of this problem, such as I, because copy-pasting these Apache 2.2 lines will not work in Apache 2.4+, and the Apache 2.2 lines are still commonly found on older help threads.
Once you have saved your changes, restart Apache. The command for this will depend on your OS and installation, so google that separately if you need help with it.
I hope this helps someone else!
PS: If you are having trouble finding these .conf files, try running the find command, such as:
$ find / -name httpd.conf
restorecon command works as below :
restorecon -v -R /var/www/html/
Notice that another issue that might be causing this is that, the "FollowSymLinks" option of a parent directory might have been mistakenly overwritten by the options of your project's directory. This was the case for me and made me pull my hair until I found out the cause!
Here's an example of such a mistake:
<Directory />
        Options FollowSymLinks
        AllowOverride all
        Require all denied
</Directory>

<Directory /var/www/>
        Options Indexes # <--- NOT OK! It's overwriting the above option of the "/" directory.
        AllowOverride all
        Require all granted
</Directory>
So now if you check the Apache's log message(tail -n 50 -f /var/www/html/{the_error_log_file_of_your_site}) you'll see such an error:
Options FollowSymLinks and SymLinksIfOwnerMatch are both off, so the RewriteRule directive
is also forbidden due to its similar ability to circumvent directory restrictions
That's because Indexes in the above rules for /var/www directory is overwriting the FolowSymLinks of the / directory. So now that you know the cause, in order to fix it, you can do many things depending on your need. For instance:
<Directory />
        Options FollowSymLinks
        AllowOverride all
        Require all denied
</Directory>

<Directory /var/www/>
        Options FollowSymLinks Indexes # <--- OK.
        AllowOverride all
        Require all granted
</Directory>
Or even this:
<Directory />
        Options FollowSymLinks
        AllowOverride all
        Require all denied
</Directory>

<Directory /var/www/>
        Options -Indexes # <--- OK as well! It will NOT cause an overwrite.
        AllowOverride all
        Require all granted
</Directory>
The example above will not cause the overwrite issue, because in Apache, if an option is "+" it will overwrite the "+"s only, and if it's a "-", it will overwrite the "-"s... (Don't ask me for a reference on that though, it's just my interpretation of an Apache's error message(checked through journalctl -xe) which says: Either all Options must start with + or -, or no Option may. when an option has a sign, but another one doesn't(E.g., FollowSymLinks -Indexes). So it's my personal conclusion -thus should be taken with a grain of salt- that if I've used -Indexes as the option, that will be considered as a whole distinct set of options by the Apache from the other option in the "/" which doesn't have any signs on it, and so no annoying rewrites will occur in the end, which I could successfully confirm by the above rules in a project directory of my own).
Hope that this will help you pull much less of your hair! :)
it doesn't, however, solve the problem, because on e.g. open SUSE Tumbleweed, custom source build is triggering the same 401 error on default web page, which is configured accordingly with Indexes and
Require all granted
The server may need read permission for your home directory and .htaccess therein
You can try disabling selinux and try once again using the following command
setenforce 0
In my case it was failing as the IP of my source server was not whitelisted in the target server.
For e.g. I was trying to access from application running on my source server. On source server find IP by ifconfig
This IP should be whitelisted in the target Server's apache config file. If its not then get it whitelist.
Steps to add a IP for whitelisting (if you control the target server as well) ssh to the apache server sudo su - cd /usr/local/apache/conf/extra (actual directories can be different based on your config)
Find the config file for the target application for e.g. prodcat-443.conf
RewriteCond %{REMOTE_ADDR} <YOUR Server's IP>
for e.g.
RewriteCond %{REMOTE_ADDR} !^192\.68\.2\.98
Hope this helps someone
Chloe Bennett explores the intersection of pop culture, streaming entertainment, digital trends, and contemporary lifestyle. Her weekly commentary reaches thousands of culture enthusiasts.
