
Applying Acl Permissions Using Powershell Set-Acl

New-Item -Type Directory -Path "C: \Myfolder" $Acl = Get-Acl "C: \Myfolder" $Ar = New-Object System. Security. Accesscontrol. Filesystemaccessrule("Username"...
New-Item -Type Directory -Path "C:\MyFolder"
$Acl = Get-Acl "C:\MyFolder"
$Ar = New-Object System.Security.AccessControl.FileSystemAccessRule("username", "FullControl", "Allow")
$Acl.SetAccessRule($Ar)
Set-Acl -Path "C:\MyFolder" -AclObject $Acl
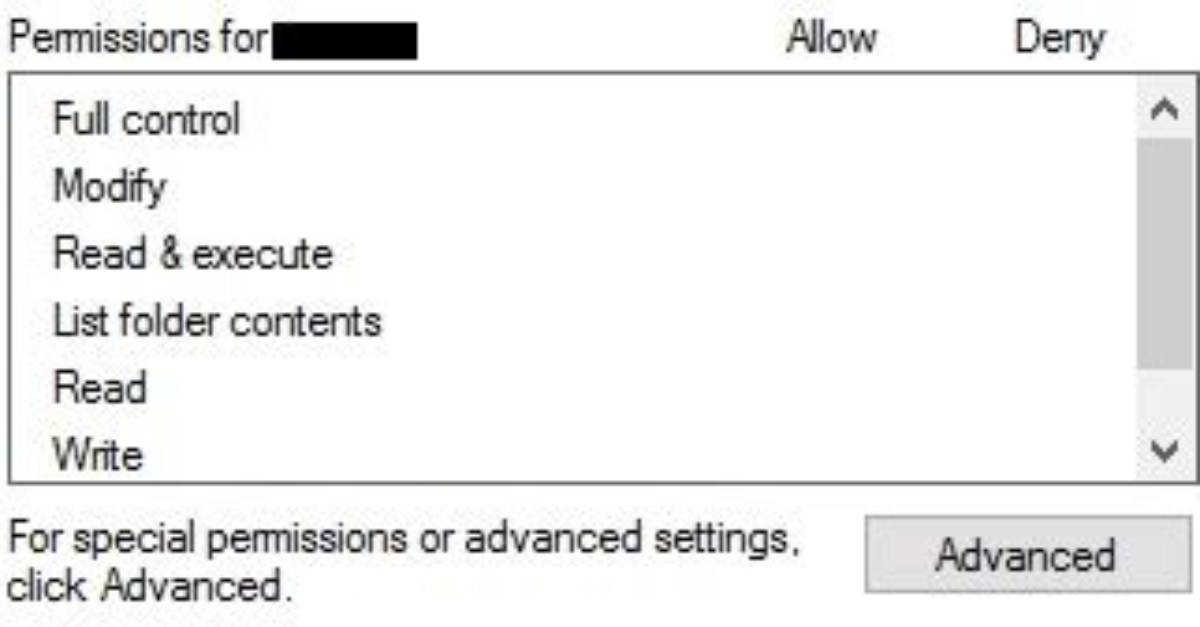
Hi, when I got the above code and applied it using my own settings - the user account entries are added for the folder but, no Permissions are applied (none ticked)
Can anyone help with why this might be?
Thanks
2 Answers
Your comment describes the following behaviour:
Your PowerShell script succeeds but if you check the permissions with the explorers properties dialog, you will see the following:
This is pretty confusing as a PowerShell query will confirm:
PS> Get-Acl .|fl


Path   : Microsoft.PowerShell.Core\FileSystem::D:\temp\myfolder
Owner  : clijsters\clijsters
Group  : clijsters\Kein
Access : clijsters\NEWUSER Allow  FullControl
        VORDEFINIERT\Administratoren Allow  FullControl
        VORDEFINIERT\Administratoren Allow  268435456
        NT-AUTORITÄT\SYSTEM Allow  FullControl
        [...]
Your ACL changed. If you scroll down the list of your checkboxes you will notice, that "Special permissions" is checked and if you click on "Advanced" you will notice, your permissions are set.
EDIT:
As mentioned by @AnsgarWiechers, I missed a part describing why the permissions added with New-Object System.Security.AccessControl.FileSystemAccessRule("username", "FullControl", "Allow") are listed as Special permissions.
Like described on MSDN, FileSystemAccessRule has 4 constructors, where some accept InheritanceFlags and PropagationFlags (e.g. this one fits your needs). If you use them and define inheritance behaviour, the permissions will show up as normal ones.
Today I was trying to compile ILSpy and encountered AL1078: Error signing assembly which is a permissions issue. An amalgamation of answers is shown.
This powershell script assigns $CurUsr to the token for the currently logged in user and $CurTgt as the folder whose permissions are being altered. Change them as required.
Add permission:
$CurTgt = "C:\Users\All Users\Microsoft\Crypto\RSA\MachineKeys"
$CurUsr = [System.Security.Principal.WindowsIdentity]::GetCurrent().Name
$acl = Get-Acl $CurTgt
$AccessRule = New-Object System.Security.AccessControl.FileSystemAccessRule($CurUsr,"FullControl","ContainerInherit,ObjectInherit","None","Allow")
$acl.SetAccessRule($AccessRule)
$acl | Set-Acl $CurTgt
Remove permission:
$CurTgt = "C:\Users\All Users\Microsoft\Crypto\RSA\MachineKeys"
$CurUsr = [System.Security.Principal.WindowsIdentity]::GetCurrent().Name
$acl = Get-Acl $CurTgt
$usersid = New-Object System.Security.Principal.Ntaccount ($CurUsr)
$acl.PurgeAccessRules($usersid)
$acl | Set-Acl $CurTgt
References:
Sarah Jenkins is a veteran tech journalist with over 12 years of experience covering artificial intelligence, mobile innovations, and digital ethics. Her insights have appeared in leading technology publications worldwide.
