
Behavior: Win32/Suspiciouscmdwithpowershell. a — Cmdwithpowershell Behavior Removal Guide

Any Malware Exists with the Only Target – Gain Money on You1. and the Programmers of These Things Are Not Thinking of Ethicality – They Use All Possible...
Any malware exists with the only target – gain money on you1. And the programmers of these things are not thinking of ethicality – they use all possible methods. Grabbing your private data, getting the payments for the banners you watch for them, utilizing your PC to mine cryptocurrencies – that is not the complete list of what they do. Do you like to be a riding horse? That is a rhetorical question.
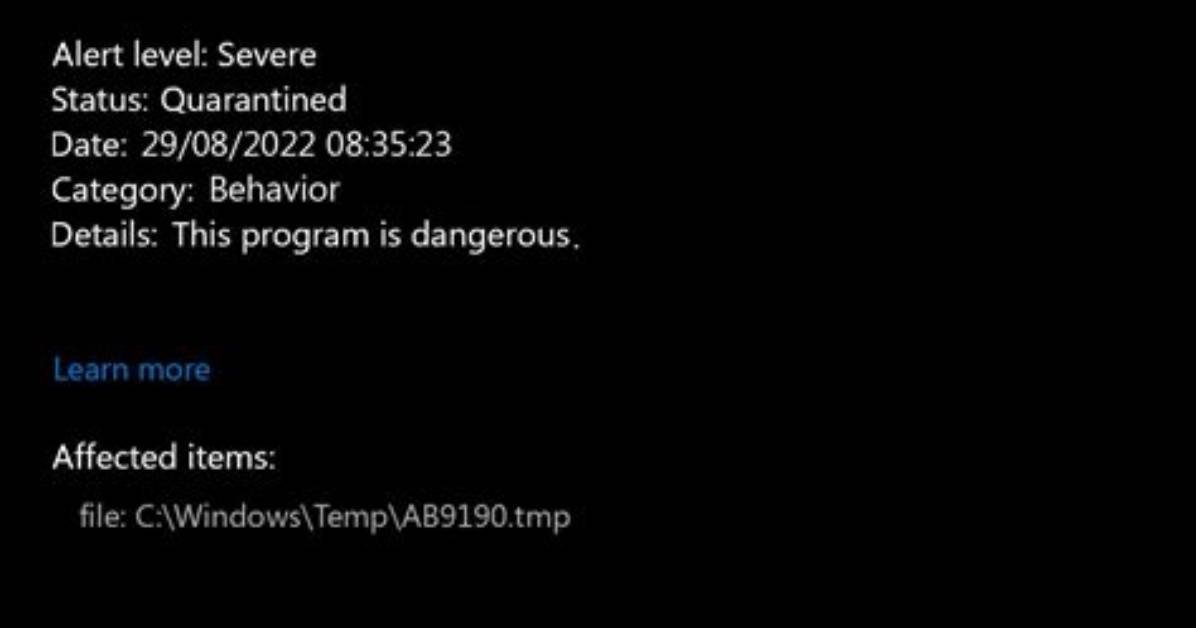
What does the notification with Behavior:Win32/SuspiciousCmdWithPowershell.A detection mean?
The Behavior:Win32/SuspiciousCmdWithPowershell.A detection you can see in the lower right corner is shown to you by Microsoft Defender. That anti-malware software is good at scanning, however, prone to be generally unstable. It is vulnerable to malware attacks, it has a glitchy interface and bugged malware removal features. Thus, the pop-up which says about the CmdWithPowershell is rather just a notification that Defender has actually identified it. To remove it, you will likely need to use a separate anti-malware program.
The exact Behavior:Win32/SuspiciousCmdWithPowershell.A virus is a very unpleasant thing. It digs into your Windows disguised as a part of something legit, or as a part of the tool you downloaded at a forum. Therefore, it makes everything to make your system weaker. At the end of this “party”, it downloads other viruses – ones which are wanted by cybercriminals who control this virus. Hence, it is likely impossible to predict the effects from CmdWithPowershell actions. And the unpredictability is one of the baddest things when we are talking about malware. That’s why it is better not to choose at all, and don’t give it even a single chance to complete its task.
Threat Summary:
| Name | CmdWithPowershell Behavior |
| Detection | Behavior:Win32/SuspiciousCmdWithPowershell.A |
| Details | CmdWithPowershell is attached to another program (such as a document), which can replicate and spread after an initial execution. |
| Fix Tool | See If Your System Has Been Affected by CmdWithPowershell Behavior |
Must Read
Is Behavior:Win32/SuspiciousCmdWithPowershell.A dangerous?
As I have pointed out , non-harmful malware does not exist. And Behavior:Win32/SuspiciousCmdWithPowershell.A is not an exclusion. This malware alters the system setups, edits the Group Policies and registry. All of these things are critical for correct system operating, even in case when we are not talking about Windows safety. Therefore, the virus which CmdWithPowershell contains, or which it will inject after some time, will squeeze out maximum revenue from you. Crooks can steal your personal information, and then push it at the black market. Using adware and browser hijacker functions, embedded in Behavior:Win32/SuspiciousCmdWithPowershell.A malware, they can make money by showing you the banners. Each view gives them a penny, but 100 views per day = $1. 1000 victims who watch 100 banners per day – $1000. Easy math, but sad conclusions. It is a bad choice to be a donkey for crooks.
Sarah Jenkins is a veteran tech journalist with over 12 years of experience covering artificial intelligence, mobile innovations, and digital ethics. Her insights have appeared in leading technology publications worldwide.
