
Best Answer: How Do Iptables Work in Linux?

Contents Iptables Is a Command-Line Firewall Utility That Uses Policy Chains to Allow or Block Traffic. When a Connection Tries to Establish Itself on Your...
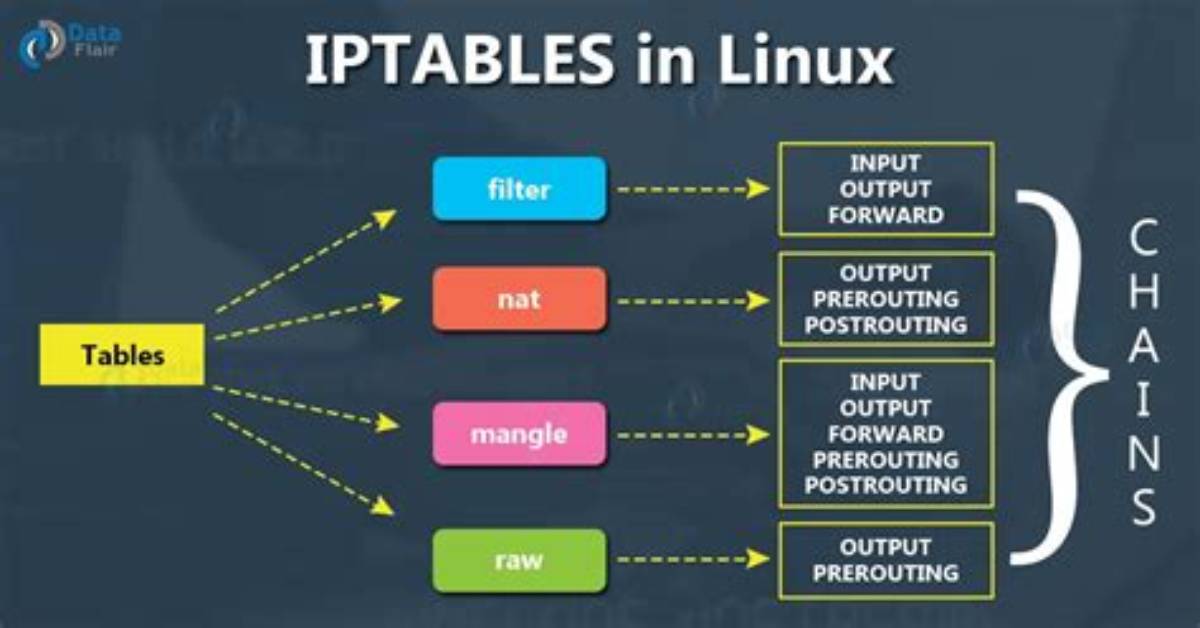
iptables is a command-line firewall utility that uses policy chains to allow or block traffic. When a connection tries to establish itself on your system, iptables looks for a rule in its list to match it to. If it doesn’t find one, it resorts to the default action.
What is the purpose of iptables in Linux?
iptables is a user-space utility program that allows a system administrator to configure the IP packet filter rules of the Linux kernel firewall, implemented as different Netfilter modules. The filters are organized in different tables, which contain chains of rules for how to treat network traffic packets.
Must Read
What is a iptables command in Linux?
iptables is a command line interface used to set up and maintain tables for the Netfilter firewall for IPv4, included in the Linux kernel. The firewall matches packets with rules defined in these tables and then takes the specified action on a possible match. Tables is the name for a set of chains.
James Sterling reports on renewable energy developments, climate policy, ecological conservation, and green tech innovations around the globe.
