
Cognito Associatesoftwaretoken: Token Does Not Have Required Scopes

I Am Setting up Totp-Based Mfa in Cognito According to the Official Documentation. the User Pool Is Configured, the Next Step Is to Associate the Token. Using...
I am setting up TOTP-based MFA in Cognito according to the official documentation. The user pool is configured, the next step is to associate the token. Using boto3:
client = boto3.client('cognito-idp')
client.associate_software_token(access_token)
Which returns the error:
NotAuthorizedException when calling the AssociateSoftwareToken operation:
Access Token does not have required scopes
The token has the scopes email profile openid. What am I missing, what other scopes does it expect?
2 Answers
You are missing the aws.cognito.signin.user.admin scope that is required by pretty much all actions related to users account.
See this question for more details: What does the `aws.cognito.signin.user.admin` scope mean in Amazon Cognito?
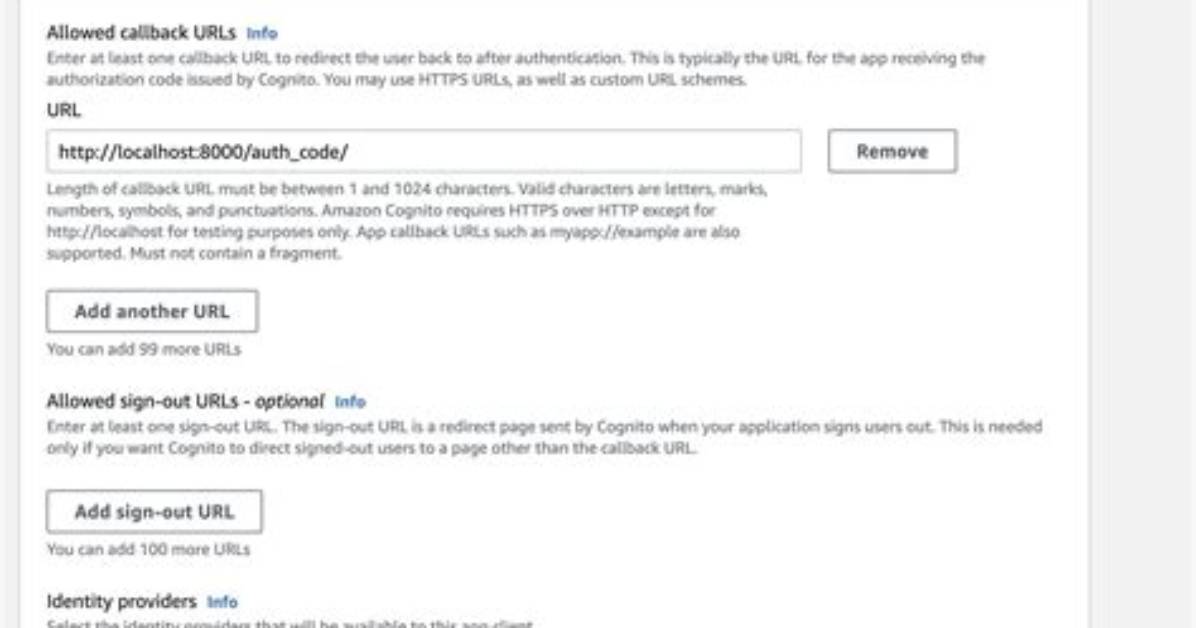
Following up on the (correct) answer by @Aleksandar Wons above, here's a screenshot that shows how/where to set the aws.cognito.signin.user.admin scope in your Cognito app client.
Sarah Jenkins is a veteran tech journalist with over 12 years of experience covering artificial intelligence, mobile innovations, and digital ethics. Her insights have appeared in leading technology publications worldwide.
