
Cookie Header

The Cookie Http Request Header Contains Stored Http Cookies Associated with the Server (I. E. Previously Sent by the Server with the Set-Cookie Header or Set...
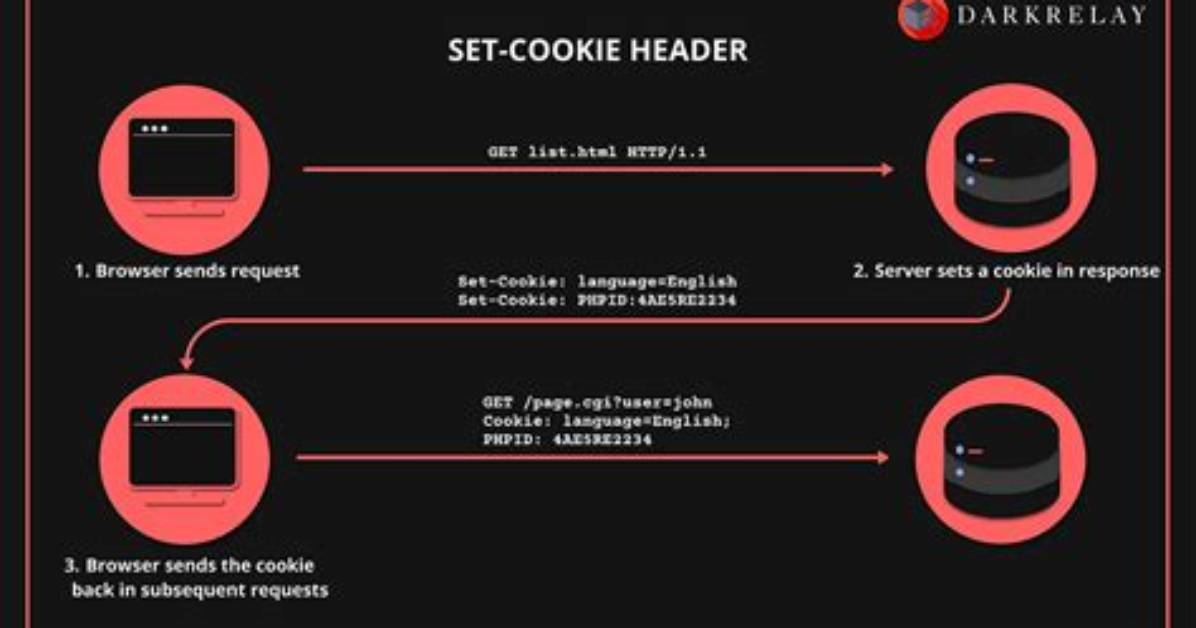
The Cookie HTTP request header contains stored HTTP cookies associated with the server (i.e. previously sent by the server with the Set-Cookie header or set in Javascript using Document. cookie ). The Cookie header is optional and may be omitted if, for example, the browser’s privacy settings block cookies.
How do I get a cookie header?
Then click Settings and more ( 3 dots at the top right corner of internet explorer ) —> Developer Tools menu item. Then click the Network tab, reload the web page, and select one network asset on left, then you can click the Headers or Cookies tab on right to see the related header or cookie values.
Is cookie part of HTTP header?
Each server sends an HTTP request containing the Set-Cookie header, which is used by the client to ioned to an HTTP request, which is used to create a cookie on the user’s system. Cookie servers receive a cookie header as part of HTTP requests sent to them by the client application.
What is the difference between set-cookie and cookie header?
The Set-Cookie header is sent by the server in response to an HTTP request, which is used to create a cookie on the user’s system. The Cookie header is included by the client application with an HTTP request sent to a server, if there is a cookie that has a matching domain and path.
How do I view headers in Chrome?
How to view HTTP headers in Google Chrome?
In Chrome, visit a URL, right click , select Inspect to open the developer tools.Select Network tab.Reload the page, select any HTTP request on the left panel, and the HTTP headers will be displayed on the right panel.
How can a cookie be created in a PHP script?
Setting Cookie In PHP: To set a cookie in PHP, the setcookie() function is used. The setcookie() function needs to be called prior to any output generated by the script otherwise the cookie will not be set. Syntax: setcookie(name, value, expire, path, domain, security);
What does HTTP header contain?
An HTTP response header includes information in a text-record form that a Web server transmits back to the client’s browser. The response header contains particulars such as the type, date and size of the file sent back by the server, as well as information regarding the server.
What is the format of cookie?
Cookies are plain text; they contain no executable code. A web page or server instructs a browser to store this information and then send it back with each subsequent request based on a set of rules. Web servers can then use this information to identify individual users.
How do I pass a cookie URL?
You can’t pass cookies in the URL. You can pass session ID if server supports it. Java Servlet containers do support it (it’s in Servlet spec) by using jsessionid path parameter. Just make sure ;jsessionid= is right after the path, before query (it’s called “path parameter” for a reason).
How do you mark cookies as secure?
Setting the Secure Attribute
How do you read cookies?
How to create and read value from cookie ?
Expires:Specifies when the cookie will expire. Domain: Specifies the domain name of the website.Name=Value: Cookies are stored in the form of name-value pairs.Path: Specifies the webpage or directory that sets the cookie.
What is cookie attribute?
The cookie-attribute command specifies the attributes to include in the DataPower generated cookie when it is returned in a Set-Cookie header. By default, the Secure and the HttpOnly attributes are included, which indicates that the cookie can be sent only when the connection is secure and the connection is over HTTPS.
What is cookie domain?
The origin domain of a cookie is the domain of the originating request. If the origin domain is an IP, the cookie’s domain attribute must not be set. If a cookie’s domain attribute is not set, the cookie is only applicable to its origin domain.
Do web cookies expire?
Cookies typically expire somewhere between 30 and 90 days. Though, some companies do implement shorter cookie expiration dates. It’s also important to note that cookies can be deleted manually by the user or through third-party security programs. The cookie expiration time is very important.
Is session a cookie?
Session cookies are cookies that last for a session. A session starts when you launch a website or web app and ends when you leave the website or close your browser window. Session cookies contain information that is stored in a temporary memory location which is deleted after the session ends.
What does SameSite none mean?
None. Cookies will be sent in all contexts, i.e. in responses to both first-party and cross-origin requests. If SameSite=None is set, the cookie Secure attribute must also be set (or the cookie will be blocked).
Must Read
Postos Recomendados
qual a importancia da litosfera confira isto qual e a importancia de litosfera
qual a importancia da litosfera confira isto qual e a importancia de litosfera
qual os 5 primeiros multiplos de 7 confira isto cinco primeiros multiplos de 7
quantas substituicoes podem ser feitas no jogo de futebol confira isto quantas substituicoes podem ser feitas no futebol
o que eu faco pra ter um relacionamento mais maduro confira isto como ter um relacionamento saudavel e maduro
o que colocar em tipo de endereco confira isto tipo de endereco
Elena Rostova holds a Master's degree in Public Health Journalism. She covers groundbreaking medical research, holistic wellness trends, mental health awareness, and nutritional science.
