
Disallow Changing Boot Option and Bash-Like Command Line in Grub

I'm Using Arch Linux and in My Home, I Share My Computer to Others. They Have Physical Access to My Computer and I Don't Want Them Changing How Grub Boot into...
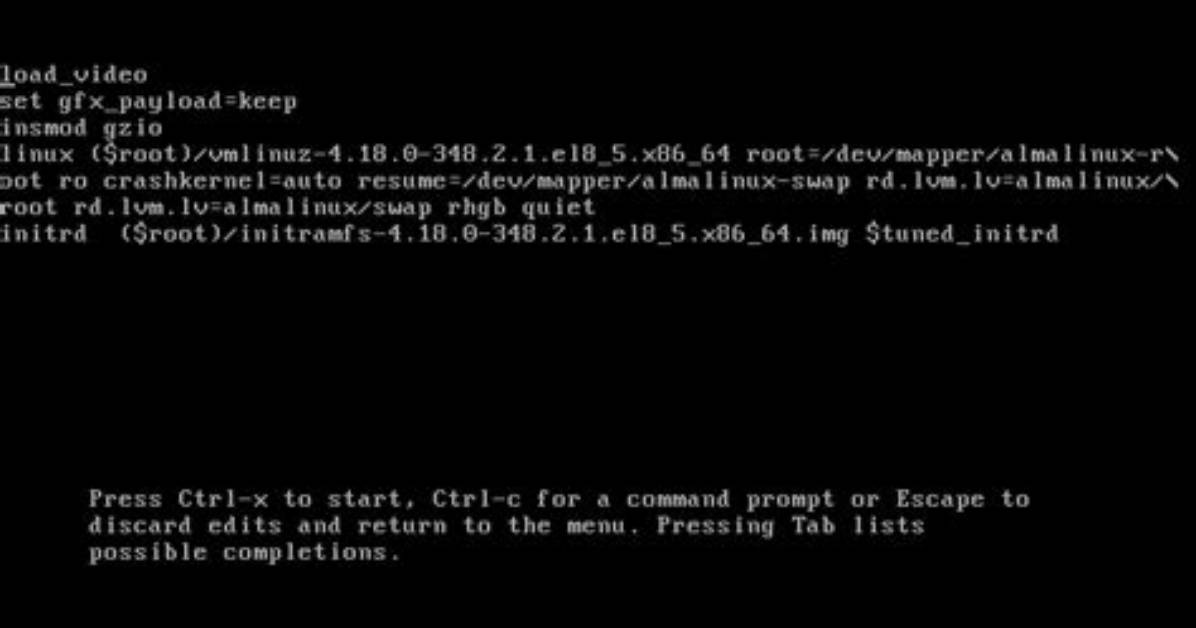
I'm using Arch Linux and in my home, I share my computer to others. They have physical access to my computer and I don't want them changing how GRUB boot into Linux by pressing e or have a command line by pressing c. Is there any way to block them from changing or having a command line in grub? Thanks in advance!!
1 Answer
Is there any way to block them from changing or having a command line in grub?
You can set and then encrypt a grub password:
Use grub password command in
grub.conf
/boot/grub/grub.confcontains information about the entries that are displayed in the GRUB menu during system startup. On some systems,/etc/grub.confis a symbolic link to/boot/grub/grub.confAdd the following
passwordline to thegrub.conffile.$ cat /etc/grub.conf default=0 timeout=15 password GrbPwd4SysAd$ ..Once the
passwordcommand is added to thegrub.conf, the following message will be displayed right under the GRUB menu during the system startup.Use the up-arrow and down-arrow keys to select which entry is highlighted. Press enter to boot the selected OS or 'p' to enter a password to unlock the next set of features.
You should then encrypt the grub password:
Encrypt the grub password using grub-crypt
grub-cryptwill get the clear text password from the user, and display the encrypted password as shown below.# grub-crypt Password: GrbPwd4SysAd$ Retype password: GrbPwd4SysAd$ ^9^32kwzzX./3WISQ0CModify the
grub.conffile, add thepasswordentry with the–encryptedargument as shown below. Just copy the output of thegrub-cryptcommand, and paste it after the–encryptedargument in the password entry.$ cat /etc/grub.conf default=0 timeout=15 password --encrypted ^9^32kwzzX./3WISQ0C..
By default, the
grub-cryptcommand encrypts the password using SHA-512 algorithm. You can also encrypt the password either using SHA-256 or MD5 algorithms as shown below.# grub-crypt --sha-256 # grub-crypt --md5You can also use
md5cryptto encrypt the password. In that case, you should usepassword –md5 encrypted-passwordin yourgrub.conffile.
Source: How to Password Protect Grub Boot Loader in Linux
What if I'm using grub2?
Generate GRUB Bootloader Password
Create a password for GRUB, be a root user, and open the command prompt, type the below command.
# grub2-setpasswordWhen prompted type grub password twice and press enter.
This will generate a hashed GRUB bootloader password in the file
/boot/grub2/user.cfgfile and can be viewed using thecatcommand as shown.# cat /boot/grub2/user.cfgAfter creating the GRUB password, you need to re-create the new GRUB configuration file by running the following command.
# grub2-mkconfig -o /boot/grub2/grub.cfgThe above command will set the grub password in the configuration file. Now, reboot the system and check if the new GRUB password is set properly.
# rebootTesting GRUB Password Protection
After your system restart, you will get the following GRUB screen, where you will get 5 seconds to break the normal boot process. So quickly press e to break the boot process.
Once you press e it will prompt you to enter the GRUB password as shown.
After entering the right username and password, you can edit GRUB parameters as shown.
Source: How to Set GRUB2 Password in RHEL, CentOS and Fedora Linux
Alexander Ross has covered the video game industry for a decade, writing deep dives on game design, esports tournaments, VR developments, and gaming culture.
