
Does a Soc Need a Siem

Siem: an Invaluable Tool for a Soc Team They Need to Have Deep Visibility into All of the Systems Under Their Protection and to Be Able to Detect, Prevent, and...
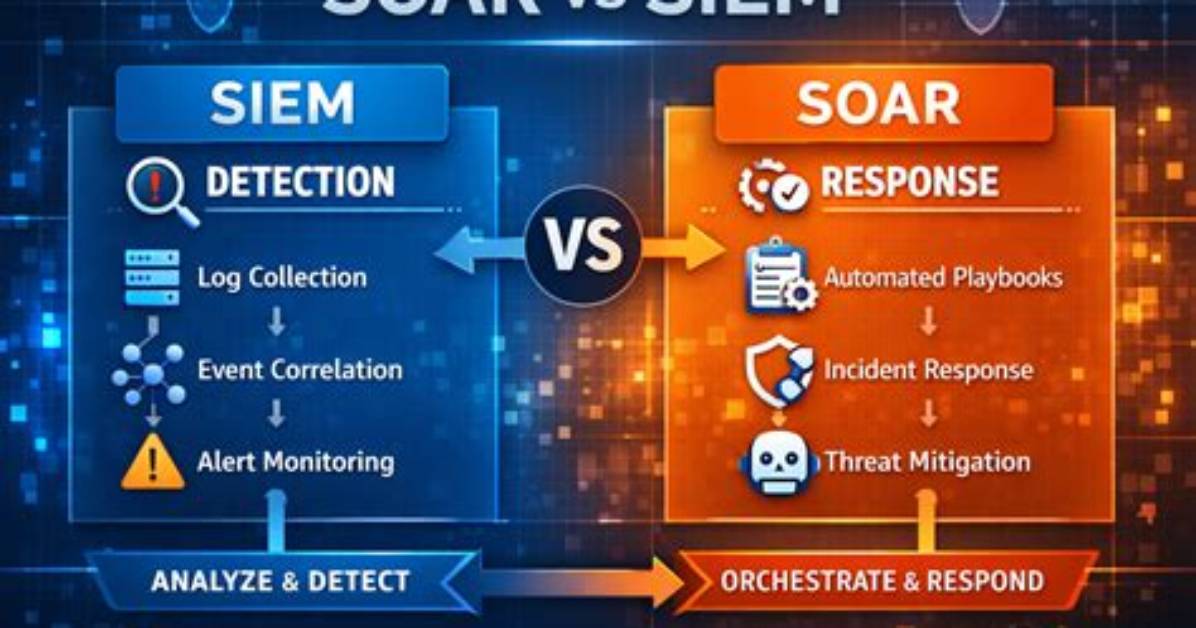
SIEM: An Invaluable Tool for a SOC Team They need to have deep visibility into all of the systems under their protection and to be able to detect, prevent, and remediate a wide range of potential threats. The complexity of the networks and security architectures that SOC analysts work with can be overwhelming.
What are the types of SIEM tools are used for SOC?
- SolarWinds Security Event Manager.
- Micro Focus ArcSight ESM.
- SolarWinds Threat Monitor.
- Splunk Enterprise Security.
- LogRhythm NextGen SIEM.
- IBM QRadar.
- AlienVault Unified Security Management.
- Sumo Logic.
What does SOC mean in security?
Share: A Security Operation Center (SOC) is a centralized function within an organization employing people, processes, and technology to continuously monitor and improve an organization’s security posture while preventing, detecting, analyzing, and responding to cybersecurity incidents.
Elena Rostova holds a Master's degree in Public Health Journalism. She covers groundbreaking medical research, holistic wellness trends, mental health awareness, and nutritional science.
