
Flscrypt Virus 🔐 (. Flscrypt Files) — How to Remove?

What Is Flscrypt Virus? the Scheme of Renaming Is the Following: Id[Xxxxxxxx]. [Contact_Email]. Flscrypt. as a Part of Encryption, a File Named, for Example...
What is Flscrypt virus?
The scheme of renaming is the following: id[xxxxxxxx].[contact_email].FLSCRYPT. As a part of encryption, a file named, for example, “report.docx” will be altered to “report.docx.id[9ECFA84E-3373].[].FLSCRYPT”.
In every directory that contains the encoded files, a info.txt text file will be found. It is a ransom money memo. Therein you can find information about the ways of contacting the racketeers and some other remarks. The ransom note most probably contains a description of how to purchase the decryption tool from the tamperers. You can get this decryptor after contacting via email. That is basically the scheme of the crime.
| Name | Flscrypt Virus |
| Ransomware family1 | Phobos ransomware |
| Extension | .FLSCRYPT |
| Ransomware note | info.txt |
| Contact | |
| Detection2 | Multi:Filecoder-H [Trj], Backdoor:Win32/Dridex.AA!MSR, Trojan.MalPack.FFS |
| Symptoms | Your files (photos, videos, documents) have a .FLSCRYPT extension and you can’t open them. |
| Fix Tool | See If Your System Has Been Affected by Flscrypt virus |
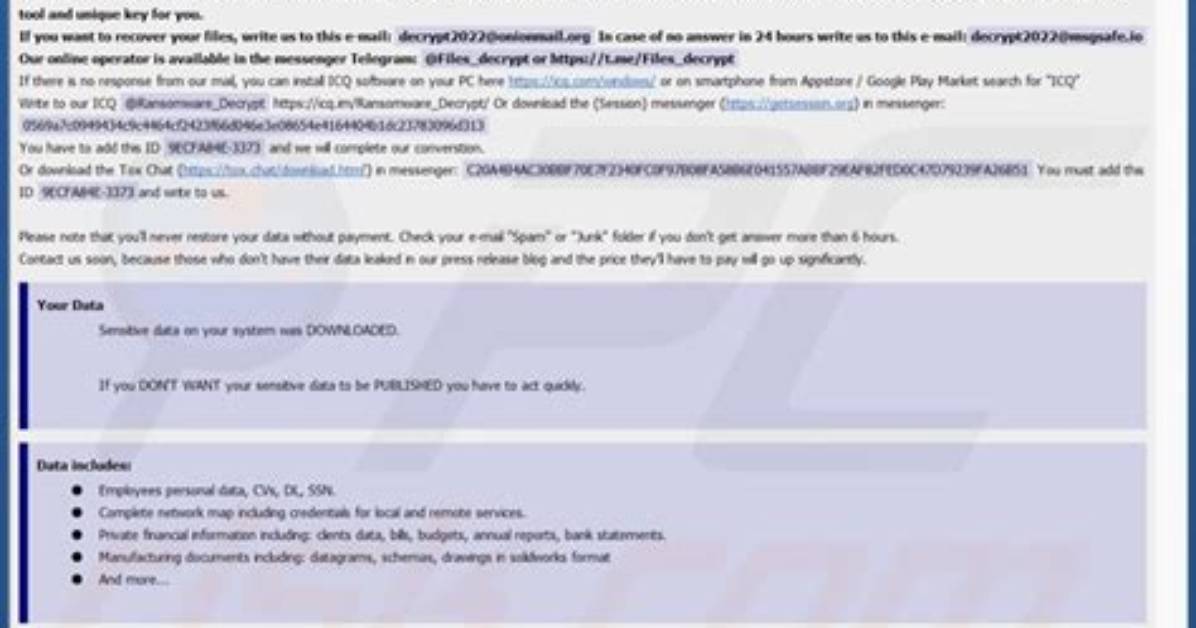
The info.txt document accompanying the Flscrypt malware states the following:
Hello my dear friend. All your files have been encrypted!


Unfortunately for you, a major IT security weakness left you open to attack, your files have been encrypted. The only method of recovering files is to purchase decrypt tool and unique key for you.
If you want to recover your files, write us to this e-mail:  In case of no answer in 24 hours write us to this e-mail:
Our online operator is available in the messenger Telegram: @Files_decrypt or hxxps://
If there is no response from our mail, you can install ICQ software on your PC here hxxps:// or on smartphone from Appstore / Google Play Market search for \"ICQ\"
Write to our ICQ @Ransomware_Decrypt hxxps:// Or download the (Session) messenger (hxxps://getsession.org) in messenger: 0569a7c0949434c9c4464cf2423f66d046e3e08654e4164404b1dc23783096d313
You have to add this ID - and we will complete our converstion.
Or download the Tox Chat (hxxps://) in messenger: C20A4B4AC30BBF70E7F2340FC0F97B08FA58B6E041557ABBF29EAF82FED0C47D79239FA26B51 You must add this ID -and write to us.


Please note that you\'ll never restore your data without payment. Check your e-mail \"Spam\" or \"Junk\" folder if you don\'t get answer more than 6 hours.
Contact us soon, because those who don\'t have their data leaked in our press release blog and the price they\'ll have to pay will go up significantly.


Your Data
Sensitive data on your system was DOWNLOADED.
If you DON\'T WANT your sensitive data to be PUBLISHED you have to act quickly.


Data includes:
Employees personal data, CVs, DL, SSN.
Complete network map including credentials for local and remote services.
Private financial information including: clients data, bills, budgets, annual reports, bank statements.
Manufacturing documents including: datagrams, schemas, drawings in solidworks format
And more...


Attention!
Do not rename encrypted files.
Do not try to decrypt your data using third party software, it may cause permanent data loss.
We are always ready to cooperate and find the best way to solve your problem.
The faster you write - the more favorable conditions will be for you.
Our company values its reputation. We give all guarantees of your files decryption.
In the picture below, you can see what a directory with files encrypted by the Flscrypt looks like. Each filename has the “.FLSCRYPT” extension appended to it.
How did my machine catch Flscrypt ransomware?
Nowadays, there are three most exploited methods for tamperers to have ransomware planted in your system. These are email spam, Trojan introduction and peer file transfer.
If you access your mailbox and see emails that look like familiar notifications from utility services providers, delivery agencies like FedEx, Internet providers, and whatnot, but whose mailer is unknown to you, beware of opening those letters. They are most likely to have a malware file enclosed in them. Therefore, it is even riskier to download any attachments that come with letters like these.
Another option for ransom hunters is a Trojan horse scheme3. A Trojan is a program that infiltrates into your PC pretending to be something legal. For instance, you download an installer of some program you need or an update for some program. But what is unboxed reveals itself a harmful program that corrupts your data. As the installation package can have any title and any icon, you have to make sure that you can trust the source of the stuff you’re downloading. The optimal way is to use the software developers’ official websites.
As for the peer file transfer protocols like torrent trackers or eMule, the threat is that they are even more trust-based than the rest of the Internet. You can never know what you download until you get it. So you’d better be using trustworthy websites. Also, it is reasonable to scan the folder containing the downloaded items with the anti-malware utility as soon as the downloading is done.
Marcus Vance is a cybersecurity auditor and technology writer dedicated to educating the public about online safety, data privacy regulations, enterprise security, and emerging cyber threats.
