
Google Cloud Forwarding Rule Http -> Https Using Terraform

I Have Setup Forwarding Rules, to Map an Url onto My Gcs Bucket Using Terraform. Now, I Am Searching for a Way to Automatically Forward All Traffic from Http...
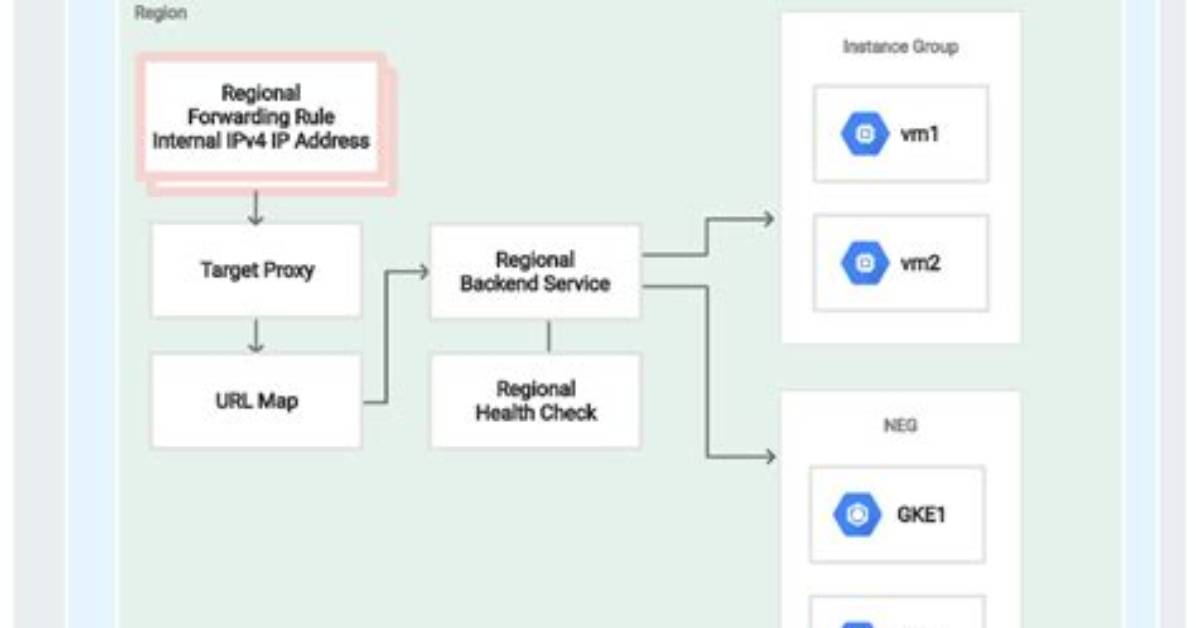
I have setup forwarding rules, to map an URL onto my GCS Bucket using Terraform. Now, I am searching for a way to automatically forward all traffic from HTTP to HTTPS, so everybody reaching my page via HTTP automatically enters the secured page.
Any idea how I can do this using terraform? Below you can find all the code I used to set this up so far which is working perfectly fine. I just need this additional forwarding rule but don't know how to set this up. Any help would be highly appreciated.
locals {
  static_bucket_name = "${var.environment}-${var.project_name}-static-pages"
  domain_name        = var.environment == "prd" ? "products.${project_name}.org" : "${var.environment}.products.${project_name}.org"
}

module "static-assets_cloud-storage-static-website" {
  source                           = "gruntwork-io/static-assets/google//modules/cloud-storage-static-website"
  version                          = "0.2.0"
  website_domain_name              = local.static_bucket_name
  project                          = var.project_id
  website_location                 = "EU"
  force_destroy_access_logs_bucket = true
  force_destroy_website            = true

  custom_labels = {
    environment = var.environment
    purpose     = "static-site"
  }
}


resource "google_compute_backend_bucket" "static_pages" {
  name        = local.static_bucket_name
  description = "Contains static app assets"
  bucket_name = module.static-assets_cloud-storage-static-website.website_bucket_name
  enable_cdn  = true
}


resource "google_compute_url_map" "static_pages" {
  name            = "${var.environment}-products"
  default_service = google_compute_backend_bucket.static_pages.self_link
}

resource "google_compute_global_address" "static_pages" {
  name = "${var.environment}-products-ip"
}

resource "google_compute_global_forwarding_rule" "http_to_static_pages" {
  name       = "${var.environment}-products-forward-rule"
  target     = google_compute_target_http_proxy.http_static_pages.self_link
  ip_address = google_compute_global_address.static_pages.address
  port_range = "80"
}

resource "google_compute_target_http_proxy" "http_static_pages" {
  name    = "${var.environment}-products-target-proxy"
  url_map = google_compute_url_map.static_pages.self_link
}

resource "google_compute_target_https_proxy" "https_static_pages" {
  project          = var.project_id
  name             = "${var.environment}-products-target-proxy"
  url_map          = google_compute_url_map.static_pages.self_link
  ssl_certificates = [google_compute_managed_ssl_certificate.static_pages.self_link]
}

resource "google_compute_global_forwarding_rule" "https_to_static_pages" {
  name       = "${var.environment}-products-https-forward-rule"
  target     = google_compute_target_https_proxy.https_static_pages.self_link
  ip_address = google_compute_global_address.static_pages.address
  port_range = "443"
}

resource "google_compute_managed_ssl_certificate" "static_pages" {
  provider = google-beta
  project  = var.project_id
  name     = "${var.environment}-products-certificate"
  managed {
    domains = [local.domain_name]
  }
}
2 Answers
Google supports this nicely with (only) three extra Terraform resources that create a second load balancer without backend but with a forwarding rule that just redirects to https.
The following is the (working) translation of their documentation:
resource "google_compute_url_map" "http-redirect" {
  name = "http-redirect"

  default_url_redirect {
    redirect_response_code = "MOVED_PERMANENTLY_DEFAULT"  // 301 redirect
    strip_query            = false
    https_redirect         = true  // this is the magic
  }
}

resource "google_compute_target_http_proxy" "http-redirect" {
  name    = "http-redirect"
  url_map = google_compute_url_map.http-redirect.self_link
}

resource "google_compute_global_forwarding_rule" "http-redirect" {
  name       = "http-redirect"
  target     = google_compute_target_http_proxy.http-redirect.self_link
  ip_address = google_compute_global_address.static_pages.address
  port_range = "80"
}
I a little bit changed the Terraform code of Rutger de Knijf's answer above.
I removed "redirect_response_code" then the result is the same:
resource "google_compute_url_map" "http-redirect" {
  name = "http-redirect"

  default_url_redirect {
    // "redirect_response_code" is removed
    // redirect_response_code = "MOVED_PERMANENTLY_DEFAULT"  // 301 redirect
    strip_query            = false
    https_redirect         = true  // this is the magic
  }
}

resource "google_compute_target_http_proxy" "http-redirect" {
  name    = "http-redirect"
  url_map = google_compute_url_map.http-redirect.self_link
}

resource "google_compute_global_forwarding_rule" "http-redirect" {
  name       = "http-redirect"
  target     = google_compute_target_http_proxy.http-redirect.self_link
  ip_address = google_compute_global_address.static_pages.address
  port_range = "80"
}
Sarah Jenkins is a veteran tech journalist with over 12 years of experience covering artificial intelligence, mobile innovations, and digital ethics. Her insights have appeared in leading technology publications worldwide.
