
Granting Rbac Roles in K8S Cluster Using Terraform

I Want to Assign Rbac Rule to a User Providing Access to All the Resources Except 'Create' and 'Delete' Verb in 'Namespace' Resource Using Terraform. Currently...
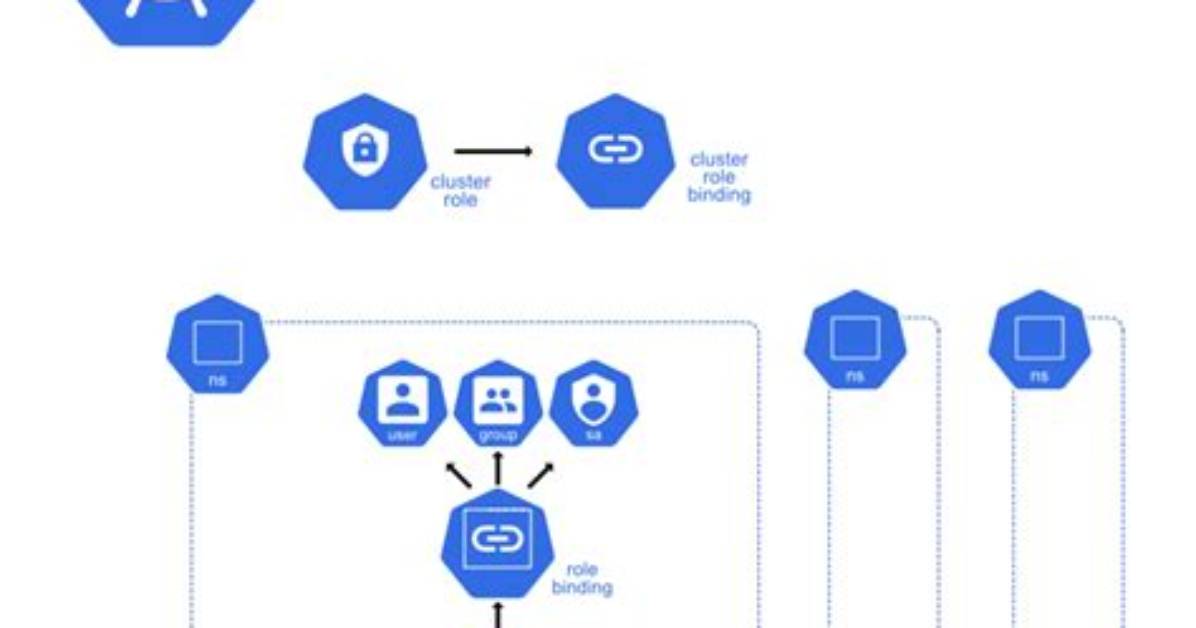
I want to assign RBAC rule to a user providing access to all the resources except 'create' and 'delete' verb in 'namespace' resource using Terraform.
Currently we have rule as stated below:
rule {
    api_groups = ["*"]
    resources  = ["*"]
    verbs      = ["*"]
  }
1 Answer
As we can find in the Role and ClusterRole documentation, permissions (rules) are purely additive - there are no "deny" rules:
Role and ClusterRole An RBAC Role or ClusterRole contains rules that represent a set of permissions. Permissions are purely additive (there are no "deny" rules).
The list of possible verbs can be found here:
You need to provide all verbs that should be applied to the resources contained in the rule.
Instead of:
verbs = ["*"]
Provide required verbs e.g.:
verbs = ["get", "list", "patch", "update", "watch"]
As an example, I've created an example-role Role and an example_role_binding RoleBinding.
The example_role_binding RoleBinding grants the permissions defined in the example-role Role to user john.
NOTE: For details on using the following resources, see the kubernetes_role and kubernetes_role_binding resource documentation.
resource "kubernetes_role" "example_role" {
  metadata {
    name      = "example-role"
    namespace = "default"
  }

  rule {
    api_groups = ["*"]
    resources  = ["*"]
    verbs      = ["get", "list", "patch", "update", "watch"]
  }
}

resource "kubernetes_role_binding" "example_role_binding" {
  metadata {
    name      = "example_role_binding"
    namespace = "default"
  }
  role_ref {
    api_group = "rbac.authorization.k8s.io"
    kind      = "Role"
    name      = "example-role"
  }

  subject {
    kind      = "User"
    name      = "john"
    api_group = "rbac.authorization.k8s.io"
  }
}
Additionally, I've created the test_user.sh Bash script to quickly check if it works as expected:
NOTE: You may need to modify the variables namespace, resources, and user to fit your needs.
$ cat test_user.sh
#!/bin/bash

namespace=default
resources="pods deployments"
user=john

echo "=== NAMESPACE: ${namespace} ==="
for verb in create delete get list patch update watch; do
    echo "-- ${verb} --"
    for resource in ${resources}; do
        echo -n "${resource}: "
        kubectl auth can-i ${verb} ${resource} -n ${namespace} --as=${user}
    done
done

$ ./test_user.sh
=== NAMESPACE: default ===
-- create --
pods: no
deployments: no
-- delete --
pods: no
deployments: no
-- get --
pods: yes
deployments: yes
-- list --
pods: yes
deployments: yes
...
David Miller brings 15 years of experience in global economics, personal finance strategy, and market dynamics. He specializes in turning complex economic trends into actionable insights for everyday readers.
