
Hipandahi Ransomware (. Encrypted File) — How to Remove Virus?

Hipandahi Hipandahi Adds Its Specific “. Encrypted” Extension to the Name of Every File. for Example, Your Photo Named as “My_Photo. Jpeg” Will Be Transformed...
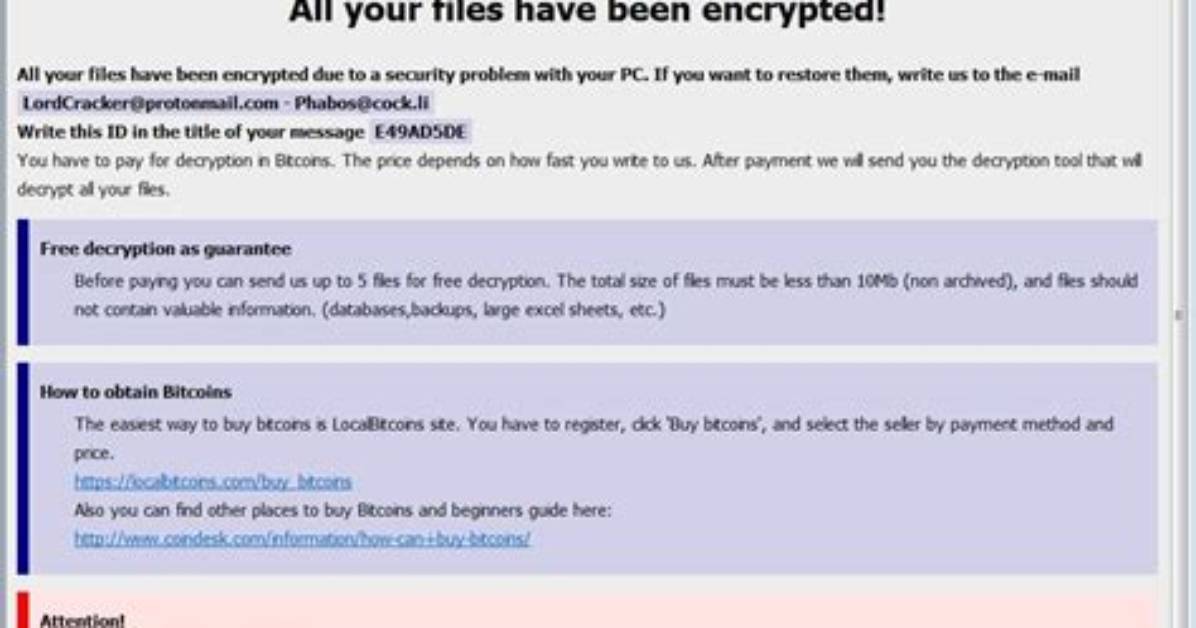
Hipandahi
Hipandahi adds its specific “.encrypted” extension to the name of every file. For example, your photo named as “my_photo.jpeg” will be transformed into “my_photo.jpeg.encrypted“, report in Excel tables named “report.xlsx” – to “report.xlsx.encrypted“, and so on.
How_to_decrypt_my_files.html file, which can be found in every folder that contains the encrypted files, is a ransom money note. Inside of it, you can find information about ways of contacting Hipandahi ransomware developers, and some other info. Inside of the ransom note, there is usually an instruction saying about purchasing the decryption tool. This decryption tool is created by ransomware developers.
YOUR IMPORTANT FILES ARE ENCRYPTED
Do not worry, you can restore it back. If you want to decrypt your files
send your ID: - to

In case of no answer from us in 12 hours write us to  DO NOT MISS YOUR ID -

DO NOT TRY to decrypt your data using third party software since it may cause permanent data loss.
These tools can damage your data, making recover IMPOSSIBLE.
If you want to decrypt your files, you have to get RSA private key from us

FREE DECRYPTION OF ONE FILE AS GUARANTEE!
Just send us up to one encrypted file. MAX SIZE must be less than 1Mb (not archived).
We will decrypt it and send it back to you.

MPORTANT NOTE!
All your data (incl sensitive and/or confidential) has been copied to remote storage and will be automatically posted in the public sources in case you do not contact us within 7 days.
| Name | Hipandahi Virus |
| Extension | .encrypted |
| Ransomware note | How_to_decrypt_my_files.html |
| Detection1 | NSIS/Hoax.ArchSMS.X, TrojanDownloader:Win32/Bredolab.X, Malware.AI.1330581277 |
| Symptoms | Your files (photos, videos, documents) have a .encrypted extension and you can’t open it. |
| Fix Tool | See If Your System Has Been Affected by Hipandahi virus |
The image below gives a clear vision of how the files with “.encrypted” extension look like:
How did I get Hipandahi ransomware on my computer?
However, nowadays there are only two ways of Hipandahi injection – email spam and trojans. You may see a lot of messages on your email, stating that you need to pay different bills or to get your parcel from the local FedEx department. But all such messages are sent from unknown email addresses, not from familiar official emails of these companies. All such letters contain the attached file, which is used as a ransomware carrier. If you open this file – your system will get infected by Hipandahi.
In case of trojans presence, you will be offered to download and install ransomware on your PC under the guise of something legit, like a Chrome update, or update for the software you are storing on your computer. Sometimes, trojan viruses can be masked as legit programs, and ransomware will be offered for download as an important update, or a big pack of extensions which are essential for proper program functioning.
There is also the third way of ransomware injection, however, it becomes less and less popular day-to-day. I am talking about peering networks, such as torrents or eMule. No one can control which files are packed in the seeding, so you can discover a huge pack of different malware after downloading. If circumstances force you to download something from peering networks – scan every downloaded folder or archive with antivirus software.
Chloe Bennett explores the intersection of pop culture, streaming entertainment, digital trends, and contemporary lifestyle. Her weekly commentary reaches thousands of culture enthusiasts.
