
How Do You Set up Ssl Certificates for Additional Ports in Apache? [Closed]

Simple Question, I Just Wanted to Know How to Install Ssl Certificates in Other Ports in a Webserver. I'm Trying to Get a Web Application to Be Able to Have a...
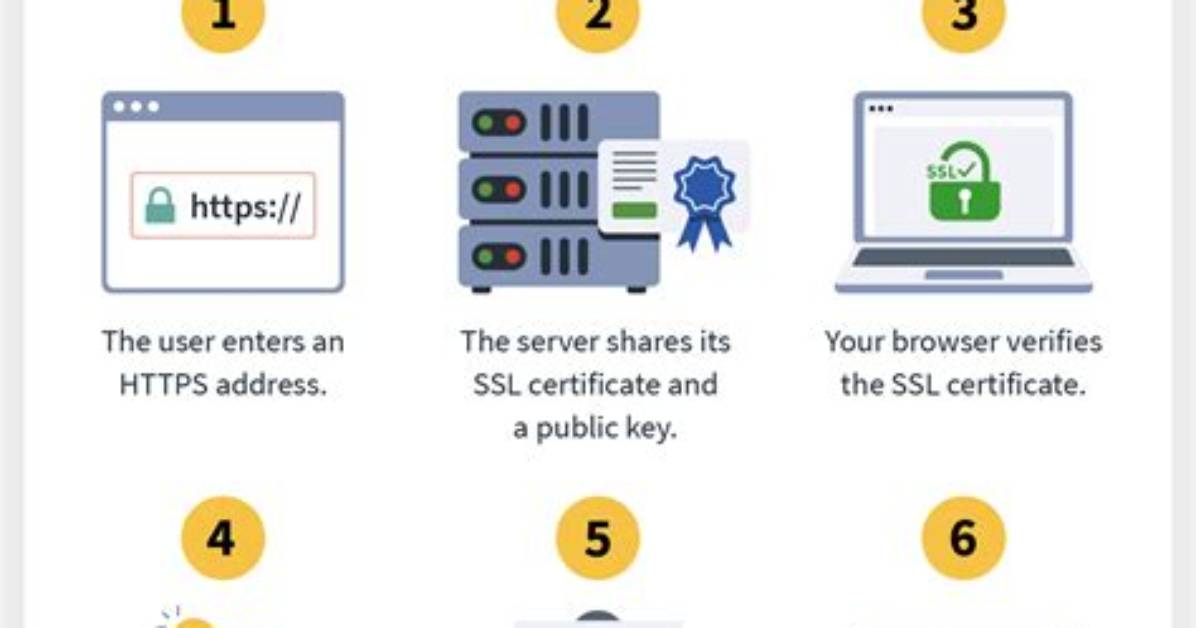
Simple question, I just wanted to know how to install SSL certificates in other ports in a webserver. I'm trying to get a web application to be able to have a valid SSL certificate. I use apache2. I've already tried to edit the virtualhost file. I don't even know what I'm trying to do.
You make modifications in apache's /etc/apache2/ports.conf to inform apache to listen on these different ports:
Listen 8080
<IfModule ssl_module>
        Listen 446
</IfModule>
The steps would be:
Create your SSL certificates:
Make directory to add certificates:
mkdir -p /etc/apache2/ssl/example.comCreate a self signed certificate:
sudo openssl req -x509 -nodes -days 365 -newkey rsa:2048 -keyout /etc/apache2/ssl/ –out /etc/apache2/ssl/
Enable the ssl module with:
sudo a2enmod sslMake entries in your
Virtualhostfiles ( called example.conf ), withsudo nano /etc/apache2/sites-available/example.conf<VirtualHost *:8080> ServerAdmin webmaster@localhost ServerName example.com DocumentRoot /var/www/html </VirtualHost> <IfModule mod_ssl.c> <VirtualHost *:446> ServerAdmin webmaster@localhost ServerName example.com DocumentRoot /var/www/html # SSL Engine Switch: # Enable/Disable SSL for this virtual host. SSLEngine on # A self-signed (snakeoil) certificate can be created by installing # the ssl-cert package. See # /usr/share/doc/apache2.2-common/README.Debian.gz for more info. # If both key and certificate are stored in the same file, only the # SSLCertificateFile directive is needed. SSLCertificateFile /etc/apache2/ssl/ SSLCertificateKeyFile /etc/apache2/ssl/ </VirtualHost> </IfModule>Tell apache to listen in the new ports by adding the ports to
/etc/apache2/ports.conffile:Listen 8080 <IfModule ssl_module> Listen 446 </IfModule> <IfModule mod_gnutls.c> Listen 446 </IfModule>- This tells apache to listen for SSL traffic on port
446as against443
- This tells apache to listen for SSL traffic on port
Enable the config files:
sudo a2ensite exampleRestart apache:
sudo systemctl restart apache2
First you should read these answers:
- How to setup an additional VirtualHost
- Change phpMyAdmin port from 80 to another number
- How to create and enable Let's Encrypt HTTPS certificate
Based on the above answers the steps are:
Create a new VirtualHost configuration file, dedicated to your additional port. Let's assume this is port
99, and the configuration file name ishttps-99.conf:sudo nano /etc/apache2/sites-available/https-99.confThe content of
https-99.confshould look like this:<IfModule mod_ssl.c> Listen 99 <VirtualHost *:99> ServerName DocumentRoot /var/www/html-99 <Directory /var/www/html-99> Options None FollowSymLinks AllowOverride None # To enable .htaccess Overrides: AllowOverride All DirectoryIndex index.html index.php Order allow,deny Allow from all Require all granted </Directory> ErrorLog ${APACHE_LOG_DIR}/https-99.error.log CustomLog ${APACHE_LOG_DIR}/https-99.access.log combined SSLEngine on SSLCertificateFile /etc/letsencrypt/live/ SSLCertificateKeyFile /etc/letsencrypt/live/ SSLCertificateChainFile /etc/letsencrypt/live/ </VirtualHost> </IfModule>Copy the above content and in
nanouse: Shift+Insert for paste; Ctrl+O and Enter for save; Ctrl+X for exit.Enable the configuration file:
sudo a2ensite https-99.confGenerate Let's Encrypt certificate files:
sudo letsencrypt --apache certonly --rsa-key-size 4096 --email -dWhere
andmust be real.Open port
99into the firewall:Create the
DocumentRootdirectory:sudo mkdir /var/www/html-99Put some simple content in the
DocumentRootdirectory:echo 'Hello!!!' | sudo tee /var/www/html-99/index.htmlReload Apache's configuration:
- Ubuntu 14.04:
sudo service apache2 reload - Ubuntu 16.04:
sudo systemctl reload apache2.service
- Ubuntu 14.04:
Try to open
via the browser. The result should be:
Sarah Jenkins is a veteran tech journalist with over 12 years of experience covering artificial intelligence, mobile innovations, and digital ethics. Her insights have appeared in leading technology publications worldwide.
