
How Does Linux Salt Passwords?

Contents When You Change Your Password, the /Bin/Passwd Program Selects a Salt Based on the Time of Day. the Salt Is Converted into a Two-Character String and...
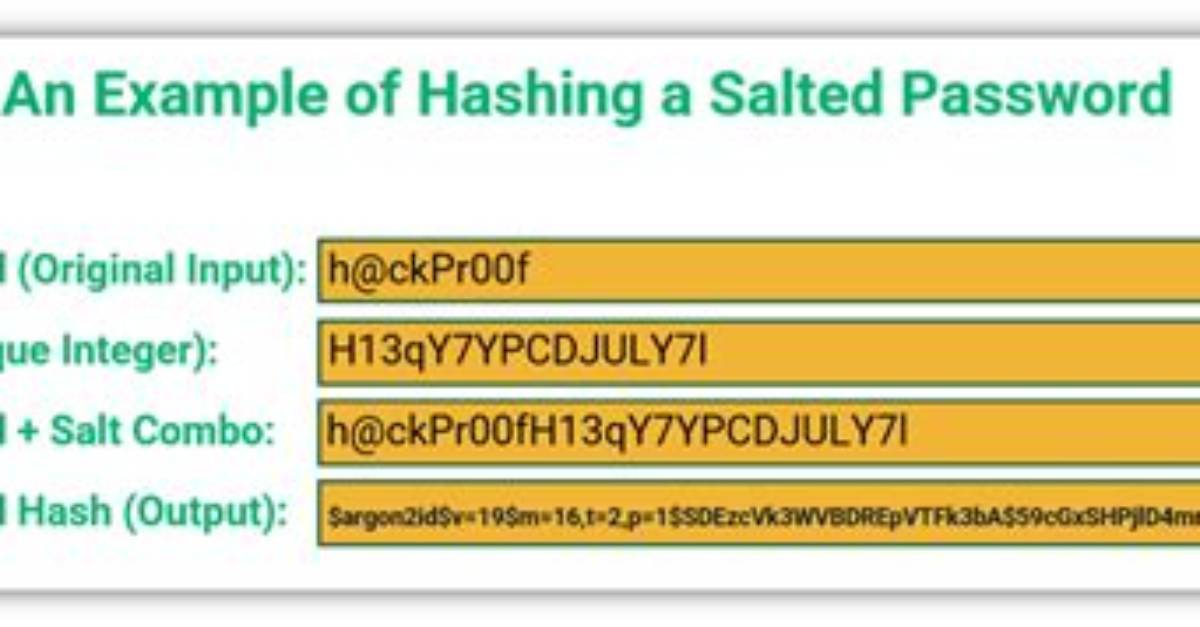
When you change your password, the /bin/passwd program selects a salt based on the time of day. The salt is converted into a two-character string and is stored in the /etc/passwd file along with the encrypted “password.” In this manner, when you type your password at login time, the same salt is used again.
How does Linux encrypt passwords?
Most Unicies (and Linux is no exception) primarily use a one-way encryption algorithm, called DES (Data Encryption Standard) to encrypt your passwords. … This encrypted password is then stored in (typically) /etc/passwd (or less commonly) /etc/shadow.
Must Read
How does salt work for passwords?
A cryptographic salt is made up of random bits added to each password instance before its hashing. Salts create unique passwords even in the instance of two users choosing the same passwords. Salts help us mitigate hash table attacks by forcing attackers to re-compute them using the salts for each user.
Sarah Jenkins is a veteran tech journalist with over 12 years of experience covering artificial intelligence, mobile innovations, and digital ethics. Her insights have appeared in leading technology publications worldwide.
