
How to Create Dkim Record in Microsoft Dns

How Do I Create a Dkim Record in Microsoft Dns? Open Your Windows Dns Manager. ( Start Menu -> Administrative Tools -> Dns) Expand the Nodes on Your Dns Server...
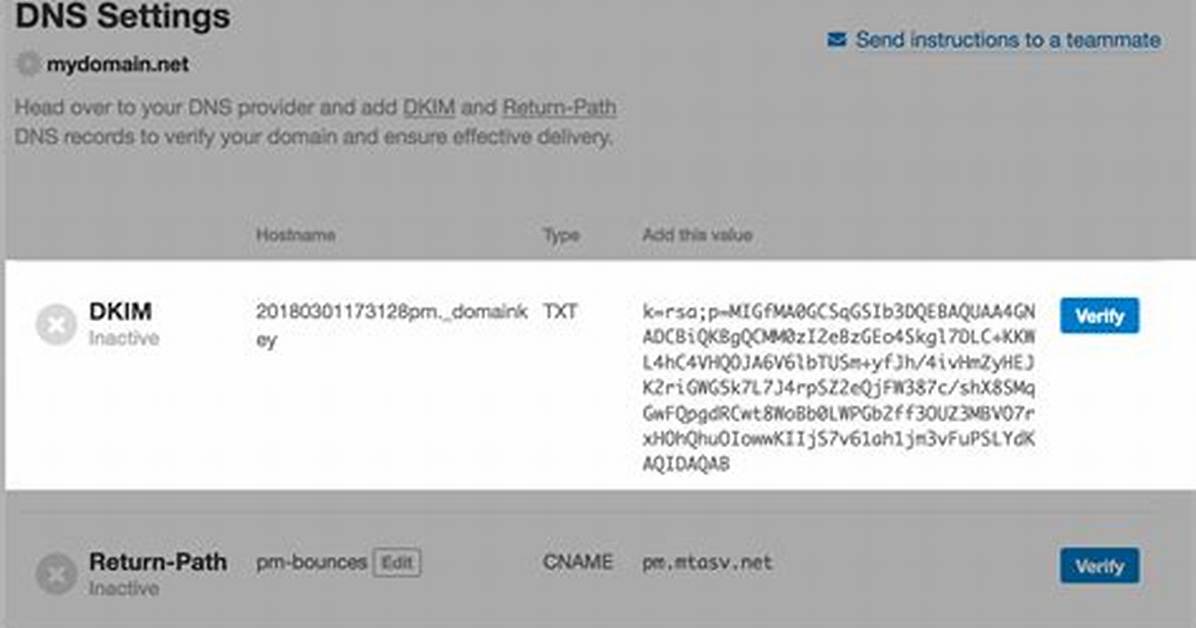
How do I create a DKIM record in Microsoft DNS?
- Open your Windows DNS Manager. ( Start Menu -> Administrative Tools -> DNS)
- Expand the nodes on your DNS Server and select the target domain where you will be adding the two DKIM TXT records:
How do I create a DKIM key?
- Choose a DKIM selector.
- Generate a public-private key pair.
- Publish the selector and public key by creating a DKIM TXT record.
- Attach the token to each outgoing email.
How do I create a Microsoft DNS SPF record?
Select and open a domain (e.g. emailarchitect.net) which you want to add a SPF record to. Right-click the record list and select “Other New Records” from the menu. Select the Text (TXT) record type and click the “Create Record” button.
What is DNS DKIM record?
How do I find my DKIM DNS record?
- Enter ‘Google’ as the Selector. As an example, we’re using a generated domain key from Google Apps.
- The DKIM record is correctly configured when the DKIM Checker shows ‘This is a valid DKIM key record‘.
- If the selector is not valid.
How is DKIM verified?
Mail systems start DKIM verification by making sure the version number meets the DKIM specification, the identity of the sender’s domain matches the domain set in the signature, and the “h=“ tag contains the From header field. The public key decrypts the encrypted hash sent.
Is Dkim better than SPF?
How important is DKIM?
What happens when Dkim fails?
When DKIM alignment fails—or when the d= value in the Header From does not match the d= value in the DKIM signature—it can negatively impact deliverability as mailbox providers may send the message to the spam folder or block it entirely.
Do I need both SPF and DKIM?
How do I fix DKIM error?
Why is DKIM authentication failing?
How long does it take for DKIM to update?
Does DKIM check header or envelope?
How many DKIM records can I have?
Where do I put DKIM records?
- Login to your Name account.
- From the Navigation toolbar, choose My Account and click My Domain.
- Click your domain from the list displayed.
- From the list of option displayed on the left, click DNS Records.
- Enter the following information:
- Click Add Record.
Is it OK to have multiple DKIM records?
A domain can have as many DKIM public keys as servers that send and sign mail. There are two types of DKIM DNS records: The policy record contains information about the DKIM signing policy and the email address of the postmaster. There should only ever be one of these.
Can a domain have two DKIM records?
Can a domain have two SPF records?
A domain name MUST NOT have multiple records that would cause an authorization check to select more than one record. The rule of thumb: multiple SPF records will fail the SPF authentication.
How many IP addresses can I have in an SPF record?
Can you have two TXT records?
What happens if you have 2 SPF records?
If your domain contains more than one entry, recipient servers will decline both. As a result, it will cause your emails to fail an SPF check. There are two ways of tackling this issue. You should remove the SPF entries in the domain’s DNS, that are not in use anymore.
How do I get an SPF record for my domain?
- Log into your Account Center.
- Navigate to the Edit DNS Zone Page Edit DNS Zone Page Edit DNS Zone Page for your desired domain.
- Select the + Add Row button to create a new record. Set the type to TXT and enter your SPF record in the right column.
- Click Save to commit the changes.
Marcus Vance is a cybersecurity auditor and technology writer dedicated to educating the public about online safety, data privacy regulations, enterprise security, and emerging cyber threats.
