
How to Patch the Heartbleed Bug (Cve-2014-0160) in Openssl?

As of Today, a Bug in Openssl Has Been Found Affecting Versions 1.0.1 Through 1.0.1F (Inclusive) and 1.0.2-Beta. Since Ubuntu 12.04, We Are All Vulnerable to...
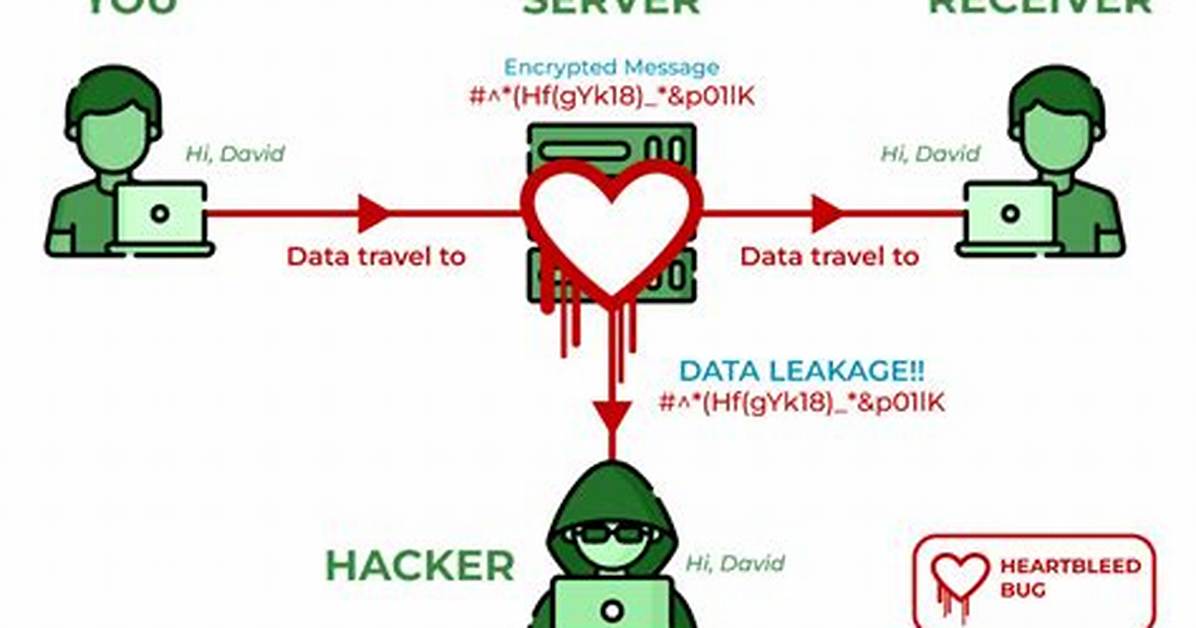
As of today, a bug in OpenSSL has been found affecting versions 1.0.1 through 1.0.1f (inclusive) and 1.0.2-beta.
Since Ubuntu 12.04, we are all vulnerable to this bug. In order to patch this vulnerability, affected users should update to OpenSSL 1.0.1g.
How can every affected user apply this update now?
6 Answers
Security updates are available for 12.04, 12.10, 13.10 and 14.04 see Ubuntu Security Notice USN-2165-1.
So first you need to apply the available security updates, for example by running
sudo apt-get update
sudo apt-get upgrade
from the command line.
Do not forget to restart the services (HTTP, SMTP, etc.) that use the affected OpenSSL version, otherwise you are still vulnerable. See also Heartbleed: What is it and what are options to mitigate it? on Serverfault.com.
The following command shows (after an upgrade) all services that need to be restarted:
sudo find /proc -maxdepth 2 -name maps -exec grep -HE '/libssl\.so.* \(deleted\)' {} \; | cut -d/ -f3 | sort -u | xargs --no-run-if-empty ps uwwp
After that, you need to regenerate all server SSL keys, then evaluate whether your keys may have leaked, in which case attackers may have retrieved confidential information from your servers.
The bug is known as Heartbleed.
Must Read
Am I vulnerable?
Generally, you're affected if you run some server that you generated an SSL key for at some point. Most end-users are not (directly) affected; at least Firefox and Chrome don't use OpenSSL. SSH is not affected. The distribution of Ubuntu packages isn't affected (it relies on GPG signatures).
You are vulnerable if you run any kind of server that uses OpenSSL versions 1.0–1.0.1f (except of course versions that were patched since the bug was discovered). The affected Ubuntu versions are 11.10 oneiric through 14.04 trusty pre-releases. It's an implementation bug, not a flaw in the protocol, so only programs that use the OpenSSL library are affected. If you have a program linked against the old 0.9.x version of OpenSSL, it isn't affected. Only programs that use the OpenSSL library to implement the SSL protocol are affected; programs that use OpenSSL for other things are not affected.
If you ran a vulnerable server exposed to the Internet, consider it compromised unless your logs show no connection since the announcement on 2014-04-07. (This assumes that the vulnerability wasn't exploited before its announcement.) If your server was only exposed internally, whether you need to change the keys will depend on what other security measures are in place.
Marcus Vance is a cybersecurity auditor and technology writer dedicated to educating the public about online safety, data privacy regulations, enterprise security, and emerging cyber threats.
