
How to Set Umask for a Folder and It's Subfolder?

I'm Working on the Same Directory with Some Friends and They Access It via Ssh. I Added Us in the Same Group and Defined a Sticky Bit to Keep the User: Group...
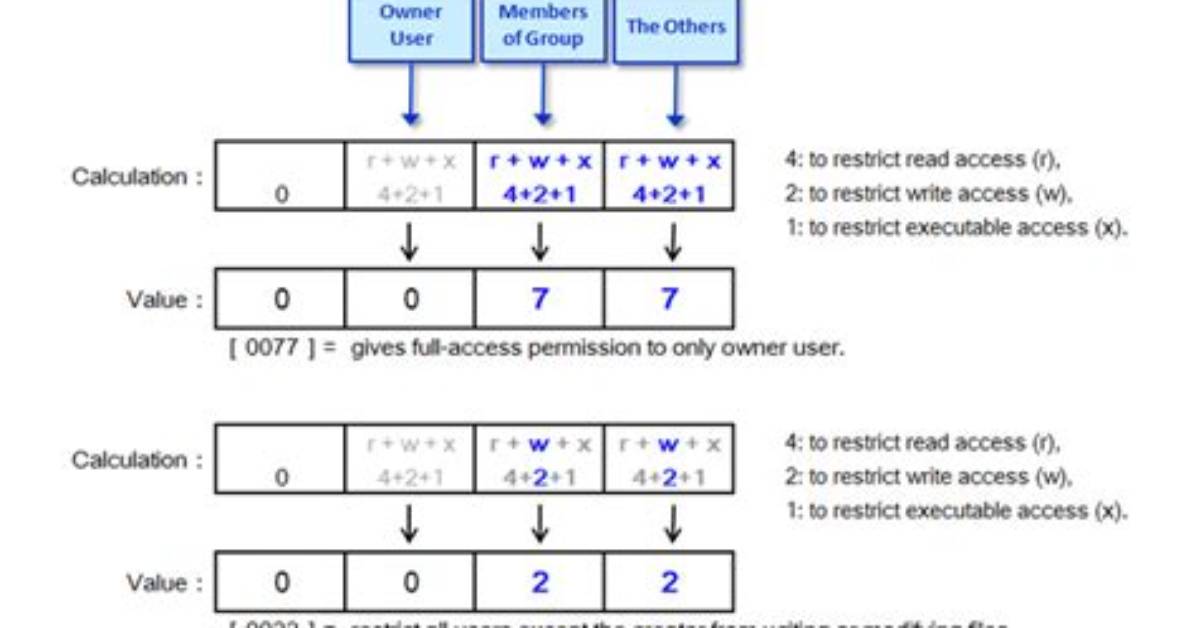
I'm working on the same directory with some friends and they access it via SSH.
I added us in the same group and defined a sticky bit to keep the user:group values the same.
But when a user create a file/folder, the Write attribute is not defined for the group, disabling other to write it/on it.
How can I define the Umask to add the Write value for groups in the specific directory and it's subfolders ?
I tried to find some help before, but I only saw helps for Fedora/CentOs, and I'm using Debian Squeeze.
Thanks for your help
3 Answers
I assume that you did already:
chmod g+rwxs directory
and now you have to make sure that the users have a umask like 002. To setup the umask for all the users, try in /etc/bashrc or /etc/profile.
caveat: you cannot setup a umask per directory as it's a process level thing.
Interesting read
The umask is an attribute of a user's environment (more specifically, a process) rather than a directory. So each of the users sharing that directory should add the following umask command to their ~/.profile:
umask 002
This will make files they create group-writeable by default.
Here's a comprehensive example using setfacl which gives you that granular control you requested on a per-directory basis where new files will be created with the write attribute for the group:
1.Create the group that will own the shared folder:
sudo addgroup projects
2.Create the folder "project1" we want to share in an appropriate FHS path such as /srv:
sudo mkdir /srv/project1
3.Change ownership of the shared folder "project1" to group "projects":
sudo chown root:projects /srv/project1
4.Set the mode on the folder to be be writable to group members, but only allow the owner to delete their own files:
sudo chmod -R 1775 /srv/project1
4.Add your users to the group "projects":
sudo usermod -a -G projects user1
sudo usermod -a -G projects user2
5.Users must log-out and log back in to recognize the new group memberships
6.Finally, apply setfacl so all new files are created writable by group members:
sudo setfacl -d -m group:projects:rwx /srv/project1
Users can now edit each other's files. In terms of managing group documents, a versioning system such as Git is going to be a better solution
Sarah Jenkins is a veteran tech journalist with over 12 years of experience covering artificial intelligence, mobile innovations, and digital ethics. Her insights have appeared in leading technology publications worldwide.
