
How to Update a Ssl Certificate from a Private Key?

A Client Sent Me a New Ssl Certificate for His Domain Site1. Hisdomain. Com. the a-Dns to This Subdomain Points to My Own Server, Running Ubuntu/Apache2. My...
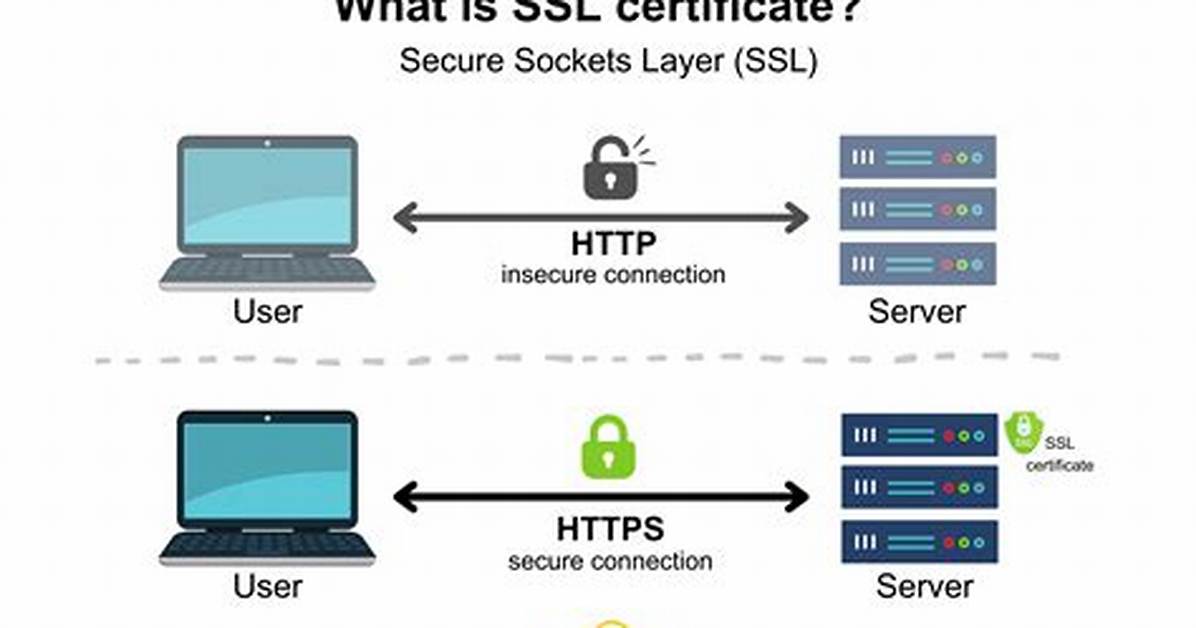
A client sent me a new SSL certificate for his domain site1.hisdomain.com.
The A-DNS to this subdomain points to my own server, running Ubuntu/Apache2.
My Apache .conf for this domain site1.hisdomain.ch is this:
UseCanonicalName Off

<VirtualHost *:443>
     DocumentRoot /var/www/site1/
     ServerName oursite.myserver.com
     ServerAlias site1.hisdomain.com
     <Directory /var/www/site1>
        Options +FollowSymlinks
        AllowOverride All
        Require all granted
     </Directory>

     ErrorLog ${APACHE_LOG_DIR}/site1-error.log
     CustomLog ${APACHE_LOG_DIR}/site1-access.log combined

  <FilesMatch ".php$">
         SetHandler "proxy:unix:/var/run/php/php7.4-fpm.sock|fcgi://localhost/"
      </FilesMatch>

SSLEngine on
SSLCertificateFile /etc/ssl/site1.hisdomain.com.pem
SSLCertificateKeyFile /etc/ssl/site1.hisdomain.com.key
SSLCertificateChainFile /etc/ssl/site1.hisdomain.com.csr

</VirtualHost>
He sent me a PFX file, which installed now a local certificate in my Keychain (a private key, RSA). How i can updated now the SSL certificate on my server from this file without crashing everything?
I overtook the server from a friend and have not really expirience how to update now the certificate.
Thanks!
Must Read
Know someone who can answer? Share a link to this question via email, Twitter, or Facebook.
David Miller brings 15 years of experience in global economics, personal finance strategy, and market dynamics. He specializes in turning complex economic trends into actionable insights for everyday readers.
