
Info Ransomware (. Info File) — Removal Guide

What Is Known About the Infovirus? the Renaming Will Be Executed by the Following Scheme: Id-Xxxxx. [Contact_Email]. Info. as a Part of Encryption, a File...
What is known about the Infovirus?
The renaming will be executed by the following scheme: id-xxxxx.[contact_email].info. As a part of encryption, a file named, for instance, “report.docx” will be changed to “report.docx.id-9ECFA84E.[].info”.
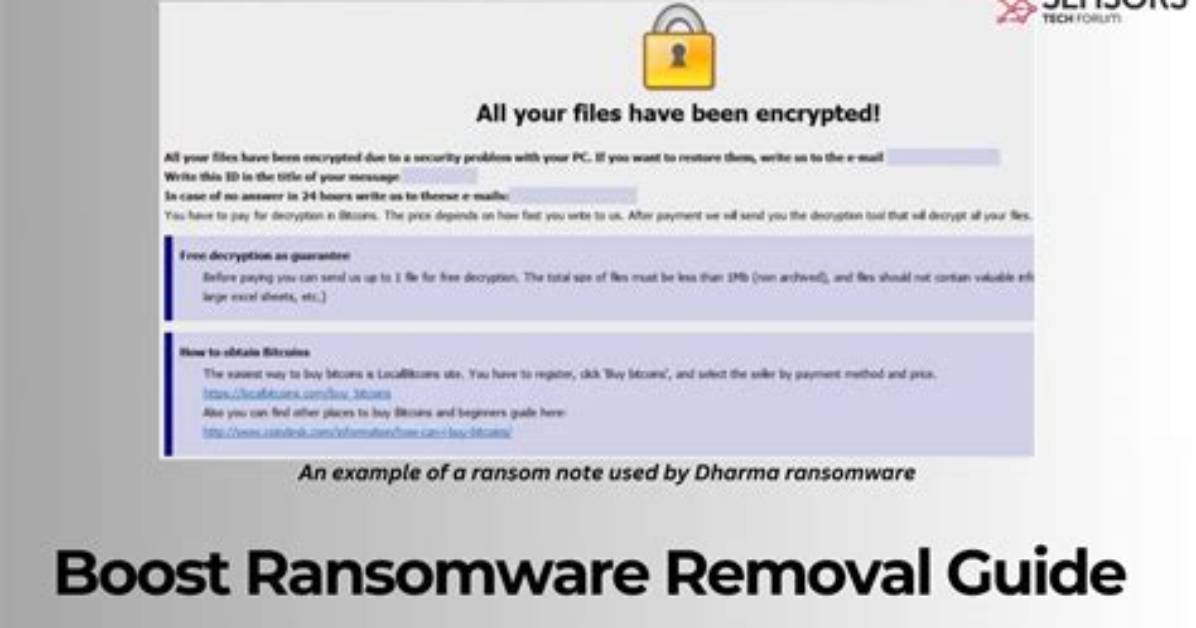
In each directory containing the encoded files, a FILES ENCRYPTED.txt text file will be found. It is a ransom money memo. It contains information on the ways of contacting the racketeers and some other information. The ransom note usually contains a description of how to purchase the decryption tool from the Info developers. You can obtain this decrypting software after contacting through email. That is it.
| Name | Info Virus |
| Ransomware family1 | Dharma ransomware |
| Extension | .info |
| Ransomware note | FILES ENCRYPTED.txt |
| Contact | |
| Detection2 | Win32/RiskWare.PEMalform.B, Ransom:Win32/StopCrypt.PBX!MTB, MSIL/Kryptik.AEXH |
| Symptoms | Your files (photos, videos, documents) get a .info extension and you can’t open them. |
| Fix Tool | See If Your System Has Been Affected by Info virus |
The FILES ENCRYPTED.txt document accompanying the Info malware provides the following frustrating information:
all your data has been locked us
You want to return?
write email  or
In the picture below, you can see what a folder with files encrypted by the Info looks like. Each filename has the “.info” extension added to it.
How did my machine catch Info ransomware?
Nowadays, there are three most exploited methods for tamperers to have the Info virus settled in your digital environment. These are email spam, Trojan injection and peer-to-peer file transfer.
If you access your mailbox and see letters that look like familiar notifications from utility services companies, delivery agencies like FedEx, web-access providers, and whatnot, but whose mailer is strange to you, beware of opening those letters. They are very likely to have a malicious file enclosed in them. Therefore, it is even more dangerous to open any attachments that come with letters like these.
Another option for ransom hunters is a Trojan file scheme3. A Trojan is a program that gets into your machine disguised as something else. For example, you download an installer of some program you want or an update for some program. However, what is unpacked reveals itself a harmful agent that encodes your data. As the update wizard can have any name and any icon, you’d better be sure that you can trust the resource of the files you’re downloading. The optimal thing is to use the software developers’ official websites.
As for the peer file transfer protocols like BitTorrent or eMule, the danger is that they are even more trust-based than the rest of the Internet. You can never know what you download until you get it. So you’d better be using trustworthy websites. Also, it is reasonable to scan the folder containing the downloaded files with the antivirus as soon as the downloading is complete.
Maya is a hardware enthusiast who tests and reviews smart home devices, smartphones, wearables, and audio gear. She focuses on practical consumer value and build quality.
