
Launching Mainview Explorer - Documentation for Bmc Ami Ops Infrastructure 7.0

You Launch Mainview Explorer by Using Java Web Start from Any Web Browser to Launch Individual Mainview Explorer Sessions That Are Saved as Shortcuts to Your...
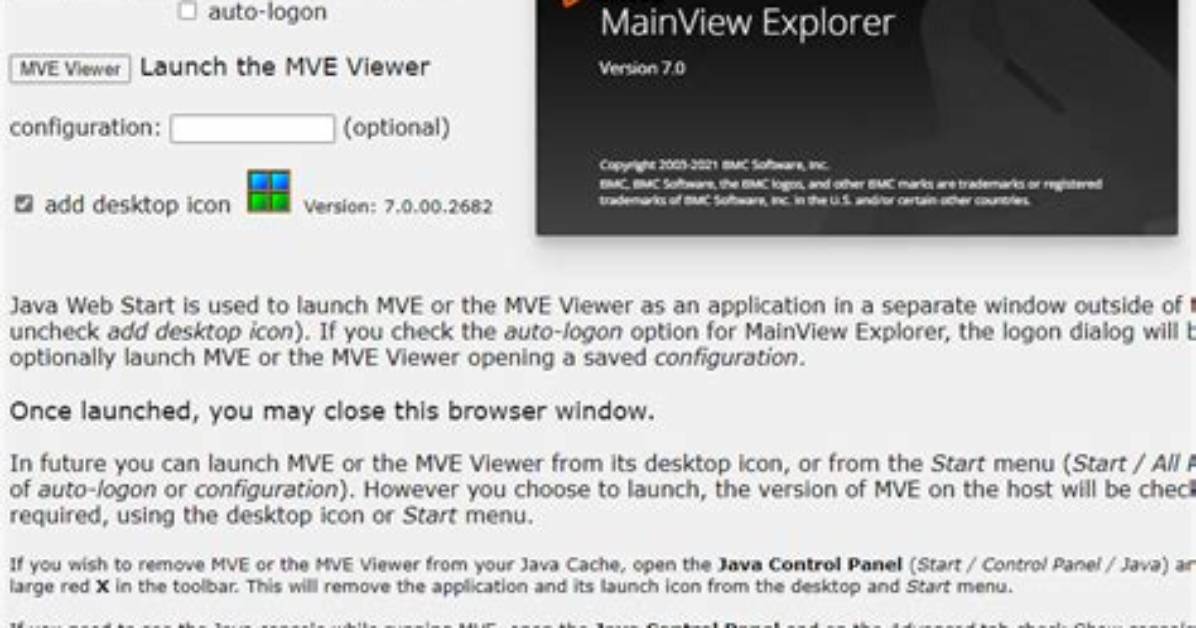
You launch MainView Explorer by using Java Web Start from any web browser to launch individual MainView Explorer sessions that are saved as shortcuts to your desktop.
Make sure that you have Java 8 or later already installed on your PC.
To launch MainView Explorer using Java Web Start
- Open any browser and enter the URL: http://host:port/mve.
- For host, use the IP address or name of the system on which the Host Server is running.
- For port, use the value specified for the PORT parameter in the Host Server startup procedure. For more information, see Creating the Host Server startup procedure.
- Press Enter.
A web page appears with two launch buttons: one for MainView Explorer and one for MainView Explorer Viewer. - Click the launch button for
MainView Explorer
.
A new window opens and prompts you to log on. To start your MainView Explorer session, see Logging on to MainView Explorer.
Tip
After you launch MainView Explorer using Java Web Start, a shortcut appears on your desktop that you can use to launch MainView Explorer in the future.
Must Read
Running MainView Explorer with IBM AT-TLS
You can run MainView Explorer in secure mode (https) using IBM Application Transparent Transport Layer Security (AT-TLS). You define the security parameters for AT-TLS in the Host Server startup procedure. For more information, see Creating the Host Server startup procedure. The ATTLS=Y parameter value is used when the user is authorized to access the Host Server .
However, while running the MainView Explorer with ATTLS=D or ATTLS=R parameter values that allows a client certificate to be used, the client certificate needs to be registered into the z/OS security manager (for example, IBM RACF, CA ACF2, or CA TSS).
For more information about the certificate registration, contact your z/OS security administrators.
The following Policy Agent AT-TLS configuration sample shows the required client certification:
TTLSEnvironmentAction eAct1~MVE_ClientAuth
{
TTLSEnvironmentAdvancedParms
{
ClientAuthType PassThru #Client certificate is requested
ApplicationControlled Off
}
HandshakeRole ServerWithClientAuth #Application verifies the certificate
TTLSKeyringParmsRef keyMVE01
}
Related topics
Chloe Bennett explores the intersection of pop culture, streaming entertainment, digital trends, and contemporary lifestyle. Her weekly commentary reaches thousands of culture enthusiasts.
