
Ldap Server Which Is My Base Dn

Hello I'm Trying to Use My Ldap Test Server in Order to Authenticate Users in Openca. I'm Currently Connecting Through Phpldapadmin with: Login Dn: Cn=Admin...
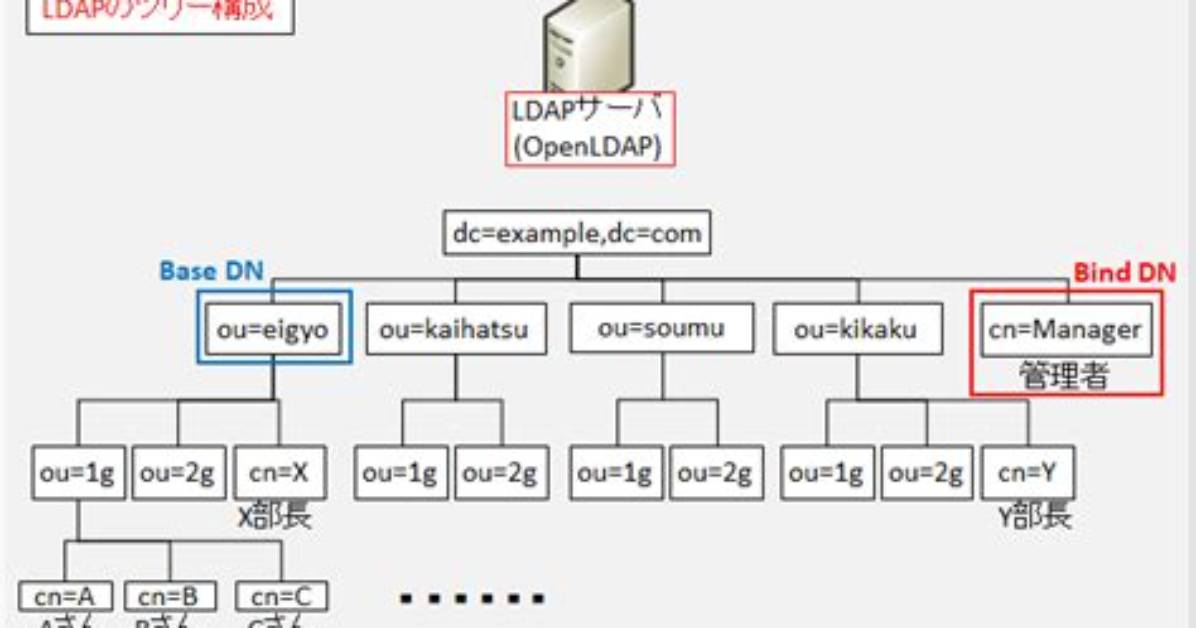
Hello I'm trying to use my ldap test server in order to authenticate users in openca.
I'm currently connecting through phpldapadmin with :
Login DN : cn=admin,dc=example,dc=com
Password : mypass
but on openca something is going wrong... in datasources.xml I found the settings of the ldap configuration and it asks for
<name>basedn</name>
which is the basedn for me ? I already tried
cn=admin,dc=example,dc=com
and
dc=example,dc=com
I can connect to my ldap with LDAP Admin explorer too.
Thanks !
2 Answers
The base dn is dc=example,dc=com.
I don't know about openca, but I will try this answer since you got very little traffic so far.
A base dn is the point from where a server will search for users. So I would try to simply use admin as a login name.
If openca behaves like most ldap aware applications, this is what is going to happen :
- An ldap search for the user
adminwill be done by the server starting at the base dn (dc=example,dc=com). - When the user is found, the full dn (
cn=admin,dc=example,dc=com) will be used to bind with the supplied password. - The ldap server will hash the password and compare with the stored hash value. If it matches, you're in.
Getting step 1 right is the hardest part, but mostly because we don't get to do it often. Things you have to look out for in your configuraiton file are :
- The
dnyour application will use to bind to the ldap server. This happens at application startup, before any user comes to authenticate. You will have to supply a full dn, maybe something likecn=admin,dc=example,dc=com. - The authentication method. It is usually a "simple bind".
- The user search filter. Look at the attribute named
objectClassfor youradminuser. It will be eitherinetOrgPersonoruser. There will be others liketop, you can ignore them. In your openca configuration, there should be a string like(objectClass=inetOrgPerson). Whatever it is, make sure it matches your admin user's object Class. You can specify two object class with this search filter(|(objectClass=inetOrgPerson)(objectClass=user)).
Download an LDAP Browser, such as Apache's Directory Studio. Connect using your application's credentials, so you will see what your application sees.
Either you set LDAP_DOMAIN variable or you misconfigured it. Jump inside of ldap machine/container and run:
slapcat > backup.ldif
If it fails, check punctuation, quotes etc while you assigned variable "LDAP_DOMAIN" Otherwise you will find answer inside on backup.ldif file.
Elena Rostova holds a Master's degree in Public Health Journalism. She covers groundbreaking medical research, holistic wellness trends, mental health awareness, and nutritional science.
