
Lokd Virus (. Lokd Files) – Decrypt & Removal

What Is “Lokd”? Ransomware Is a Specific Kind of Virus That Encrypts Your Documents and Then Forces You to Pay to Restore Them. Djvu (Aka Stop) Ransomware...
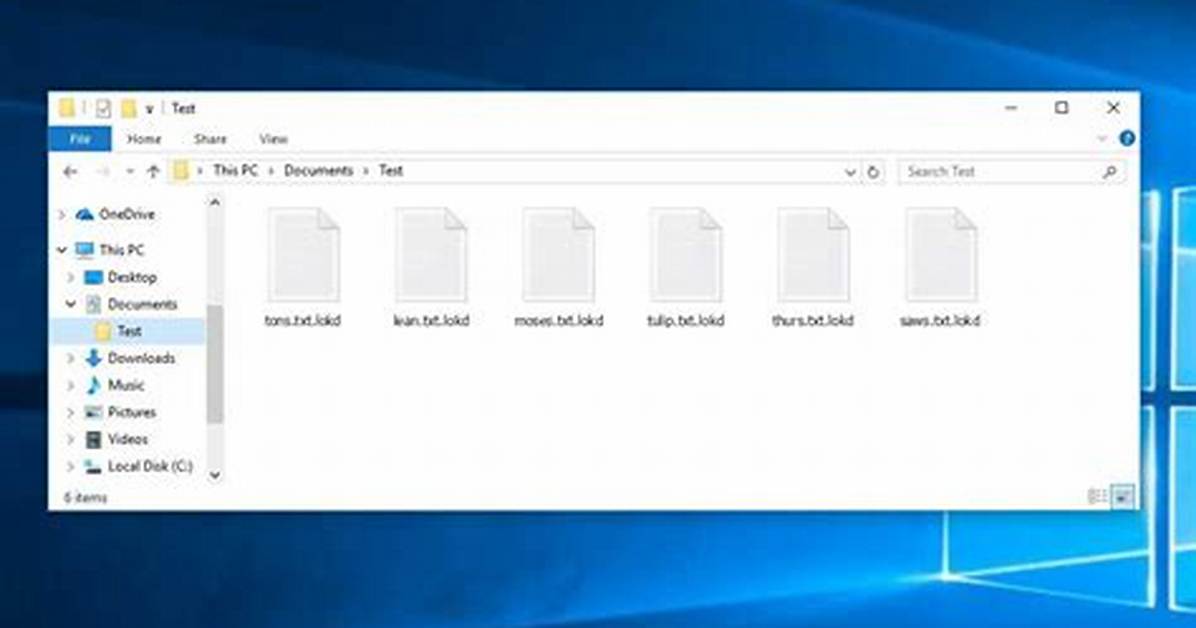
What is “Lokd”?
Ransomware is a specific kind of virus that encrypts your documents and then forces you to pay to restore them. DJVU (aka STOP) ransomware family was first revealed and analyzed by virus analyst Michael Gillespie">2.
Lokd is similar to other representatives of the same family: Rezm, Rezm, Nppp. It encrypts all popular file types. Hence, you cannot work with the your documents or photos, and all external drives you connected or connecting to infected PC will be encrypted, too. Lokd adds its particular “.lokd” extension into all files. For instance, the file “video.avi”, will be amended into “video.avi.lokd”. As soon as the encryption is accomplished, Lokd drops a special text file “_readme.txt” and puts it into all folders that contain the modified files.
| Ransomware family3 | DJVU/STOP4 ransomware |
| Extension | .lokd |
| Ransomware note | _readme.txt |
| Ransom | From $490 to $980 (in Bitcoins) |
| Contact | , |
| Detection5 | Win64:TrojanX-gen [Trj], Win64/Packed.Themida.IL, Graftor.636898 |
| Symptoms | Your files (photos, videos, documents) have a .lokd extension and you can’t open it |
| Fix Tool | See If Your System Has Been Affected by .lokd file virus |
This text asking payment is for restore files via decryption key:
The scary alert demanding from users to pay the ransom to decrypt the compromised data contains these frustrating warnings
The cryptography algorithm used by Lokd is AES-256. So, if your documents got encrypted with a specific decryption key, which is totally unique and there are no other copies. The sad reality is that it is impossible to restore the information without the unique key available.
In case if Lokd worked in online mode, it is impossible for you to gain access to the AES-256 key. It is stored on a remote server owned by the criminals who promote the Lokd ransomware. It could be a solution to turn your Internet connection off and use a decryptor to get your files back, but as soon as you will be back online, the ransomware will get another command to encrypt your files.
For receiving decryption key the payment should be $980. To obtain the payment details the victims are encouraged by the message to contact the frauds by email (), or via Telegram.
Do not pay for Lokd!
_readme.txt file also indicates that the computer owners must get in touch with the Lokd representatives during 72 hours starting from the moment of files where encrypted. On the condition of getting in touch within 72 hours, users will be granted a 50% rebate, thus the ransom amount will be minimized down to $490). Sometimes, distributors can start a chat with their victim, trying to force him/her to pay. Nonetheless, stay away from paying the ransom!
I strongly recommend you not to contact these crooks and not to pay them a penny. The one of the most real working solution to recover the lost data – just using the available backups, or use Decrypter tool in combination with Anti-Malware software.
The peculiarity of all such viruses apply a similar set of actions for generating the unique decryption key to recover the ciphered data. And only this frauds have an access to this key.
Thus, unless the ransomware is still under the stage of development or possesses with some hard-to-track flaws, manually recovering the ciphered data is a thing you can’t really perform. The only solution to prevent the loss of your valuable data is to regularly make backups of your crucial files.
Note that even if you do maintain such backups regularly, they ought to be put into a specific location without loitering, not being connected to your main workstation.
For instance, the backup may be kept on the USB flash drive or some alternative external hard drive storage. Optionally, you may refer to the help of online (cloud) information storage.
Needless to mention, when you maintain your backup data on your common device, it may be similarly ciphered as well as other data, so you will lost a chance to recover your data without external software interruption.
Another problem that could appear in process of system recovery via backup is a probability of ransomware precense in backup files. Ransomware can be asleep for a long time, so in some time user can find out that he was been attacked, again, and even without downloading anything. Even more, the ransomware can launch once user finished his backup, because “launch encrypting” command is already sent from fraudsters’ command server , and as soon as user’s PC getting online, ransomware will get “launch encrypting” command.
Also, some users, generally with weak PC, detected an unusuall activity on their machines via awful slowdown of their computers, that are already performing low. So, if you detected an unusuall lagspikes for your machine – wait for bad news and .lokd extensions on your files.
For this reason, locating the backup on your main device is surely not a wise idea.
Sophia analyzes international trade, startup ecosystems, retail transformation, and supply chain logistics for modern digital publications.
