
Nginx Redirect to Docker Container

I Made My Personal Server Ssl Encrypted, So That Only Port 443 Is Accessible to the Outside World. However, in Doing So, I Locked My Web Apps from Seeing the...
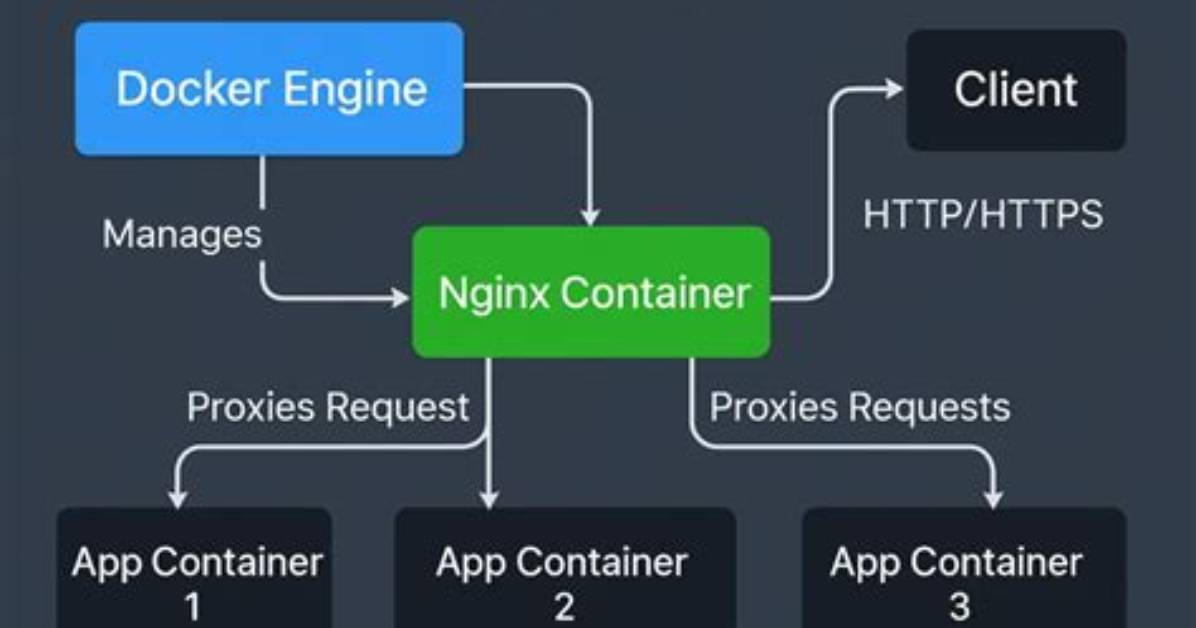
I made my personal server SSL encrypted, so that only port 443 is accessible to the outside world. However, in doing so, I locked my web apps from seeing the outside world.
The gist of it is that I have two Docker chains such that <domain>:2019 and <domain>:2020 are two separate web applications that are each served with Nginx containers, and output correctly on my local machine. I want to have <domain>:2019 output to example1.com and <domain>:2020 output to example2.com from using the host machine's Nginx service. How would I go about doing this?
[edit]
The Docker chains have respective Nginx containers that look like:
  nginx:
    container_name: domain_nginx
    build:
      context: ./nginx
    volumes:
      - static_volume:/usr/src/domain_django/static
    ports:
      - "2019:80"
    depends_on:
      - django
Where the Nginx container outputs to 127.0.0.1:2019. I want a user going to example1.com to see the 127.0.0.1:2019
1 Answer
just need to use the name of the container name / services since you are using docker-compose. Try adding this configuration to your container with nginx:
http {
    include /etc/nginx/mime.types;
    ssl_session_cache   shared:SSL:10m;
    ssl_session_timeout 10m;
    server {
        listen 80 default_server;
    listen [::]:80;
        server_name  example1.com  example2.com;
        return 301
    }
    server {

         listen 443 ssl default_server;
         listen [::]:443 ssl default_server;


        server_name  example1.com;

        ssl_certificate ssl/fullchain1.pem;
        ssl_certificate_key ssl/privkey1.pem;
        ssl_protocols       TLSv1 TLSv1.1 TLSv1.2;

        keepalive_timeout   70;

        location / {
                proxy_pass  ###<-------HERE you can use webapp
                proxy_set_header Host $host;
                proxy_set_header X-Real-IP $remote_addr;
                proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        }


        server {

         listen 443 ssl default_server;
         listen [::]:443 ssl default_server;


        server_name  example2.com;

        ssl_certificate ssl/fullchain2.pem;
        ssl_certificate_key ssl/privkey2.pem;
        ssl_protocols       TLSv1 TLSv1.1 TLSv1.2;

        keepalive_timeout   70;

        location / {
                proxy_pass  ###<-------HERE you can use webapp
                proxy_set_header Host $host;
                proxy_set_header X-Real-IP $remote_addr;
                proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        }

}
Example of old docker-compose
version: '2'
services:
    # webapp is the name that you can use inside the nginx configuration
    webapp:
        build: build
        volumes:
            - .:/home/noc/app
        ports:
            - 8000:8000
        environment:
            - RECAPTCHA_SECRET_KEY=****
            - RECAPTCHA_SITE_KEY=****
            - DB_HOST=******

    nginx:
        image: nginx:1.10.2
        volumes:
            - ./static:/var/www/static
            - ./config/nginx.conf:/etc/nginx/nginx.conf
            - /etc/letsencrypt/archive/:/etc/nginx/ssl
        links:
            - webapp
        depends_on:
            - webapp
        ports:
            - 80:80
            - 443:443
        command: /bin/bash -c "nginx -g 'daemon off;'"
More information: Docker documentation
Robert Thorne covers electric vehicle innovations, autonomous driving systems, global mobility trends, and automotive engineering developments.
