
Oauth2-Proxy: Validate Azure Ad Jwt Token Returns 401

I Am Trying to Validate Jwt Token with Oauth2-Proxy and Azure Ad (Multi Tenant). the Setup Is Working and I Can Log in Via. This Is How I Run the Proxy: Docker...
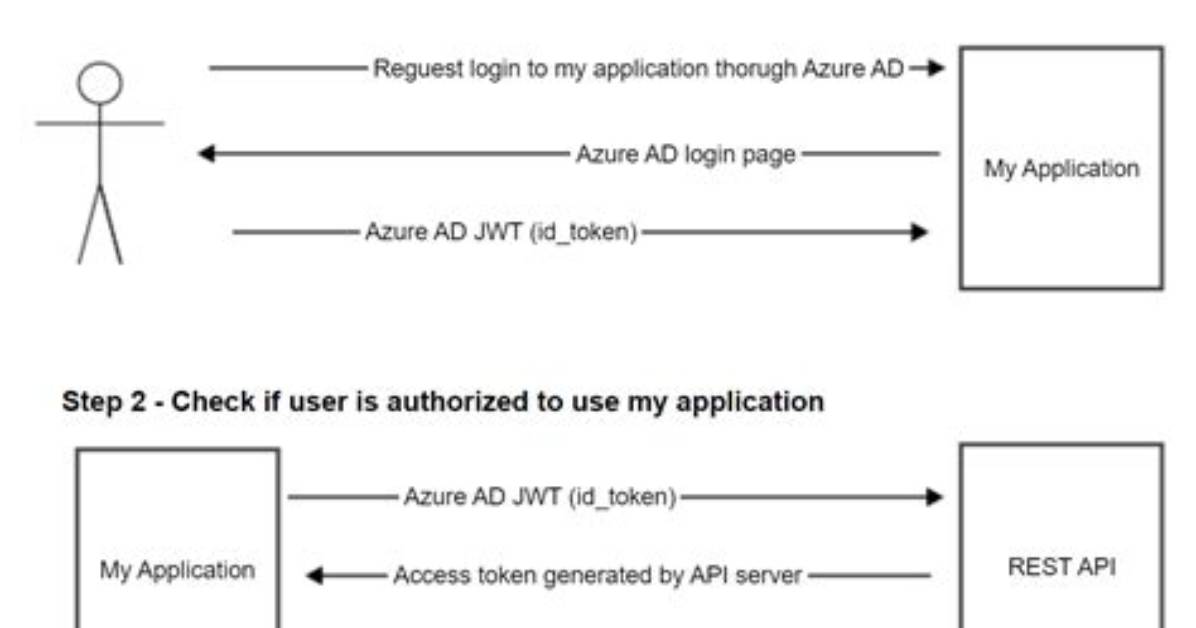
I am trying to validate JWT Token with oauth2-proxy and Azure AD (multi tenant). The setup is working and I can log in via . This is how I run the proxy:
docker run --net=host  \
--provider=oidc \
--oidc-issuer-url= \
--insecure-oidc-skip-issuer-verification=true \
--scope=[REDACTED] \
--oidc-email-claim=preferred_username \
--email-domain="*" \
--client-secret=[REDACTED] \
--client-id=[REDACTED] \
--cookie-secret=[REDACTED] \
--redirect-url="" \
--pass-access-token=true \
--pass-authorization-header=true \
--upstream=file:///dev/null \
--pass-user-headers=true \
--auth-logging=true \
--standard-logging=true \
--request-logging=true
I made a small NextJS application with React MSAL so I can get my JWT token. I even verified it at and everything looks okay.
Problem occurs when I want to check validity of token. I send a request to via Insomnia and add the Authorization: Bearer <token> header, but I constantly get 401.
How can I get 202 and the token accepted? What am I doing wrong? I can not any information as to what oauth2/auth expects from me. Again, I am certain the token is valid, but I do not know how to pass it to oauth2/auth.
I am open to any solutions to validate this JWT token. I just want to either get 202 or 401. The final solution will be connected to nginx.
Must Read
Know someone who can answer? Share a link to this question via email, Twitter, or Facebook.
Robert Thorne covers electric vehicle innovations, autonomous driving systems, global mobility trends, and automotive engineering developments.
