
On Owasp Top 10?

What Are the Latest Owasp Top 10 Categories? Injection. .. . Broken Authentication. .. . Sensitive Data Exposure. .. . Xml External Entities (Xxe). .. . Broken...
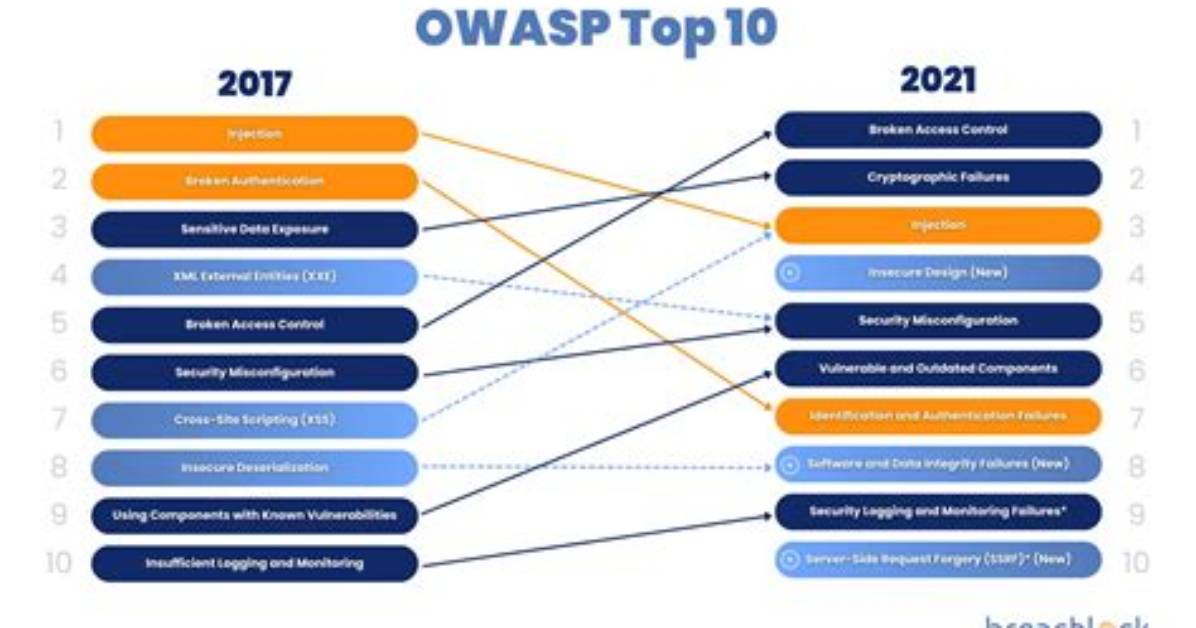
What are the latest OWASP Top 10 categories?
- Injection. ...
- Broken Authentication. ...
- Sensitive Data Exposure. ...
- XML External Entities (XXE). ...
- Broken Access Control. ...
- Security Misconfiguration. ...
- Cross-Site Scripting (XSS). ...
- Insecure Deserialization.
Which vulnerabilities are part of the OWASP Top Ten?
The Top 10 OWASP vulnerabilities in 2021 are:
- Injection.
- Broken authentication.
- Sensitive data exposure.
- XML external entities (XXE)
- Broken access control.
- Security misconfigurations.
- Cross site scripting (XSS)
- Insecure deserialization.
What is the OWASP Top 10 and why is it important?
The OWASP Top 10 is a standard awareness document for developers and web application security. It represents a broad consensus about the most critical security risks to web applications. Globally recognized by developers as the first step towards more secure coding.
David Miller brings 15 years of experience in global economics, personal finance strategy, and market dynamics. He specializes in turning complex economic trends into actionable insights for everyday readers.
