
Pingfederate Oauth 2.0 Custom Grant to Get Access / Refresh Token?

We Are Setting up a Oauth 2.0 via Pingfederate in Our Organization. the Scenario in Question Is as Follows - We Have a Website in Which the Customer Would Be...
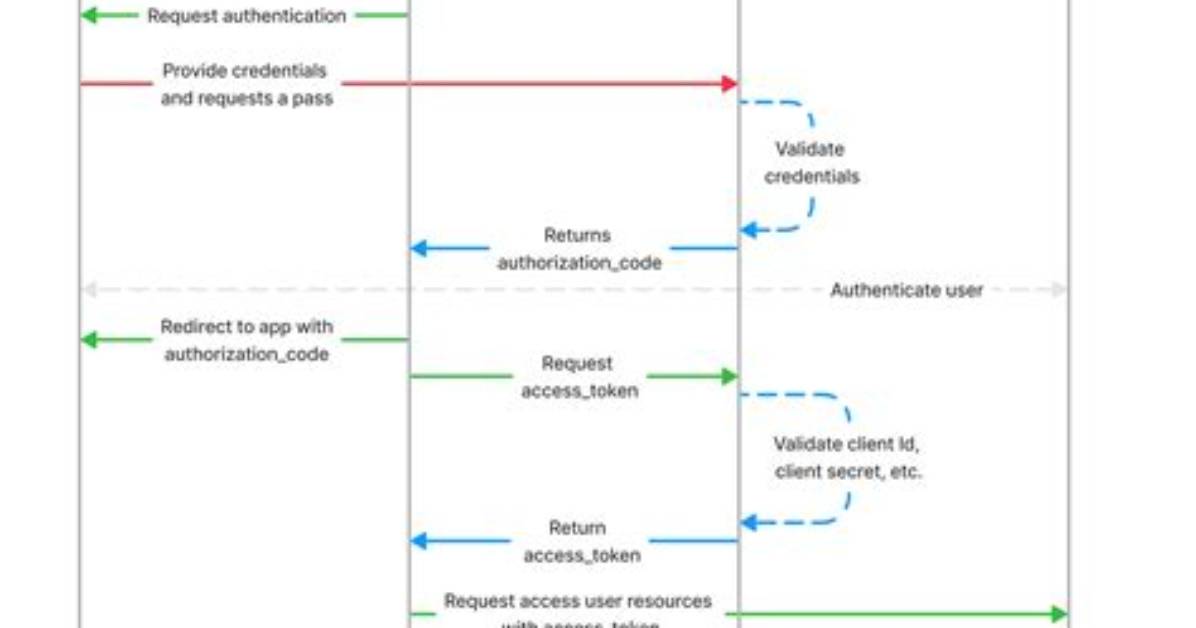
We are setting up a OAuth 2.0 via PingFederate in our organization. The scenario in question is as follows - We have a website in which the customer would be logging in using user name and password. There are are also links within the site to redirect the customer to a partner site. The partner site would be securely passed some basic information via SSO payload.
The partner site would also need to be able to call back to our Apis (call made in the background) to get additional information about our customer which they will then use to display on their site.
Our Api’s are currently setup to be accessed via access token which the consumers of the Api get by following the Authorization Grant flow.
In the partner redirect scenario we want partner site not go through the Authorization code flow when it makes the Api call because the customer would have already logged into our site to start with using their credentials but instead when we redirect to the partner site provide it securely (SSO payload) the access and refresh token which it can then use to make the Api calls ?.
Is there a grant type that I can invoke telling my authorization provider (PingFederate) that I trust the customer based on the information that he has already provided now give me access token and refresh token and then redirect using that information (None of the grant types that I am aware is able to support it - does Ping OAuth setup support a flow wherein I can say I trust this customer give me access and refresh token )?
1 Answer
It sounds like you'd be combining SAML and OAuth to meet your business need. While it's not defined as a standard grant type, one potential solution is to include an Access Token in the SAML Assertion attribute payload so the partner application can then make calls without going through additional redirects. PingFederate does offer the ability to do this by using OGNL to create an access token in the attribute contract fulfillment. An example of how to do this is in our SDK documentation:
If you need more guidance on selecting the right OAuth grant type, we have information on our developer portal that covers this. Please refer to:
James Sterling reports on renewable energy developments, climate policy, ecological conservation, and green tech innovations around the globe.
