
Question: How Do I Read a Tcpdump File in Linux?

Contents the “-R” Option Lets You Read the Output of a File. All You Have to Do Is Use the “-R” Option with Tcpdump Command and Specify the Path of the File...
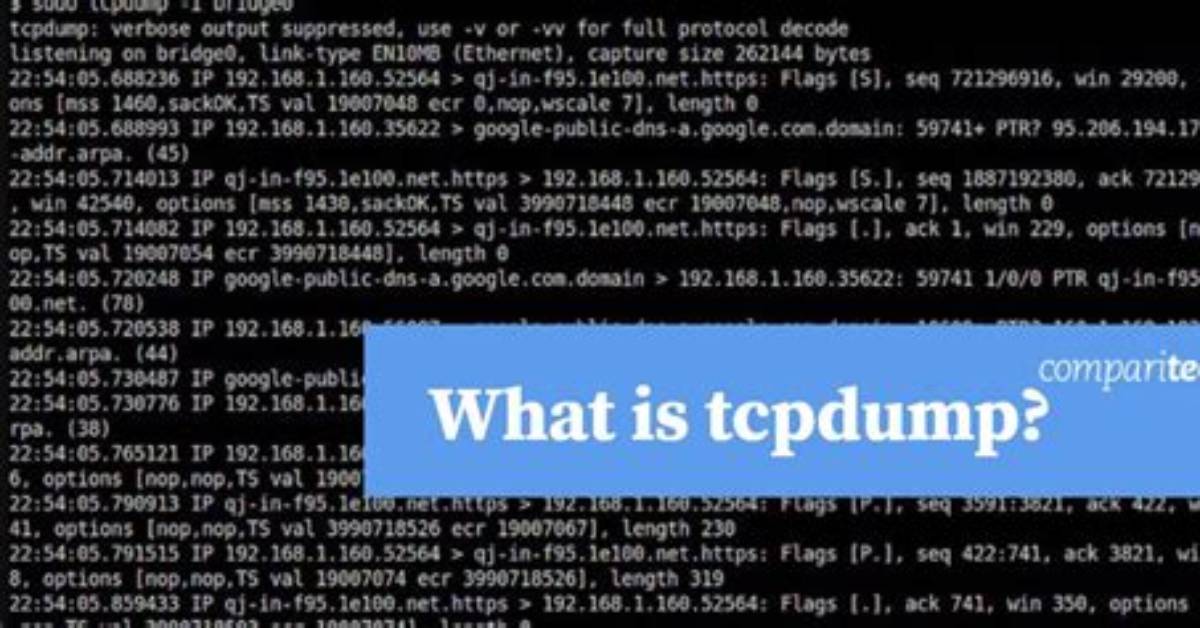
The “-r” option lets you read the output of a file. All you have to do is use the “-r” option with tcpdump command and specify the path of the file you want to read.
How do I read a tcpdump file?
What does the tcpdump output look like?
- Unix timestamp ( 20:58:26.765637 )
- protocol (IP)
- the source hostname or IP, and port number ( 10.0.0.50.80 )
- destination hostname or IP, and port number ( 10.0.0.1.53181 )
- TCP Flags ( Flags [F.] ). …
- Sequence number of the data in the packet. ( …
- Acknowledgement number ( ack 2 )
Must Read
How does tcpdump work in Linux?
Tcpdump uses libpcap library to capture the network packets & is available on almost all Linux/Unix flavors. Tcpdump command can read the contents from a network interface or from a previously created packet file or we can also write the packets to a file to be used for later.
Maya is a hardware enthusiast who tests and reviews smart home devices, smartphones, wearables, and audio gear. She focuses on practical consumer value and build quality.
