
Ransom: Win32/Stopcrypt! Ml

What Is Ransom: Win32/Stopcrypt! Ml Infection? in This Short Article You Will Certainly Discover Concerning the Interpretation of Ransom: Win32/Stopcrypt! Ml...
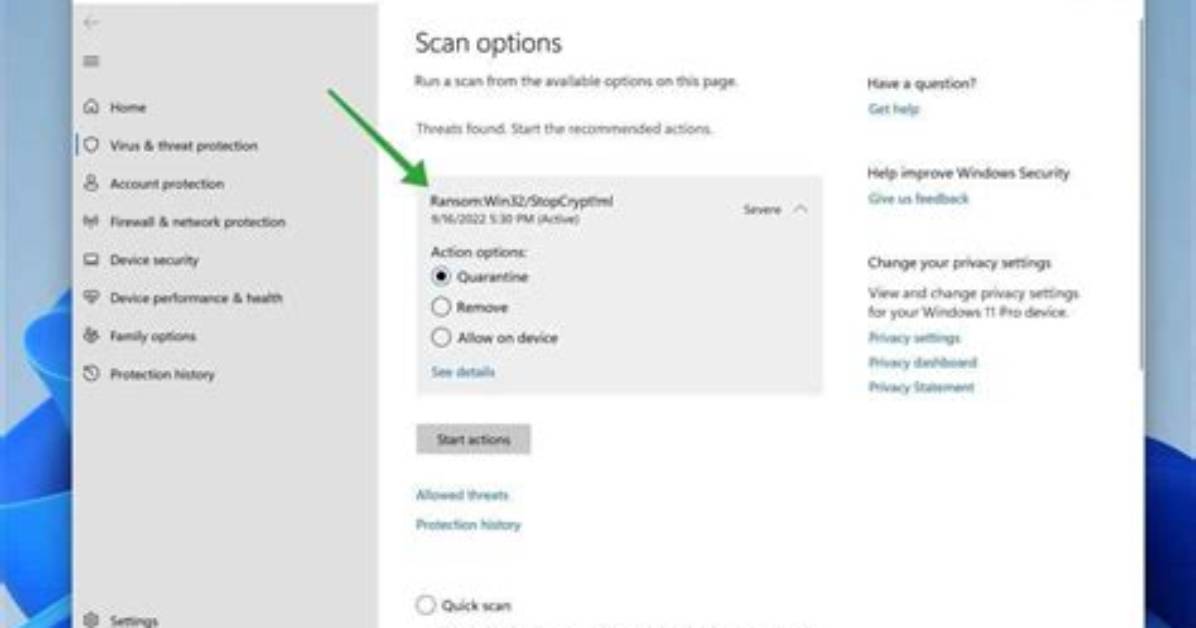
What is Ransom:Win32/StopCrypt!ml infection?
In this short article you will certainly discover concerning the interpretation of Ransom:Win32/StopCrypt!ml and also its adverse impact on your computer system. Such ransomware are a kind of malware that is clarified by on the internet frauds to require paying the ransom money by a victim.
Most of the situations, Ransom:Win32/StopCrypt!ml ransomware will instruct its victims to start funds move for the purpose of reducing the effects of the changes that the Trojan infection has presented to the sufferer’s gadget.
Ransom:Win32/StopCrypt!ml Summary
These adjustments can be as adheres to:
- A process attempted to delay the analysis task.;
- Reads data out of its own binary image;
- Drops a binary and executes it;
- Performs some HTTP requests;
- Creates or sets a registry key to a long series of bytes, possibly to store a binary or malware config;
- Installs itself for autorun at Windows startup;
- Network activity detected but not expressed in API logs;
- Anomalous binary characteristics;
- Ciphering the papers found on the target’s hard drive — so the victim can no longer use the information;
- Preventing routine accessibility to the target’s workstation;
Related domains:
| z.whorecord.xyz | Ransom:Win32/StopCrypt!ml |
| a.tomx.xyz | Ransom:Win32/StopCrypt!ml |
| edgedl.me.gvt1.com | Ransom:Win32/StopCrypt!ml |
Ransom:Win32/StopCrypt!ml
One of the most typical networks whereby Ransom:Win32/StopCrypt!ml Ransomware are infused are:
- By ways of phishing e-mails;
- As a repercussion of individual ending up on a source that organizes a malicious software;
As quickly as the Trojan is efficiently injected, it will certainly either cipher the information on the sufferer’s computer or avoid the gadget from operating in a proper way – while likewise positioning a ransom money note that discusses the need for the targets to impact the payment for the function of decrypting the files or recovering the file system back to the first problem. In many instances, the ransom money note will turn up when the client restarts the PC after the system has currently been harmed.
Ransom:Win32/StopCrypt!ml circulation networks.
In different corners of the globe, Ransom:Win32/StopCrypt!ml expands by jumps as well as bounds. Nevertheless, the ransom notes as well as methods of obtaining the ransom amount might vary depending on specific local (regional) setups. The ransom money notes and also techniques of extorting the ransom money amount may differ depending on certain local (regional) setups.
For example:
Faulty alerts about unlicensed software program.
In specific areas, the Trojans typically wrongfully report having found some unlicensed applications enabled on the target’s gadget. The alert then requires the customer to pay the ransom money.
Faulty statements about unlawful material.
In countries where software application piracy is much less preferred, this method is not as efficient for the cyber fraudulences. Alternatively, the Ransom:Win32/StopCrypt!ml popup alert may wrongly assert to be originating from a law enforcement establishment as well as will report having located kid porn or various other unlawful information on the gadget.
Ransom:Win32/StopCrypt!ml popup alert may wrongly assert to be acquiring from a law enforcement institution and also will certainly report having situated youngster porn or other illegal information on the tool. The alert will likewise have a need for the user to pay the ransom money.
Must Read
Technical details
File Info:
crc32: 0980CDE7md5: 4e9e166624356d7d99813f2755a6f28bname: 4E9E166624356D7D99813F2755A6F28B.mlwsha1: a68bb8711585ad6886ef7b9d1fc2bb9ad574cf5dsha256: c71c941475802991d7de9103f418b0e412d0df86bc9ecb13eb117a5aa08a6541sha512: 2fa870e88ad40bea38ab043d64acf959ab74aab4185293a967b8bd535055bac2b72720d535f680b66afde614ce74b2ffbfcee26855adf92f2f5f35edb3663338ssdeep: 49152:33FhzsDIiKqkNx58uW1j192jhITxl51bJQKI:F5+IZhxUpiyxX1TItype: PE32 executable (GUI) Intel 80386, for MS Windows, Nullsoft Installer self-extracting archiveVersion Info:
ProductName: qptyvsaqihFileDescription: guedcfbzeieOriginalFilename: womgfmeweoCompanyName: ckdljvpsmqTranslation: 0x0409 0x04b0
Ransom:Win32/StopCrypt!ml also known as:
| GridinSoft | Trojan.Ransom.Gen |
| Bkav | W32.AIDetect.malware2 |
| Elastic | malicious (high confidence) |
| ALYac | Dropped:Trojan.GenericKD.46131044 |
| Cylance | Unsafe |
| Zillya | Adware.Generic.Win32.8024 |
| Sangfor | Trojan.Win32.Save.a |
| CrowdStrike | win/malicious_confidence_100% (D) |
| K7GW | Adware ( 005375181 ) |
| K7AntiVirus | Adware ( 005375181 ) |
| Symantec | ML.Attribute.HighConfidence |
| ESET-NOD32 | multiple detections |
| APEX | Malicious |
| Avast | Win32:Adware-gen [Adw] |
| Cynet | Malicious () |
| Kaspersky | not-a-virus:HEUR:AdWare.Win32.Hpdefender.gen |
| BitDefender | Dropped:Trojan.GenericKD.46131044 |
| NANO-Antivirus | Riskware.Win32.HPDefender.ffivfg |
| MicroWorld-eScan | Dropped:Trojan.GenericKD.46131044 |
| Tencent | Win32.Adware.Generic.Pgnm |
| Ad-Aware | Dropped:Trojan.GenericKD.46131044 |
| Sophos | Generic PUA KG (PUA) |
| Comodo | ApplicUnwnt@#2ddec42gyp3he |
| BitDefenderTheta | Gen:NN.ZexaF.34058.Fy0@aSw4DOki |
| VIPRE | Trojan.Win32.Generic!BT |
| TrendMicro | TROJ_GEN.R002C0PDJ21 |
| McAfee-GW-Edition | BehavesLike.Win32.Browser.tc |
| FireEye | Generic.mg.4e9e166624356d7d |
| Emsisoft | Dropped:Trojan.GenericKD.46131044 (B) |
| SentinelOne | Static AI – Malicious PE |
| Avira | HEUR/AGEN.1117983 |
| Microsoft | Ransom:Win32/StopCrypt!ml |
| ZoneAlarm | not-a-virus:HEUR:AdWare.Win32.Generic |
| GData | Dropped:Trojan.GenericKD.46131044 |
| AhnLab-V3 | PUP/Win32.HPDefender.R231831 |
| McAfee | ICLoader |
| MAX | malware (ai score=98) |
| VBA32 | Trojan.Tiggre |
| Malwarebytes | Malware.AI.1110499809 |
| Panda | Trj/Genetic.gen |
| TrendMicro-HouseCall | TROJ_GEN.R002C0PDJ21 |
| Rising | Trojan.Generic@ML.100 (RDML:1JN4g//fuxGNdz7shg7dAA) |
| Yandex | PUA.HPDefender!OIsGrAnrIRU |
| Fortinet | W32/Generic_PUA_DE |
| AVG | Win32:Adware-gen [Adw] |
| Paloalto | generic.ml |
| Qihoo-360 | Win32/Adware.Generic.HyoDEpsA |
James Sterling reports on renewable energy developments, climate policy, ecological conservation, and green tech innovations around the globe.
