
Simple Way to Validate Android App Integrity

I Want to Detect Any Tampering in the Apk File and Validate the App or Built Integrity. When I Searched Online I Got This Solution from Official Sources...
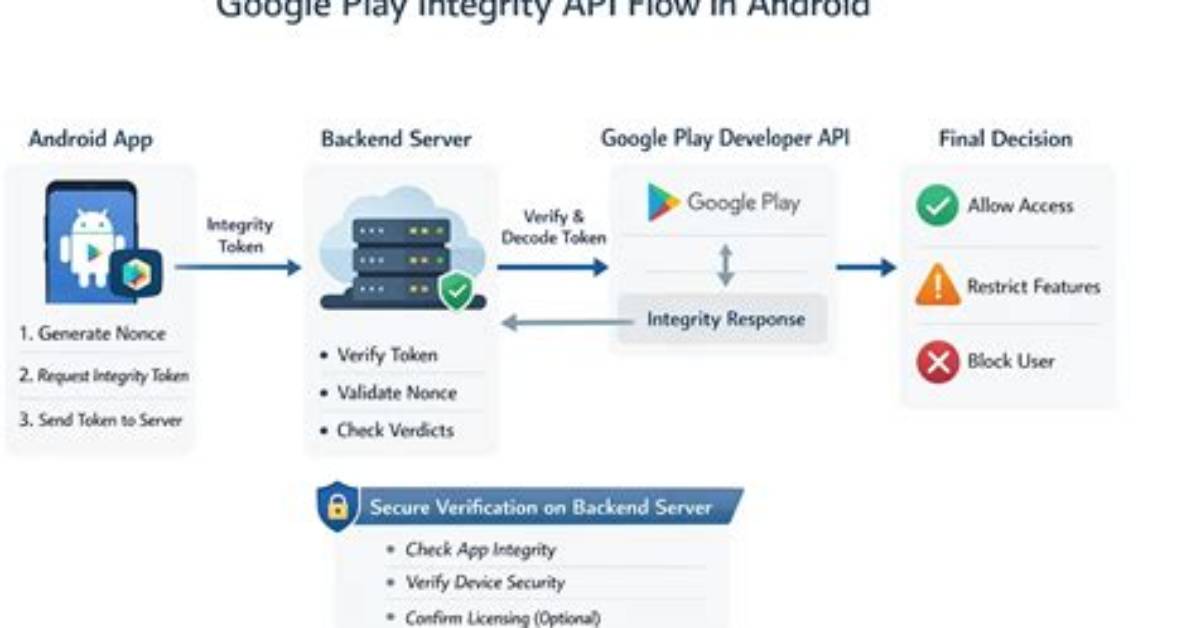
I want to detect any tampering in the APK file and validate the App or Built integrity. When I searched online I got this solution from official sources -
However it looks little too much to implement and involves changes on the server side as well. Hence I looked into another solution i.e finding out the signature of current keystore that is used to sign my Application and send it to the backend(which already has the original signature before uploading the build to PlayStore) to validate.
Sample code:
SigningInfo signingInfo = getPackageManager()
              .getPackageInfo(getPackageName(), PackageManager.GET_SIGNATURES)
              .signingInfo;
signingInfo.getApkContentsSigners();
//Send the information to backend to check if matches our original release.keystore signature
- Is there is any downside to the above simple code to check for APK integrity?
- If there aren't any then - What is the reason Goggle recommends Play Integrity API instead of this simple solution
1 Answer
Must Read
Your Problem
However it looks little too much to implement and involves changes on the server side as well.
Securing a mobile app is a very complex task and when done only on the client side allows for an attacker to bypass any decision made regarding its integrity.
Attackers can use reverse engineer techniques to decompile your mobile app and tamper with it or they can use an instrumentation framework to hook into your code at runtime to change its behaviour and/or extract whatever its required to then automate attacks against the mobile app backend.
Some very popular open source tools exist to make reverse engineering easier:
MobSF - Mobile Security Framework
Mobile Security Framework is an automated, all-in-one mobile application (Android/iOS/Windows) pen-testing framework capable of performing static analysis, dynamic analysis, malware analysis and web API testing.
Inject your own scripts into black box processes. Hook any function, spy on crypto APIs or trace private application code, no source code needed. Edit, hit save, and instantly see the results. All without compilation steps or program restarts.
To account for the use of such reverse engineer tecniques any decisions made about the integrity of a mobile app and device its running on always need to be performed on the backend based on measurements/challenges taken/executed from/in the mobile app and device its running on.
Hence I looked into another solution i.e finding out the signature of current keystore that is used to sign my Application and send it to the backend(which already has the original signature before uploading the build to PlayStore) to validate.
An attacker can easily perform a MitM attack to intercept this request and then extract this signature you are sending to the backend. From here it will be trivial for the attacker to impersonate your mobile app when doing API requests to your API backend. You can learn how to do a MitM attack on your own mobile to try by yourself to extract its signature, and I can help you with that by pointing you to my article Steal that Api Key with a Man in the Middle Attack:
In order to help to demonstrate how to steal an API key, I have built and released in Github the Currency Converter Demo app for Android, which uses the same JNI/NDK technique we used in the earlier Android Hide Secrets app to hide the API key.
So, in this article you will learn how to setup and run a MitM attack to intercept https traffic in a mobile device under your control, so that you can steal the API key. Finally, you will see at a high level how MitM attacks can be mitigated.
While my article is to extract the API key, the steps are the same for extracting your app signature from the API request.
Sample code:
SigningInfo signingInfo = getPackageManager()
             .getPackageInfo(getPackageName(), PackageManager.GET_SIGNATURES)
             .signingInfo;
signingInfo.getApkContentsSigners();
//Send the information to backend to check if matches our original >release.keystore signature
- Is there is any downside to the above simple code to check for APK integrity?
I already mention the MitM attack as a way of extracting the signature being sent to the backend, but an attacker can also resort to use Frida to hook at runtime into the function with this code and extract the signature. The attacker can also decompile your mobile app binary and extract the signature from it.
The downside of your approach is that its easy to bypass by attackers, even by the ones that aren't very skilled, like scripts kids, that just google search on how to do stuff and/or use the dark web to buy specialized solutions/tools to help them achieving their malicious intents.
- If there aren't any then - What is the reason Goggle recommends Play Integrity API instead of this simple solution
The reason Google recommends the Play Integrity API it's because it relies on more advanced techniques that also require a backend side integration, thus making the process harder to bypass and requiring a lot more skills to perform a successful attack.
Marcus Vance is a cybersecurity auditor and technology writer dedicated to educating the public about online safety, data privacy regulations, enterprise security, and emerging cyber threats.
