
System. Security. Cryptography. Cryptographicexception: Keyset Does Not Exist

When I Make an X509 Certificate to Encrypt and Decrypt Messages, I Got Some Error Information and Could Not Able to Fix This Problem. Could Someone Ever Happen...
When I make an x509 certificate to encrypt and decrypt messages, I got some error information and could not able to fix this problem. Could someone ever happen to solve this bug? thanks.
Description: An unhandled exception occurred during the execution of the current web request. Please review the stack trace for more information about the error and where it originated in the code.
Exception Details:
System.Security.Cryptography.CryptographicException: keyset does not exist。
Source Error:
Line 53: using (RSACryptoServiceProvider rsaProviderDecrypt = (RSACryptoServiceProvider)cerDecrypt.PublicKey.Key) Line 54:
{ Line 55: plainHashBytes = rsaProviderDecrypt.Decrypt(encryptedHashBytes, false); Line 56:
rsaProviderDecrypt.Clear(); Line 57:
rsaProviderDecrypt.Dispose();Source File: E:\PayUSite\PayMvcApp\Controllers\HashMessageController.cs Line: 55
Stack Trace:
[CryptographicException: keyset does not exist. ]
System.Security.Cryptography.CryptographicException.ThrowCryptographicException(Int32 hr) +41
System.Security.Cryptography.RSACryptoServiceProvider.DecryptKey(SafeKeyHandle pKeyContext, Byte[] pbEncryptedKey, Int32 cbEncryptedKey, Boolean fOAEP, ObjectHandleOnStack ohRetDecryptedKey) +0
System.Security.Cryptography.RSACryptoServiceProvider.Decrypt(Byte[] rgb, Boolean fOAEP) +579
source code:
string docFile = Server.MapPath("~/docx/DirectAccess_StepByStep.doc");
HashAlgorithm hash = HashAlgorithm.Create("SHA1");
byte[] hashedBytes;
using (FileStream fs = new FileStream(docFile, FileMode.Open))
{
    //compute message hash value
    hashedBytes = hash.ComputeHash(fs);
    hash.Dispose();
    fs.Close();
}

string hashedString = Convert.ToBase64String(hashedBytes);

//encrypt message digest
string priKeyFile = Server.MapPath("~/certificate/WosMiddle.pfx");
X509Certificate2 certEncrypt = new X509Certificate2(priKeyFile, "123456");
byte[] encryptedHashBytes;
using (RSACryptoServiceProvider rsaProviderEncrypt = (RSACryptoServiceProvider)certEncrypt.PrivateKey)
{
    encryptedHashBytes = rsaProviderEncrypt.Encrypt(hashedBytes, false);
    rsaProviderEncrypt.Dispose();
}

//decrypt message digest
string pubKeyFile = Server.MapPath("~/certificate/WosMiddle-pubkey.cer");
X509Certificate2 cerDecrypt = new X509Certificate2(pubKeyFile);
byte[] plainHashBytes;
using (RSACryptoServiceProvider rsaProviderDecrypt = (RSACryptoServiceProvider)cerDecrypt.PublicKey.Key)
{
    //***will throw error message here...***
    plainHashBytes = rsaProviderDecrypt.Decrypt(encryptedHashBytes, false);
    rsaProviderDecrypt.Dispose();
}

//verify message whether was modified
string docFile2 = Server.MapPath("~/docx/DirectAccess_StepByStep.doc");
HashAlgorithm hash2 = HashAlgorithm.Create("SHA1");
byte[] hashedBytes2;
using (FileStream fs2 = new FileStream(docFile2, FileMode.Open))
{
    //compute message hash value
    hashedBytes2 = hash.ComputeHash(fs2);
    fs2.Close();
}

//compare hash value
bool isEqual = plainHashBytes.SequenceEqual(hashedBytes2);
10 Answers
This question is old but for someone looking for the solution while continuing to use Encrypt and Decrypt here is how I manage to solve this error:
The base is my certificate have been installed the wrong way by double-clicking the .pfx file and selecting the store.
The wrong way to install the certificate
1. Double click the certificate:
2. The wizard opens, click in the next button:
3. The wizard show the certificates location, click in the next button:
4. Enter the password then click next:
5. Select the store then click next:
6. The wizard show the certificate information, click in Finish button
7. Succes dialog is showed:
Must Read
So at this point I had the error "Keyset does not exist".
To solve that I proceeded this way (the correct way)
1. Execute Microsoft Management Console (mmc.exe):
2. A blank MMC instance showed:
3. Click in File->Add/Remove Snap-in...
4. Select certificate snap-in an click in Add button:
5. Select Computer account then click in Next button:
6. Select Local computer then click in Finish button:
7. The certificate snap-in is now added, click in OK button:
8. Select the personal store, then right click and select Import:
9. Browse the certificate, and click next:
10. Enter the password, then click in Next button:
11. Automatically select the certificate store:
12. The certificate information shows:
13. Success dialog message shows:
14. Refresh the MMConsole to show the certificate:
15. Right click on the certificate, then click in Manage Private Keys...:
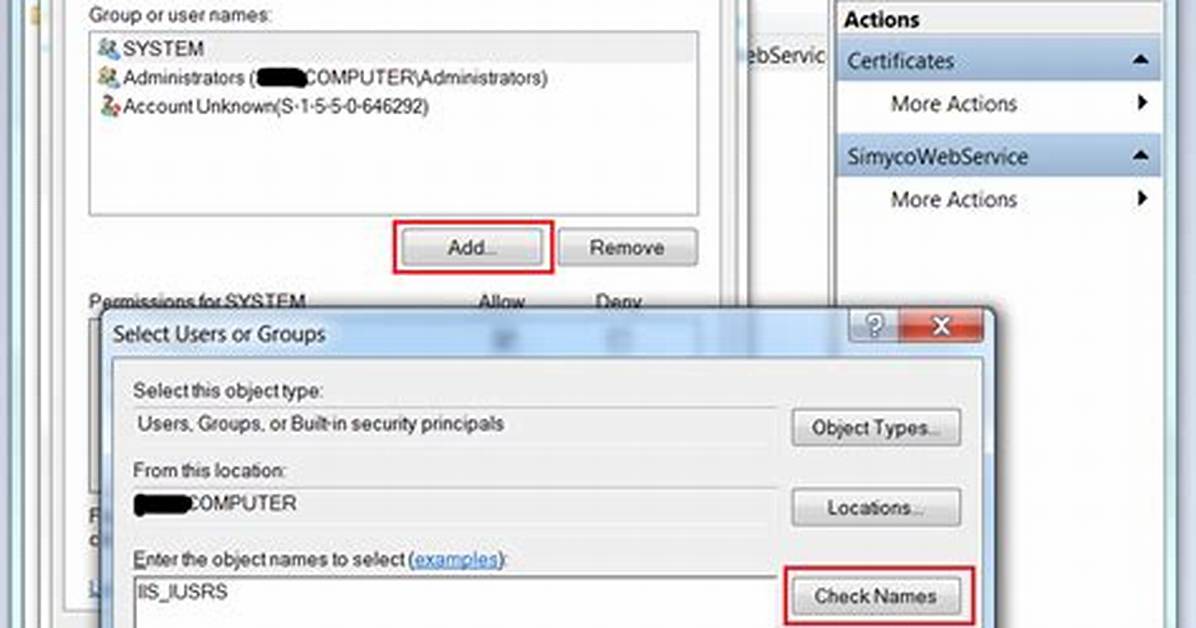
16. Add the pool identity or the IIS user in my case I added IIS_IUSRS:
17. The user has been added, click on OK button:
Sarah Jenkins is a veteran tech journalist with over 12 years of experience covering artificial intelligence, mobile innovations, and digital ethics. Her insights have appeared in leading technology publications worldwide.
