
The Mitre Att&Ck Framework Explained

The Mitre Att&Ack Framework Is a Free, Globally-Accessible Resource That Can Help Guide Organizations Through Assumed Security Breach Incidents—and It Can...
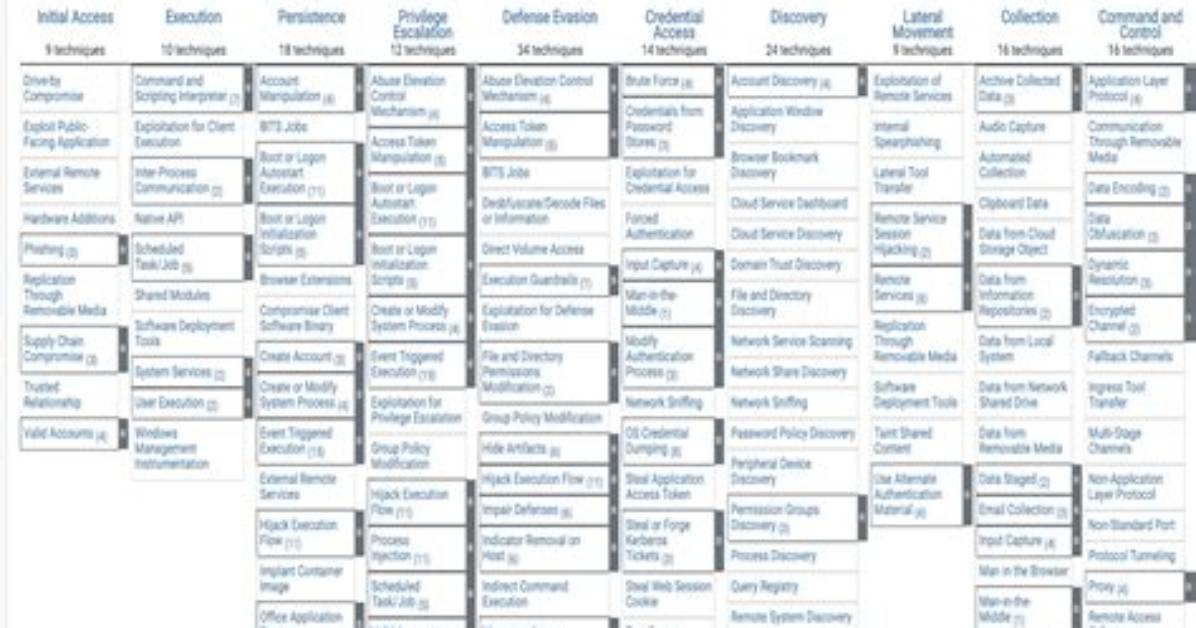
The MITRE ATT&ACK framework is a free, globally-accessible resource that can help guide organizations through assumed security breach incidents—and it can shift the organizational culture around risk management.
The MITRE ATT&CK framework is based on documented knowledge around:
- Adversary/attacker behaviors
- Threat models
- Techniques
- Mitigation tactics
The idea is that by understanding the myriad ways that attackers actually attack, organizations can better prepare for the risks.
In this article, we will discuss what the MITRE ATT&CK Framework is and how the framework can support your security initiatives.
What is the MITRE ATT&CK framework?
The ATT&CK framework provides the attacker perspective on each stage of the cyberattack lifecycle, from end to end.
MITRE ATT&CK was developed by the non-profit organization MITRE in 2013 as a community-led initiative. Its name derives from the acronym for Adversarial Tactics, Techniques, and Common Knowledge (ATT&CK).
The concept—using an end-to-end cyberattack taxonomy as a reference to gain intruder perspective—is not new. (The Lockheed Martin Cyber Kill Chain is another popular framework to model and understand attacker behavior.)
Previously, such extensive information was only available in two ways:
- Through expert cybersecurity incident responders with vast experience.
- As classified documentation in large enterprises regularly addressing Advanced Persistent Threats (APTs) with a dedicated, internal security workforce.
But the ATT&CK framework is unique for the way it drills down into the various attack techniques and procedures used in specific examples, suggesting appropriate mitigation strategies and standardizing language. So, the value proposition of using the MITRE ATT&CK framework has three key points:
- In-depth real-life examples of relevant and appropriate adversary behaviors
- Environment-specific attack techniques and methods
- Standardized language for various attacker methodologies
The framework enables visibility and access, enabling cybersecurity personnel to identify and react to a variety of cybersecurity risks with the right risk management approach. The ATT&CK framework covers several cybersecurity disciplines, including:
- Detection
- Intelligence
- Containment
- Risk management
- Security engineering
The MITRE ATT&CK framework covers mobile, enterprise (cloud), and pre-exploit stages for a variety of cybersecurity disciplines, including:
Who can use the ATT&CK framework?
In terms of who uses this framework, the knowledge can help guide any organization, be it private, non-profit, or government.
The MITRE ATT&CK framework has supports for both mobile and enterprise environments. The true separation, though, is by operating system. The currently supported operating systems are:
- Enterprise: PRE, Windows, macOS, Linux, Cloud & Network
- Mobile: Android & iOS
Other operating systems, including z/OS, aren’t available but may be added in the future.
Robert Thorne covers electric vehicle innovations, autonomous driving systems, global mobility trends, and automotive engineering developments.
