
Trojan. Ircbot

What Is Trojan. Ircbot Infection? in This Article You Will Find Regarding the Interpretation of Trojan. Ircbot and Its Unfavorable Effect on Your Computer...
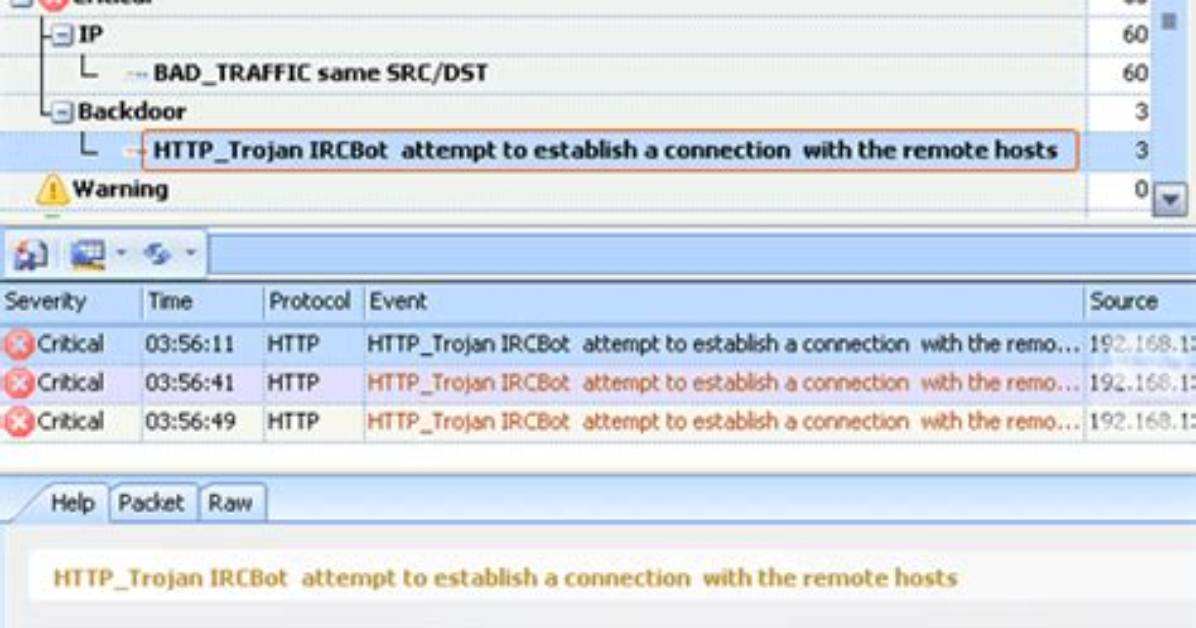
What is Trojan.IRCbot infection?
In this article you will find regarding the interpretation of Trojan.IRCbot and its unfavorable effect on your computer system. Such ransomware are a kind of malware that is specified by online fraudulences to require paying the ransom money by a sufferer.
Most of the instances, Trojan.IRCbot infection will advise its targets to start funds move for the purpose of neutralizing the amendments that the Trojan infection has actually introduced to the victim’s device.
Trojan.IRCbot Summary
These alterations can be as complies with:
- Ciphering the files situated on the victim’s hard disk — so the sufferer can no more utilize the information;
- Preventing routine access to the target’s workstation;
Trojan.IRCbot
The most common channels where Trojan.IRCbot Ransomware Trojans are injected are:
- By ways of phishing emails;
- As a repercussion of user ending up on a source that holds a malicious software program;
As soon as the Trojan is effectively injected, it will either cipher the information on the sufferer’s PC or protect against the tool from working in a proper manner – while additionally putting a ransom money note that states the demand for the sufferers to impact the repayment for the purpose of decrypting the papers or recovering the data system back to the first condition. In the majority of circumstances, the ransom note will turn up when the client reboots the COMPUTER after the system has actually currently been harmed.
Trojan.IRCbot distribution channels.
In different edges of the world, Trojan.IRCbot grows by leaps as well as bounds. However, the ransom notes and also techniques of extorting the ransom money quantity may vary relying on specific regional (local) settings. The ransom money notes and tricks of obtaining the ransom quantity may vary depending on particular local (regional) setups.
For example:
Faulty signals concerning unlicensed software program.
In specific areas, the Trojans frequently wrongfully report having detected some unlicensed applications made it possible for on the target’s gadget. The alert then demands the user to pay the ransom.
Faulty declarations concerning illegal web content.
In countries where software program piracy is less popular, this technique is not as reliable for the cyber fraudulences. Conversely, the Trojan.IRCbot popup alert may wrongly claim to be originating from a law enforcement organization as well as will certainly report having located kid pornography or various other unlawful information on the device.
Trojan.IRCbot popup alert might falsely claim to be acquiring from a law enforcement organization and also will report having located kid pornography or other illegal data on the device. The alert will likewise have a requirement for the user to pay the ransom money.
Technical details
File Info:
crc32: A2F1BA26md5: 588ff00e584a3f5120c2bac622fc4678name: 588FF00E584A3F5120C2BAC622FC4678.mlwsha1: 1a91fd327313f35888ac2b969a850b0681380b28sha256: 5938263c2209486a7ed37ea523b7b7bf7a70a533104f204896015f13008f9a80sha512: a78a35ae9a8272e0b5e44405edf3b8279655f6c4365a83fba90f45f304f7d8e2773d7d87f43be6f39e63902db0eef7dbae70699ff2d1aa01b3a408e2231a9954ssdeep: 6144:nlUYW9cVHir3mg7qabHLB7bN3s3OPXdSzW:nqYJKWg7qahbjPNSzWtype: PE32 executable (GUI) Intel 80386, for MS WindowsVersion Info:
LegalCopyright: Copyright (C) 2017FileVersion: 1.0.0.1ProductVersion: 1.0.0.1Translation: 0x0809 0x04b0
Trojan.IRCbot also known as:
| GridinSoft | Trojan.Ransom.Gen |
| Bkav | W32.AIDetect.malware1 |
| K7AntiVirus | Trojan ( 00521a0c1 ) |
| Lionic | Trojan.Win32.Generic.4!c |
| Elastic | malicious (high confidence) |
| DrWeb | Trojan.MulDrop7.56124 |
| Cynet | Malicious () |
| CAT-QuickHeal | Trojan.Chapak.ZZ5 |
| ALYac | Trojan.GenericKDZ.41582 |
| Cylance | Unsafe |
| Zillya | Worm.Phorpiex.Win32.398 |
| Sangfor | Trojan.Win32.Save.a |
| CrowdStrike | win/malicious_confidence_70% (D) |
| K7GW | Trojan ( 00521a0c1 ) |
| Cybereason | malicious.e584a3 |
| Cyren | W32/Trojan.BCHM-1189 |
| ESET-NOD32 | Win32/Phorpiex.F |
| APEX | Malicious |
| Avast | Win32:Malware-gen |
| ClamAV | Win.Trojan.Emotet-6524991-0 |
| Kaspersky | HEUR:Trojan.Win32.Chapak.gen |
| BitDefender | Trojan.GenericKDZ.41582 |
| NANO-Antivirus | Trojan.Win32.RansomHeur.ewmcdx |
| MicroWorld-eScan | Trojan.GenericKDZ.41582 |
| Tencent | Malware.Win32.Gencirc.10b4c42b |
| Ad-Aware | Trojan.GenericKDZ.41582 |
| Sophos | ML/PE-A |
| Comodo | Malware@#3qaus0x9kb10s |
| BitDefenderTheta | Gen:NN.ZexaF.34058.su0@aqQag8bi |
| VIPRE | Trojan.Win32.Generic!BT |
| TrendMicro | Ransom_HPGANDCRAB.SMG2 |
| McAfee-GW-Edition | BehavesLike.Win32.Generic.dh |
| FireEye | Generic.mg.588ff00e584a3f51 |
| Emsisoft | Trojan.GenericKDZ.41582 (B) |
| SentinelOne | Static AI – Malicious PE |
| Jiangmin | Trojan.IRCBot.vw |
| Avira | TR/AD.Phorpiex.munvt |
| Antiy-AVL | Trojan/Generic.ASMalwS.23B3A46 |
| Microsoft | Trojan:Win32/Tiggre!rfn |
| Arcabit | Trojan.Generic.DA26E |
| SUPERAntiSpyware | |
| ZoneAlarm | HEUR:Trojan.Win32.Generic |
| GData | Trojan.GenericKDZ.41582 |
| AhnLab-V3 | Trojan/Win32.Hermesran.R216465 |
| Acronis | suspicious |
| McAfee | GenericRXDP-NO!588FF00E584A |
| MAX | malware (ai score=100) |
| VBA32 | Trojan.IRCbot |
| Malwarebytes | Trojan.MalPack |
| Panda | Trj/CI.A |
| TrendMicro-HouseCall | Ransom_HPGANDCRAB.SMG2 |
| Rising | Malware.Obscure!1.A3BB (CLASSIC) |
| Yandex | Trojan.GenAsa!jL2Z7f08xv0 |
| Ikarus | Trojan.Win32.Midrami |
| MaxSecure | Ransomeware.CRAB.gen |
| Fortinet | W32/Kryptik.FZML!tr |
| AVG | Win32:Malware-gen |
| Paloalto | generic.ml |
| Qihoo-360 | Win32/Trojan.Phorpiex.HwoCEpsA |
Alexander Ross has covered the video game industry for a decade, writing deep dives on game design, esports tournaments, VR developments, and gaming culture.
