
What Does This This Http Authorization Rewriterule Do?

I Have an Rewrite Recursion Error Somewhere on My Website That Google Bot Caused, but I Can't Find the Url That Caused It Because My Loglevel Is Low. I Raised...
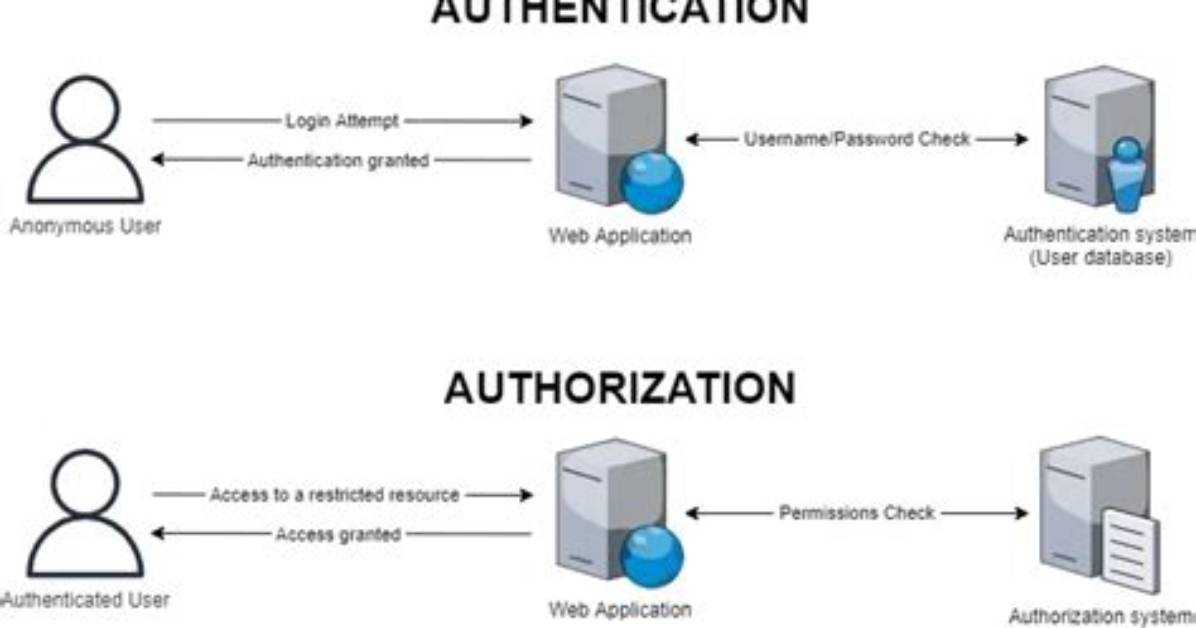
I have an rewrite recursion error somewhere on my website that Google Bot caused, but I can't find the url that caused it because my Loglevel is low. I raised it but it has not happened again so far.
RewriteRule .* - [E=HTTP_AUTHORIZATION:%{HTTP:Authorization}]
All Rewriterules look fine to me and have the [L] flag, except this one.
I can't quite understand it. It is from the open source shop system Magento.
As far as I can tell it does nothing but sets the environment variable E. But isn't that a very stupid way of doing that? Shouldn't you use SetEnv if that was the goal?
2 Answers
Symfony developers Group has a good answer for it. I quote:
it looks like your hosting is running php as a fcgi, not a php5_module, like your localhost does. ( phpinfo - Server API: CGI/FastCGI )
the point is that php5_module automatically handles HTTP_AUTHORIZATION headers, but fcgi_module does not.
solution is simple - add this line to your .htacces on your hosting server:
RewriteRule .* - [E=HTTP_AUTHORIZATION:%{HTTP:Authorization},L]
It worked for me
This line is setting the environment variable to the value of user authentication string - essentially setting a variable rather than constant value. As far as I know, SetEnv and SetEnvIf only allow you to set an environment variable to a predetermined constant.
The variable being set is actually HTTP_AUTHORIZATION, not E. I would guess this is part of the user authentication process.
Chloe Bennett explores the intersection of pop culture, streaming entertainment, digital trends, and contemporary lifestyle. Her weekly commentary reaches thousands of culture enthusiasts.
