
What Is a Deserialization Vulnerability

Share. Insecure Deserialization Is a Well-Known, Yet Not Commonly Occurring, Vulnerability in Which an Attacker Inserts Malicious Objects into a Web...
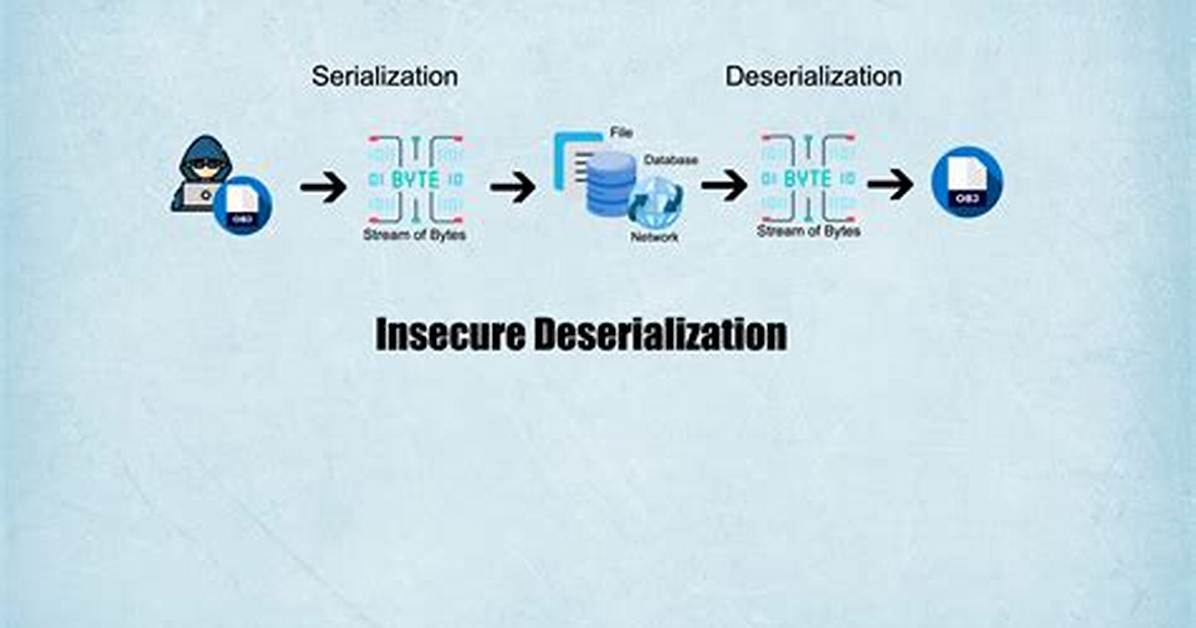
Share. Insecure deserialization is a well-known, yet not commonly occurring, vulnerability in which an attacker inserts malicious objects into a web application. This allows them to inflict denial-of-service (DoS) attacks, remote code execution
What are deserialization attacks?
Insecure deserialization is a vulnerability in which an untrusted or unknown data is used to either inflict a denial of service attack (DoS attack), execute code, bypass authentication or further abuse the logic behind an application. … Serialization and deserialization are safe, common processes in web applications.
What is meant by deserialization?
Deserialization is the process of reconstructing a data structure or object from a series of bytes or a string in order to instantiate the object for consumption. This is the reverse process of serialization, i.e., converting a data structure or object into a series of bytes for storage or transmission across devices.
Chloe Bennett explores the intersection of pop culture, streaming entertainment, digital trends, and contemporary lifestyle. Her weekly commentary reaches thousands of culture enthusiasts.
