
What Is Audit Log in Linux?

Contents the Linux Audit Framework Is a Kernel Feature (Paired with Userspace Tools) That Can Log System Calls. for Example, Opening a File, Killing a Process...
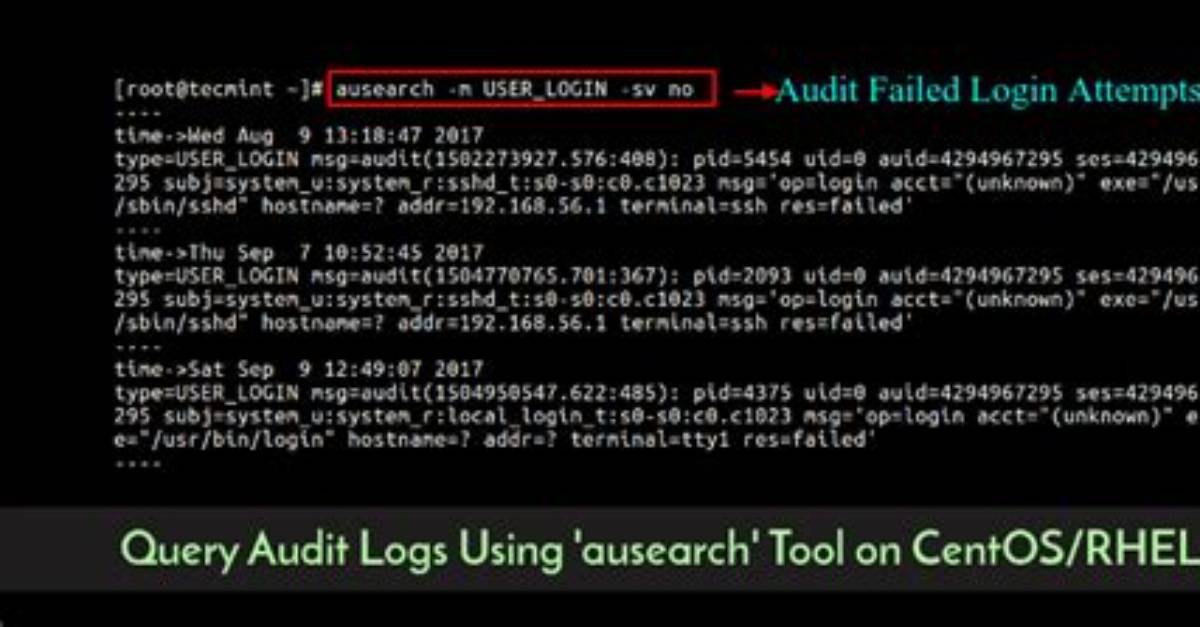
The Linux Audit framework is a kernel feature (paired with userspace tools) that can log system calls. For example, opening a file, killing a process or creating a network connection. These audit logs can be used to monitor systems for suspicious activity. In this post, we will configure rules to generate audit logs.
What does audit log mean?
Per Wikipedia: “An audit trail (also called audit log) is a security-relevant chronological record, set of records, and/or destination and source of records that provide documentary evidence of the sequence of activities that have affected at any time a specific operation, procedure, or event.” An audit log in its most …
What is the function of the audit log?
Audit log has records providing information about who has accessed the system and what operations he or she has performed during a given period of time. Audit logs are useful both for maintaining security and for recovering lost transactions.
Elena Rostova holds a Master's degree in Public Health Journalism. She covers groundbreaking medical research, holistic wellness trends, mental health awareness, and nutritional science.
