
What Is Devsecops? Combining Development, Security & Operations

Devops Has Dramatically Increased How Quickly You Can Deliver New Features to the Market. but with This Speed Comes New Security Risks—This Is Where Devsecops...
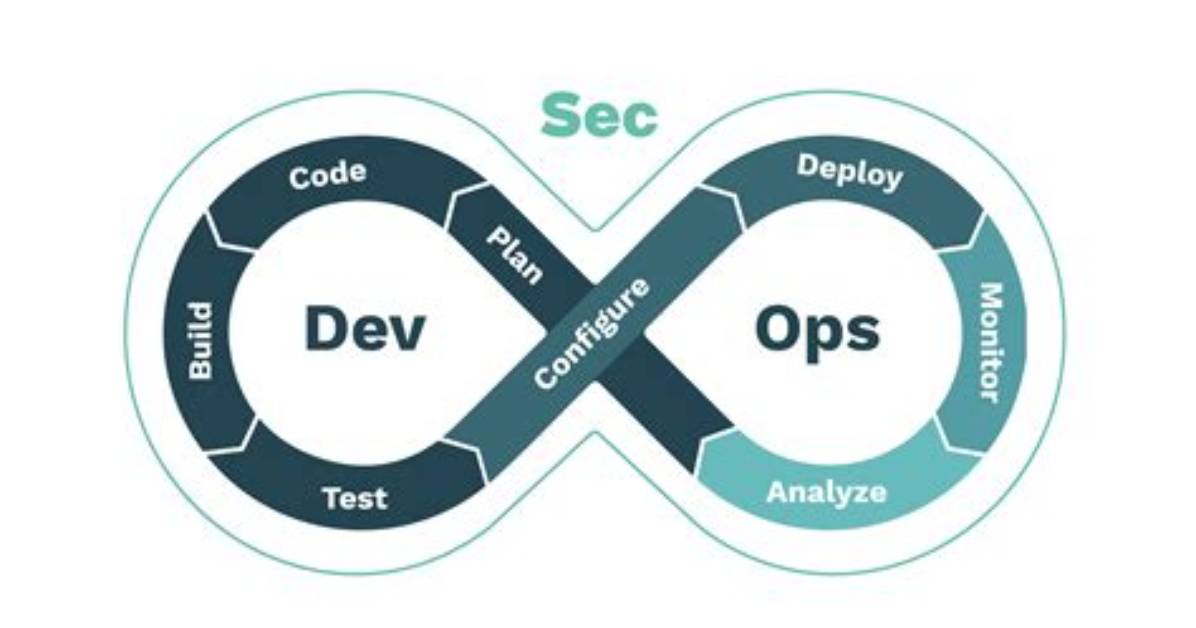
DevOps has dramatically increased how quickly you can deliver new features to the market. But with this speed comes new security risks—this is where DevSecOps comes into play.
(This article is part of our DevOps Guide. Use the right-hand menu to navigate.)
Overview of DevOps & SecOps
DevOps and SecOps have some key similarities. For everyone to have a deeper understanding of other aspects of the project they are working on, both DevOps and SecOps:
- Emphasize the importance of collaboration
- Promote the use of cross-discipline teams
This enhanced insight provides team members with a unique perspective that empowers them to:
- Focus on their tasks
- Consider how their work will impact the work of teammates
Operational intelligence is a constant concern for the teams as they look to enhance their understanding of each system and its vulnerabilities.
SecOps tools feed teams constant streams of insightful data that empowers them to maintain security standards while achieving continuous compliance. Yes, this intense focus on security can result in slower deployment rates. But that extra time provides high levels of security for increased stability and mitigated risks.
Must Read
What is DevSecOps?
Marrying SecOps and DevOps gives us the tools to go faster—while still maintaining safety. DevSecOps refuses to accept that the speed and safety are mutually exclusive.
DevSecOps is about creating a culture where security is a part of everyone’s job, not just the people specifically working in security roles. Security needs to be at the top of every developer’s mind as they build, test, and release features to production.
Bill Gates (reportedly) shared this very message in a 2002 Wired article:
“When we face a choice between adding features and resolving security issues, we need to choose security”.
The faster we move, the truer this becomes.
When we prioritize code creation above security testing, Parkinson’s Law dictates that development work will consume the time up until the release date. Parkinson’s Law says:
“Work expands to fill the time available for its completion.”
This normally means that less thought than necessary is given to security during the development process. If the release date is to be kept, often there is no time left to fix security issues.
Remediation of security concerns, identified late will see the production release date delayed, displeasing the development team and business owners alike. This can lead to dev teams and line of business owners circumventing the IT security team, shipping code to production with or without security scans, regardless of the results.
We cannot afford for security checks to be the final piece of the development puzzle. When security flaws aren’t discovered until the 11th hour or after release, you will have reputational and financial damage—as too many businesses have demonstrated, to their peril.
DevSecOps moves the responsibility for security, ensuring it is fully integrated into every stage of the development journey, continually delivering security throughout the software development process. It achieves this goal through a combination of new tools and processes that enhance security of both the application software and the cloud resources which these apps use.
Marcus Vance is a cybersecurity auditor and technology writer dedicated to educating the public about online safety, data privacy regulations, enterprise security, and emerging cyber threats.
