
What Is Firewall Rules in Linux?

Contents Iptables Is a Linux Command Line Firewall That Allows System Administrators to Manage Incoming and Outgoing Traffic via a Set of Configurable Table...
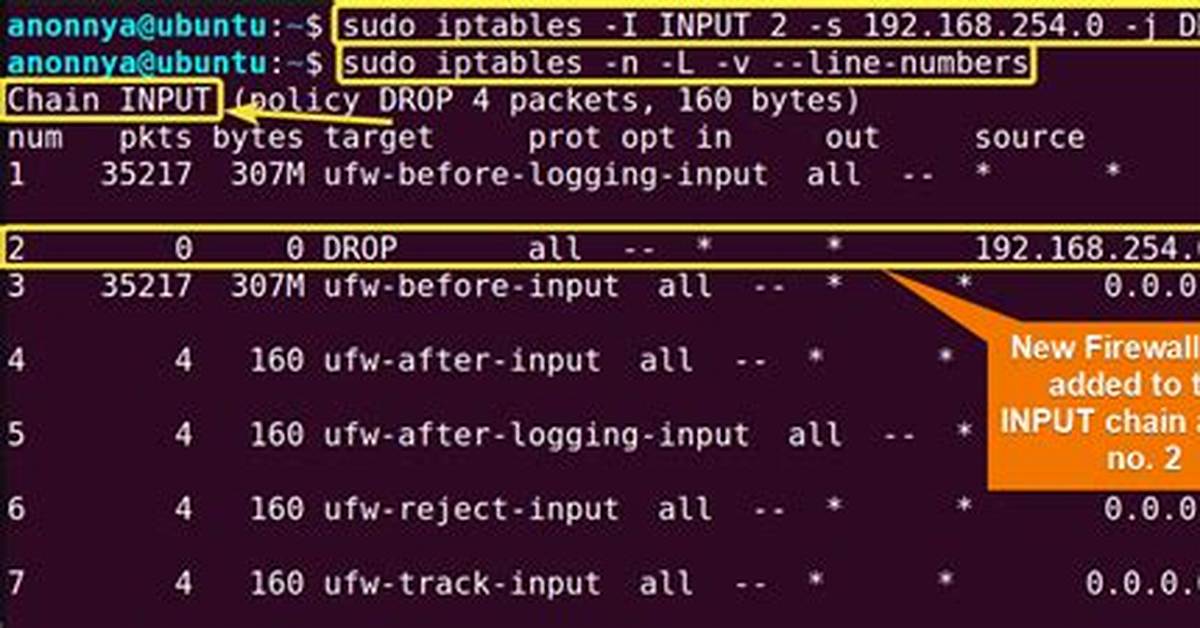
Iptables is a Linux command line firewall that allows system administrators to manage incoming and outgoing traffic via a set of configurable table rules. Iptables uses a set of tables which have chains that contain set of built-in or user defined rules.
What are firewall rules?
Firewall Rules examine the control information in individual packets. The Rules either block or allow those packets based on rules that are defined on these pages. Firewall Rules are assigned directly to computers or to policies that are in turn assigned to a computer or collection of computers.
What is the firewall in Linux?
A Linux firewall is a device that inspects Network traffic ( Inbound /Outbound connections ) and makes a decision to pass or filter out the traffic. Iptables is a CLI tool for managing firewall rules on a Linux machine.
David Miller brings 15 years of experience in global economics, personal finance strategy, and market dynamics. He specializes in turning complex economic trends into actionable insights for everyday readers.
