
What Is Nat Binding? | Contextresponse. Com

Nat Stands for Network Address Translation. Nat Is a Technology That Is Embedded into Network Routingdevices Such as Home Dsl Boxes, Firewalls, Switches and...
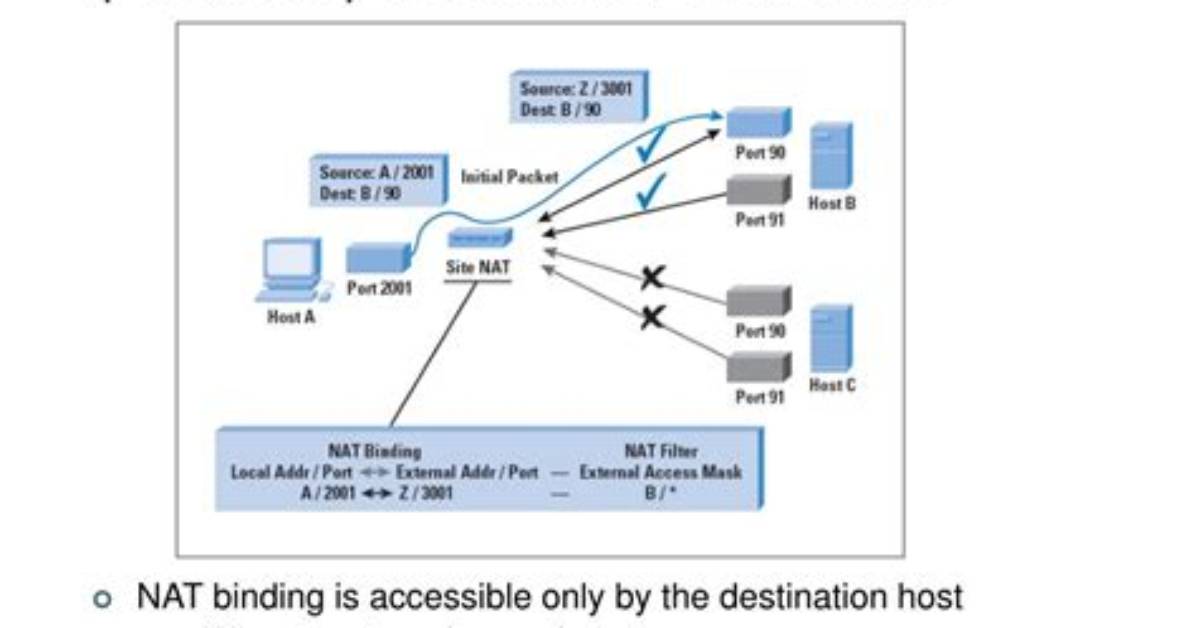
.
Subsequently, one may also ask, what is the NAT traversal problem?
NAT-T (NAT Traversal) Nat Traversal also known as UDP encapsulationallows traffic to get to the specified destination when a devicedoes not have a public address. This is usually the case if yourISP is doing NAT, or the external interface of your firewallis connected to a device that has NATenabled.
Furthermore, how does NAT firewall work? A NAT firewall works by only allowing internettraffic to pass through the gateway if a device on the privatenetwork requested it. If inbound internet traffic does nothave a private IP address to forward to beyond the gateway, theNAT firewall knows the traffic is unsolicited and should bediscarded.
Also Know, what is NAT router settings?
Network Address Translation (NAT) is theability of a router to translate a public IP addressto a private IP address and vice versa. It adds security tothe network by keeping the private IP addresses hidden from theoutside world. Once the ports are successfully opened, theNAT Type will change to Open or Moderate.
How can Nat improve security?
NAT helps improve security and decreasethe number of IP addresses an organization needs. NATgateways sit between two networks, the inside network and theoutside network.
