
What Is Netfilter in Linux?

Contents Netfilter Is a Framework Provided by the Linux Kernel That Allows Various Networking-Related Operations to Be Implemented in the Form of Customized...
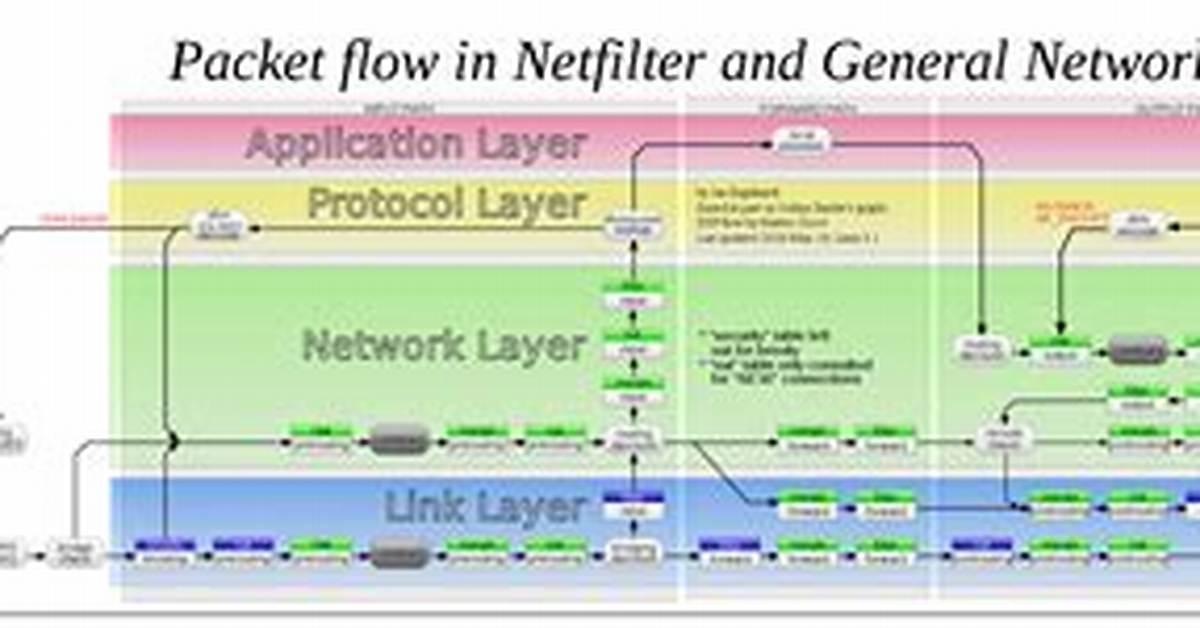
Netfilter is a framework provided by the Linux kernel that allows various networking-related operations to be implemented in the form of customized handlers. … Netfilter represents a set of hooks inside the Linux kernel, allowing specific kernel modules to register callback functions with the kernel’s networking stack.
What is difference between iptables and netfilter?
There may be some confusion about the difference between Netfilter and iptables. Netfilter is an infrastructure; it is the basic API that the Linux 2.4 kernel offers for applications that want to view and manipulate network packets. Iptables is an interface that uses Netfilter to classify and act on packets.
How does netfilter work in Linux?
The netfilter hooks are a framework inside the Linux kernel that allows kernel modules to register callback functions at different locations of the Linux network stack. The registered callback function is then called back for every packet that traverses the respective hook within the Linux network stack.
James Sterling reports on renewable energy developments, climate policy, ecological conservation, and green tech innovations around the globe.
