
What Is Owasp Framework

The Owasp Security Knowledge Framework Is an Open Source Web Application That Explains Secure Coding Principles in Multiple Programming Languages. the Goal of...
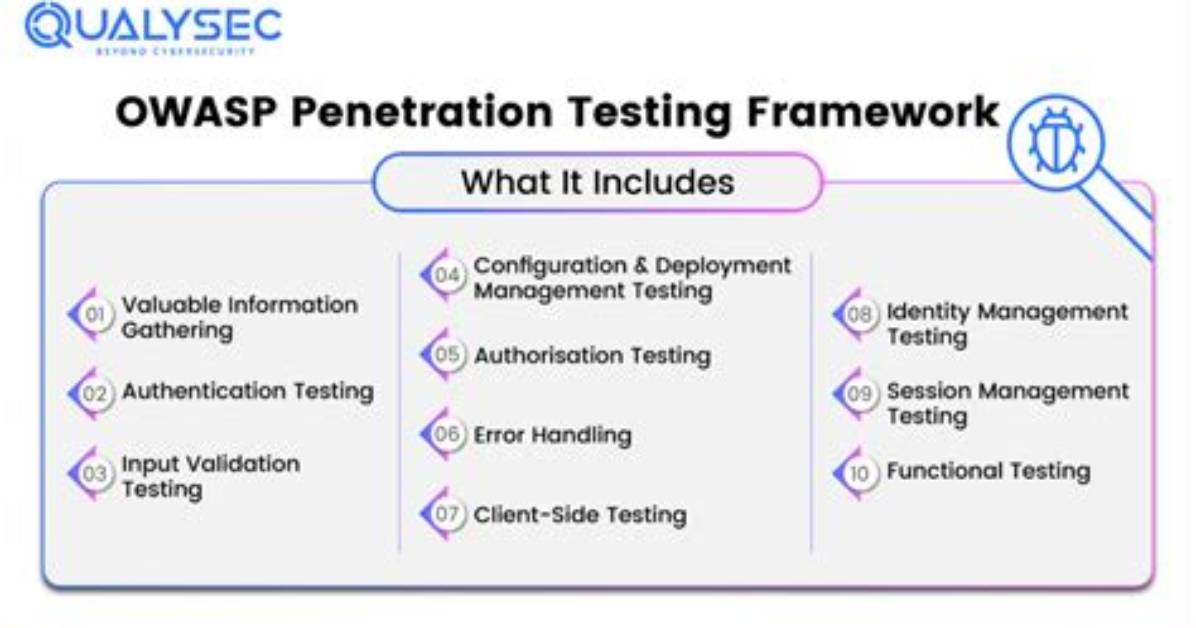
The OWASP Security Knowledge Framework is an open source web application that explains secure coding principles in multiple programming languages. The goal of OWASP-SKF is to help you learn and integrate security by design in your software development and build applications that are secure by design.
What is Owasp used for?
The Open Web Application Security Project (OWASP) is a non-profit organization founded in 2001, with the goal of helping website owners and security experts protect web applications from cyber attacks.
Which vulnerabilities are part of Owasp?
- Injection. Injection occurs when an attacker exploits insecure code to insert (or inject) their own code into a program. …
- Broken Authentication. …
- Sensitive Data Exposure. …
- XML External Entities. …
- Broken Access Control. …
- Security Misconfiguration. …
- Cross-Site Scripting. …
- Insecure Deserialization.
Marcus Vance is a cybersecurity auditor and technology writer dedicated to educating the public about online safety, data privacy regulations, enterprise security, and emerging cyber threats.
