
What Is Setuid Bit Linux?

Contents Setuid Is a Linux File Permission Setting That Allows a User to Execute That File or Program with the Permission of the Owner of That File. … If a...
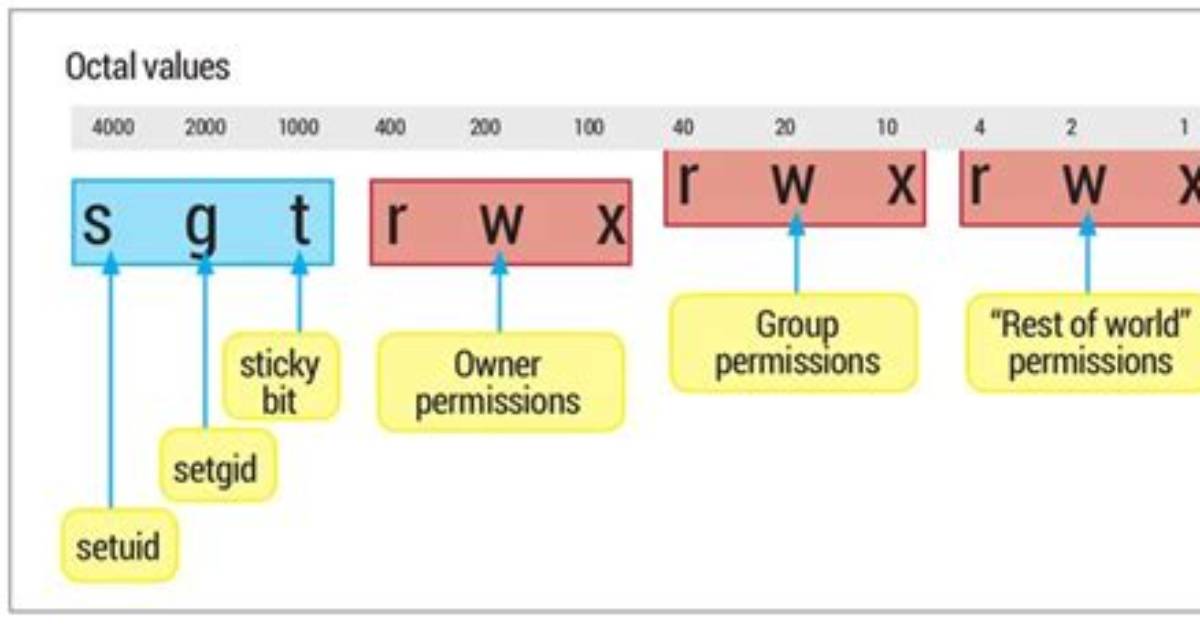
Setuid is a Linux file permission setting that allows a user to execute that file or program with the permission of the owner of that file. … If a file is “setuid” and is owned by the user “root” then a user that has the ability to execute that program will do so as the user root instead of themselves.
What is setuid used for?
The Unix access rights flags setuid and setgid (short for “set user ID” and “set group ID”) allow users to run an executable with the file system permissions of the executable’s owner or group respectively and to change behaviour in directories.
What is the use of sticky bit in Linux?
Usage. The most common use of the sticky bit is on directories residing within filesystems for Unix-like operating systems. When a directory’s sticky bit is set, the filesystem treats the files in such directories in a special way so only the file’s owner, the directory’s owner, or root can rename or delete the file.
Maya is a hardware enthusiast who tests and reviews smart home devices, smartphones, wearables, and audio gear. She focuses on practical consumer value and build quality.
