
Where Are Iptables Rules?

There Is a Service Called "Iptables". This Must Be Enabled. the Rules Are Saved in the File /Etc/Sysconfig/Iptables for Ipv4 and in the File...
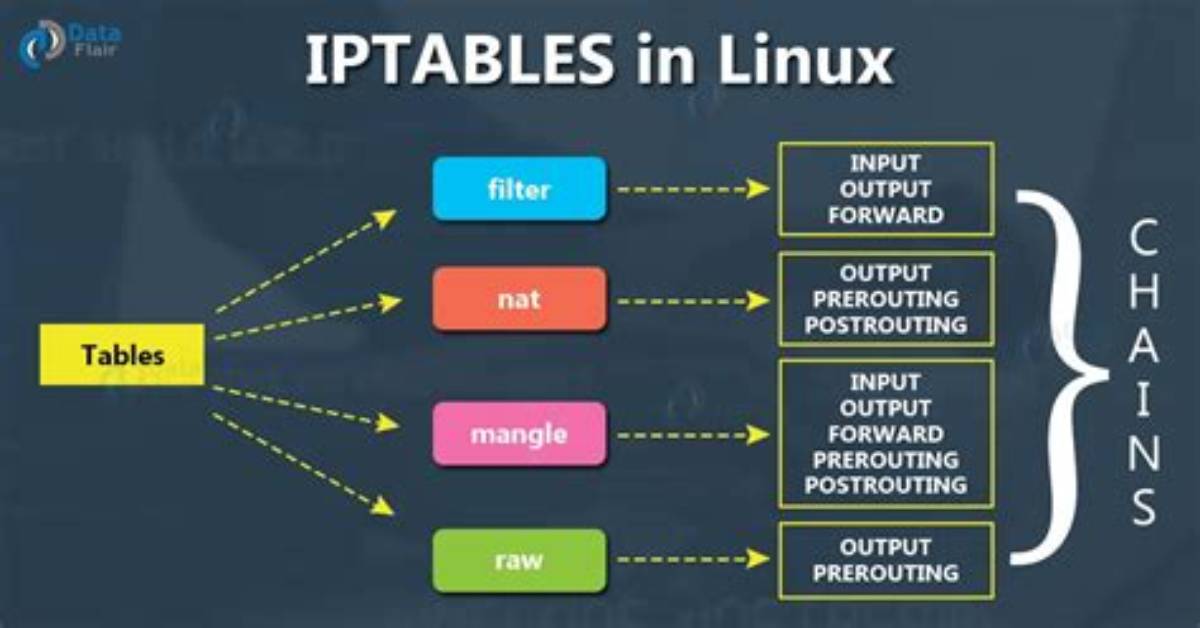
.
In this way, how can I see all iptables rules?
How to list all iptables rules on Linux
- Open the terminal app or login using ssh: ssh [email protected]
- To list all IPv4 rules : sudo iptables -S.
- To list all IPv6 rules : sudo ip6tables -S.
- To list all tables rules : sudo iptables -L -v -n | more.
- To list all rules for INPUT tables : sudo iptables -L INPUT -v -n.
Also Know, how can I permanently save iptables rules? There is no option in iptables which will make your rules permanent. But you can use iptables-save and iptables-restore to fulfill your task. First add the iptable rule using the command you gave. Add the following command in /etc/rc.
Considering this, how do I use iptables?
How to Install and Use Iptables Linux Firewall
- Connect to your server via SSH. If you don't know, you can read our SSH tutorial.
- Execute the following command one by one: sudo apt-get update sudo apt-get install iptables.
- Check the status of your current iptables configuration by running: sudo iptables -L -v.
Do iptables rules take effect immediately?
iptables rules take effect immediately. Because your script is Appending (-A) to the INPUT and OUTPUT chains, your rules are being added to the end of those chains. If you have other terminating rules that precede these rules, then they will take effect (and later rules will not).
