
Which Command Is Used to Configure Firewall Linux?

Contents We Will Be Using “Iptables” the Default Tool Provided in Linux to Establish a Firewall. Iptables Is Used to Set Up, Maintain and Inspect the Tables of...
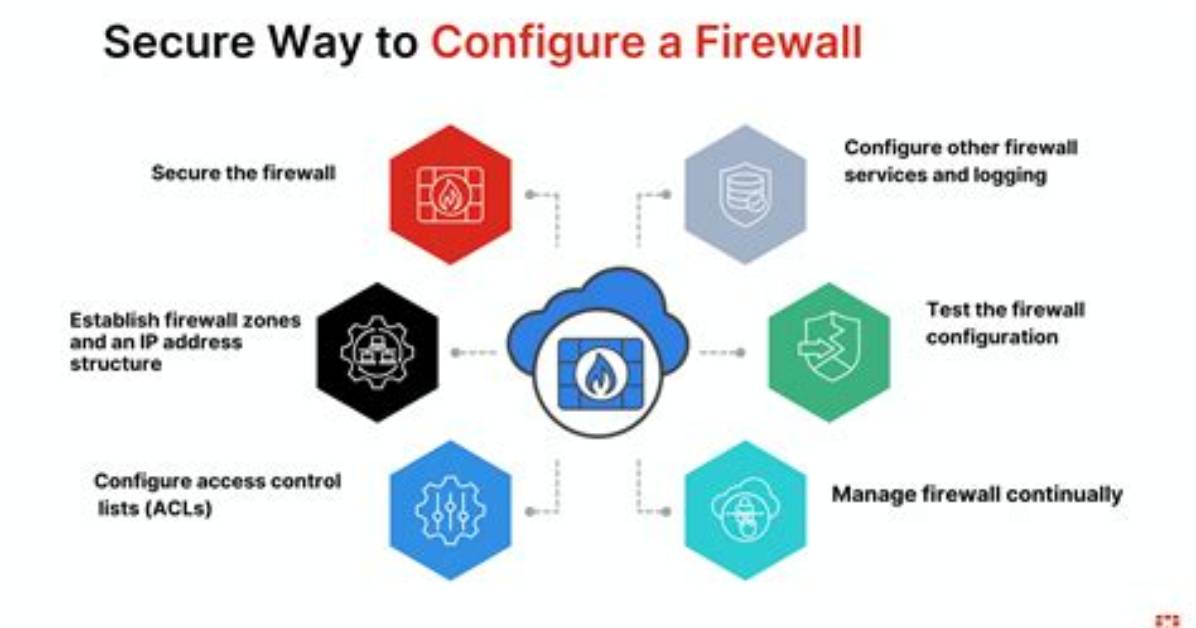
We will be using “IPTables” the default tool provided in Linux to establish a firewall. Iptables is used to set up, maintain and inspect the tables of the IPv4 and IPv6 packet filter rules in the Linux Kernel. Note:- All the command below need sudo privileges.
Which command is used for firewall in Linux?
This article covers the firewall-cmd terminal command found on most Linux distributions. Firewall-cmd is a front-end tool for managing the firewalld daemon, which interfaces with the Linux kernel’s netfilter framework.
How do I add a firewall to Linux?
Firewall Rule Parameters
- Indicates the protocol for the rule.
- Possible values are tcp, udp, icmp.
- Use “all” to allow all protocols. …
- Use either the name (for example: tcp), or the number (for example: 6 for tcp) for protocol.
- /etc/protocols file contains all allowed protocol name and number.
- You an also use –protocol.
Marcus Vance is a cybersecurity auditor and technology writer dedicated to educating the public about online safety, data privacy regulations, enterprise security, and emerging cyber threats.
