
Win32/Agent. Admm

Is a Virus Detection You Can Spectate in Your Computer. It Often Appears After the Preliminary Activities on Your Pc – Opening the Suspicious E-Mail, Clicking...
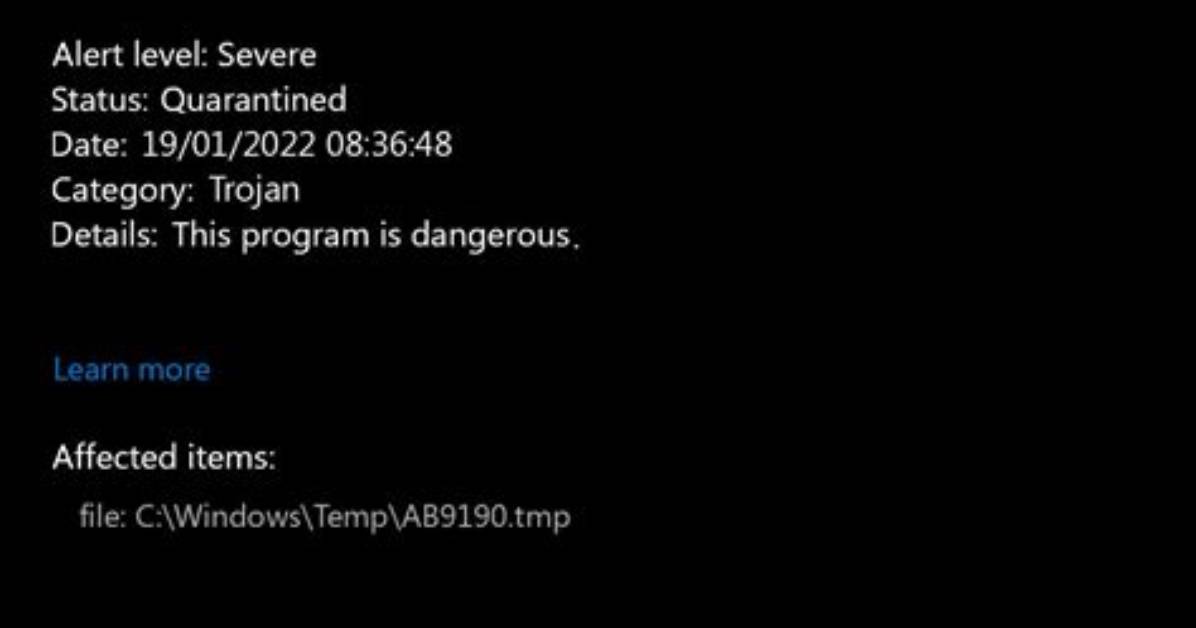
Win32/Agent.ADMM detection is a virus detection you can spectate in your computer. It often appears after the preliminary activities on your PC – opening the suspicious e-mail, clicking the banner in the Web or setting up the program from dubious resources. From the instance it appears, you have a short time to act until it starts its malicious action. And be sure – it is much better not to wait for these malicious things.
What is Win32/Agent.ADMM virus?
Win32/Agent.ADMM is ransomware-type malware. It searches for the documents on your disk drives, encrypts it, and after that asks you to pay the ransom for receiving the decryption key. Besides making your documents locked, this malware also does a ton of damage to your system. It modifies the networking setups in order to prevent you from reading the elimination guides or downloading the antivirus. Sometimes, Win32/Agent.ADMM can even block the setup of anti-malware programs.
Win32/Agent.ADMM Summary
Summarizingly, Win32/Agent.ADMM virus actions in the infected PC are next:
- Sample contains Overlay data;
- Yara rule detections observed from a process memory dump/dropped files/CAPE;
- The binary contains an unknown PE section name indicative of packing;
- The binary likely contains encrypted or compressed data.;
- The executable is compressed using UPX;
- Authenticode signature is invalid;
- Encrypting the files located on the target’s disk — so the victim cannot open these files;
- Blocking the launching of .exe files of security tools
- Blocking the launching of installation files of security tools
Ransomware has been a major problem for the last 4 years. It is difficult to imagine a more damaging malware for both individual users and companies. The algorithms used in Win32/Agent.ADMM (generally, RHA-1028 or AES-256) are not hackable – with minor exclusions. To hack it with a brute force, you need to have more time than our galaxy already exists, and possibly will exist. But that virus does not do all these bad things immediately – it may take up to a few hours to cipher all of your documents. Hence, seeing the Win32/Agent.ADMM detection is a clear signal that you must start the clearing procedure.
Must Read
Where did I get the Win32/Agent.ADMM?
Ordinary methods of Win32/Agent.ADMM injection are common for all other ransomware variants. Those are one-day landing websites where users are offered to download and install the free program, so-called bait e-mails and hacktools. Bait e-mails are a quite modern tactic in malware distribution – you get the email that imitates some regular notifications about deliveries or bank service conditions updates. Within the email, there is a corrupted MS Office file, or a link which leads to the exploit landing page.
Malicious email message. This one tricks you to open the phishing website.
Avoiding it looks fairly simple, but still requires tons of focus. Malware can hide in various spots, and it is far better to prevent it even before it invades your system than to rely upon an anti-malware program. Common cybersecurity knowledge is just an essential item in the modern world, even if your relationship with a computer stays on YouTube videos. That can save you a lot of money and time which you would certainly spend while searching for a solution.
Marcus Vance is a cybersecurity auditor and technology writer dedicated to educating the public about online safety, data privacy regulations, enterprise security, and emerging cyber threats.
