
Win32/Genkryptik. Bsdc

What Is Win32/Genkryptik. Bsdc Infection? in This Post You Will Certainly Discover Regarding the Interpretation of Win32/Genkryptik. Bsdc and Its Negative...
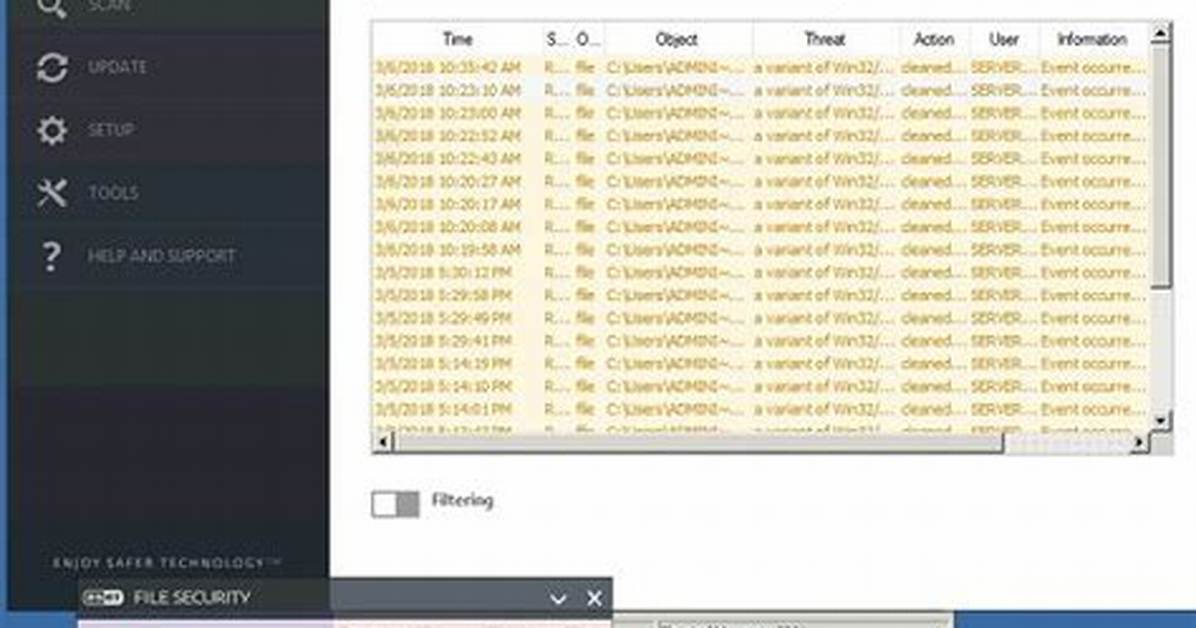
What is Win32/GenKryptik.BSDC infection?
In this post you will certainly discover regarding the interpretation of Win32/GenKryptik.BSDC and its negative impact on your computer system. Such ransomware are a form of malware that is specified by on the internet frauds to demand paying the ransom by a sufferer.
Most of the situations, Win32/GenKryptik.BSDC ransomware will instruct its victims to initiate funds transfer for the objective of reducing the effects of the modifications that the Trojan infection has presented to the victim’s device.
Win32/GenKryptik.BSDC Summary
These adjustments can be as complies with:
- The binary likely contains encrypted or compressed data. In this case, encryption is a way of hiding virus’ code from antiviruses and virus’ analysts.
- Anomalous binary characteristics. This is a way of hiding virus’ code from antiviruses and virus’ analysts.
- Ciphering the records found on the victim’s hard disk — so the target can no more use the information;
- Preventing normal accessibility to the sufferer’s workstation. This is the typical behavior of a virus called locker. It blocks access to the computer until the victim pays the ransom.
| z.whorecord.xyz | Ransom_GANDCRAB.SMALY-5 |
| a.tomx.xyz | Ransom_GANDCRAB.SMALY-5 |
Win32/GenKryptik.BSDC
One of the most regular channels whereby Win32/GenKryptik.BSDC Trojans are injected are:
- By means of phishing emails;
- As an effect of individual winding up on a source that hosts a destructive software program;
As soon as the Trojan is efficiently infused, it will certainly either cipher the data on the target’s PC or stop the device from functioning in a proper fashion – while likewise placing a ransom money note that mentions the demand for the victims to impact the settlement for the objective of decrypting the records or recovering the file system back to the first problem. In many circumstances, the ransom note will certainly turn up when the customer restarts the PC after the system has actually already been damaged.
Win32/GenKryptik.BSDC distribution networks.
In various corners of the world, Win32/GenKryptik.BSDC grows by jumps and bounds. Nonetheless, the ransom notes as well as techniques of extorting the ransom money amount may vary depending upon particular local (local) settings. The ransom money notes and also techniques of obtaining the ransom amount might vary depending on particular regional (regional) setups.
For instance:
Faulty alerts regarding unlicensed software application.
In certain locations, the Trojans commonly wrongfully report having found some unlicensed applications enabled on the target’s tool. The sharp then requires the user to pay the ransom.
Faulty statements about illegal content.
In countries where software application piracy is much less preferred, this method is not as efficient for the cyber fraudulences. Additionally, the Win32/GenKryptik.BSDC popup alert may wrongly assert to be originating from a law enforcement establishment and also will certainly report having situated kid porn or various other prohibited data on the tool.
Win32/GenKryptik.BSDC popup alert may incorrectly declare to be obtaining from a regulation enforcement establishment and will report having situated child porn or other prohibited data on the gadget. The alert will similarly contain a demand for the individual to pay the ransom money.
Must Read
Technical details
File Info:
crc32: 39C32AB8md5: 01c71f7a9d154ec54c59dfd6d8aa926ename: 01C71F7A9D154EC54C59DFD6D8AA926E.mlwsha1: 01fd38c1fb392d299db1d35d85d5a2c0ccc27593sha256: 4f01da3e3b3eeae201259ff11b9a0198abd7aa57abcd02fad18ad17efd1f1689sha512: 5ac5c3744f14f887b06adde6281dc02aadf2f016784917dbf10995bc197de4577c9aa942d83e02a6f8f8ce13fc22451abf6e258a28d221b1cf34e415d30fcd6fssdeep: 3072:Gpau7ANWI/KfotzMdRq5tJKzaxYvZdQ39YzfGGfUpFlMyYHhZqLVuh:GpV7TgqRqnJbxYvw3QhUpgRHhkLVtype: PE32 executable (GUI) Intel 80386, for MS WindowsVersion Info:
0: [No Data]
Win32/GenKryptik.BSDC also known as:
| GridinSoft | Trojan.Ransom.Gen |
| Bkav | W32.AIDetect.malware1 |
| Elastic | malicious (high confidence) |
| MicroWorld-eScan | Trojan.BRMon.Gen.3 |
| FireEye | Generic.mg.01c71f7a9d154ec5 |
| CAT-QuickHeal | Trojan.Chapak.ZZ5 |
| McAfee | GenericRXEF-VN!01C71F7A9D15 |
| Cylance | Unsafe |
| VIPRE | Trojan.Win32.Generic!BT |
| Sangfor | Virus_Suspicious.Win32.Sality.ae |
| CrowdStrike | win/malicious_confidence_100% (D) |
| BitDefender | Trojan.BRMon.Gen.3 |
| K7GW | Trojan ( 655333331 ) |
| K7AntiVirus | Trojan ( 00532e3d1 ) |
| Cyren | W32/S-0fb65811!Eldorado |
| Symantec | Packed.Generic.525 |
| APEX | Malicious |
| Avast | Win32:Malware-gen |
| Kaspersky | HEUR:Trojan.Win32.Generic |
| NANO-Antivirus | Trojan.Win32.Yakes.eypasb |
| Rising | Trojan.GenKryptik!8.AA55 (CLOUD) |
| Ad-Aware | Trojan.BRMon.Gen.3 |
| Emsisoft | Trojan.BRMon.Gen.3 (B) |
| Comodo | TrojWare.Win32.NeutrinoPOS.E@7jwvo8 |
| F-Secure | |
| DrWeb | BackDoor.IRC.Bot.4081 |
| TrendMicro | Ransom_GANDCRAB.SMALY-5 |
| McAfee-GW-Edition | BehavesLike.Win32.Generic.cc |
| Sophos | Mal/Generic-S + Mal/GandCrab-D |
| Ikarus | Trojan.Win32.Krypt |
| Jiangmin | TrojanDownloader.Upatre.aiqo |
| MaxSecure | Ransomeware.CRAB.gen |
| Avira | HEUR/AGEN.1121533 |
| Antiy-AVL | Trojan[Banker]/Win32.NeutrinoPOS |
| Kingsoft | Win32.Troj.Banker.(kcloud) |
| Microsoft | Ransom:Win32/Gandcrab.SF!MTB |
| Arcabit | Trojan.BRMon.Gen.3 |
| ZoneAlarm | HEUR:Trojan.Win32.Generic |
| GData | Trojan.BRMon.Gen.3 |
| Cynet | Malicious () |
| AhnLab-V3 | Win-Trojan/Gandcrab02.Exp |
| Acronis | suspicious |
| BitDefenderTheta | Gen:NN.ZexaF.34590.kuW@amodUCji |
| ALYac | Trojan.BRMon.Gen.3 |
| VBA32 | TrojanDownloader.Upatre |
| Malwarebytes | |
| Panda | Trj/CI.A |
| ESET-NOD32 | a variant of Win32/GenKryptik.BSDC |
| TrendMicro-HouseCall | Ransom_GANDCRAB.SMALY-5 |
| Tencent | Win32.Trojan.Generic.Eyh |
| Yandex | Trojan.CHS!aUg+uHJLtn4 |
| SentinelOne | Static AI – Malicious PE |
| eGambit | Unsafe.AI_Score_93% |
| Fortinet | W32/GenKryptik.DWPH!tr |
| AVG | Win32:Malware-gen |
| Cybereason | malicious.a9d154 |
| Paloalto | generic.ml |
| Qihoo-360 | Win32/Trojan.7c2 |
Sarah Jenkins is a veteran tech journalist with over 12 years of experience covering artificial intelligence, mobile innovations, and digital ethics. Her insights have appeared in leading technology publications worldwide.
