
Win32/Killmbr. Nds

What Is Win32/Killmbr. Nds Infection? in This Short Article You Will Discover About the Definition of Win32/Killmbr. Nds as Well as Its Adverse Impact on Your...
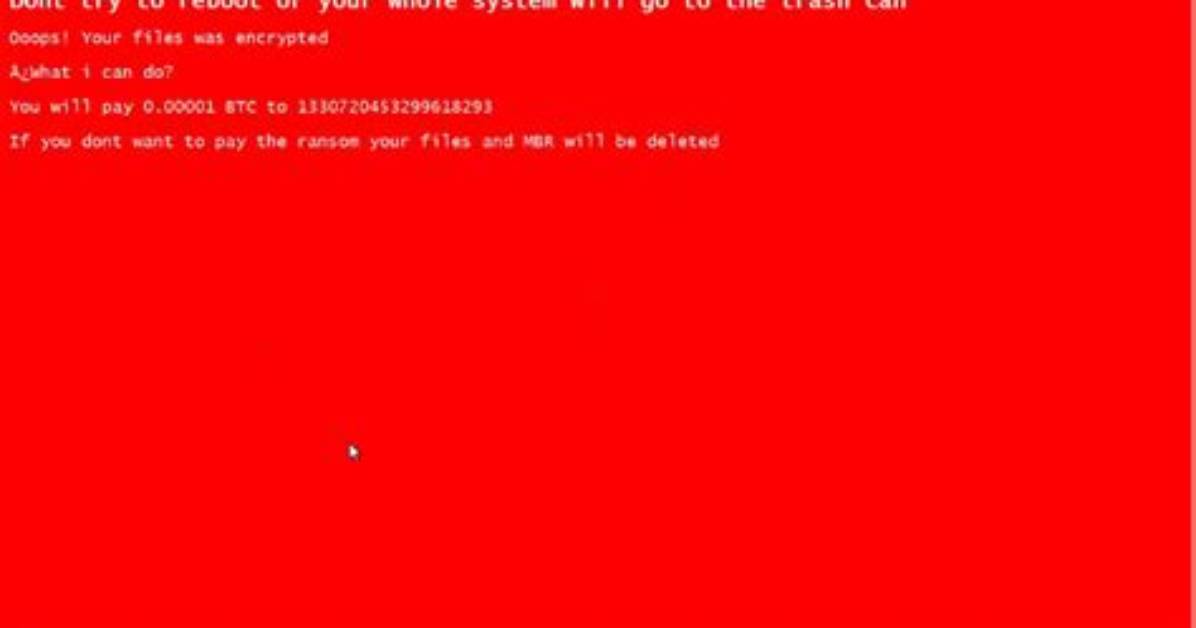
What is Win32/KillMBR.NDS infection?
In this short article you will discover about the definition of Win32/KillMBR.NDS as well as its adverse impact on your computer system. Such ransomware are a form of malware that is clarified by on the internet scams to require paying the ransom by a victim.
Most of the cases, Win32/KillMBR.NDS infection will instruct its sufferers to initiate funds transfer for the objective of reducing the effects of the amendments that the Trojan infection has introduced to the sufferer’s gadget.
Win32/KillMBR.NDS Summary
These alterations can be as complies with:
- A process attempted to delay the analysis task.;
- Uses Windows utilities for basic functionality;
- Attempts to repeatedly call a single API many times in order to delay analysis time. This significantly complicates the work of the virus analyzer. Typical malware tactics!
- Writes a potential ransom message to disk;
- Anomalous binary characteristics. This is a way of hiding virus’ code from antiviruses and virus’ analysts.
- Uses suspicious command line tools or Windows utilities;
- Ciphering the documents situated on the sufferer’s hard disk — so the sufferer can no more use the data;
- Preventing regular access to the sufferer’s workstation. This is the typical behavior of a virus called locker. It blocks access to the computer until the victim pays the ransom.
Win32/KillMBR.NDS
One of the most regular channels where Win32/KillMBR.NDS are infused are:
- By ways of phishing emails;
- As a repercussion of individual winding up on a source that hosts a destructive software application;
As soon as the Trojan is efficiently injected, it will certainly either cipher the information on the victim’s computer or prevent the device from working in a correct fashion – while additionally placing a ransom money note that points out the need for the targets to effect the repayment for the objective of decrypting the papers or recovering the documents system back to the preliminary problem. In many circumstances, the ransom money note will come up when the customer reboots the PC after the system has currently been damaged.
Win32/KillMBR.NDS circulation networks.
In different edges of the globe, Win32/KillMBR.NDS grows by jumps and bounds. However, the ransom notes and also techniques of extorting the ransom quantity might vary depending upon certain regional (regional) settings. The ransom notes and techniques of obtaining the ransom amount might differ depending on certain neighborhood (local) setups.
For example:
Faulty signals concerning unlicensed software program.
In certain locations, the Trojans usually wrongfully report having detected some unlicensed applications enabled on the target’s tool. The alert after that demands the user to pay the ransom money.
Faulty statements concerning illegal material.
In countries where software piracy is much less preferred, this technique is not as reliable for the cyber frauds. Conversely, the Win32/KillMBR.NDS popup alert might incorrectly claim to be originating from a law enforcement establishment and also will report having situated kid porn or various other illegal information on the device.
Win32/KillMBR.NDS popup alert might wrongly claim to be deriving from a regulation enforcement establishment and also will report having situated child pornography or other illegal information on the gadget. The alert will similarly contain a need for the customer to pay the ransom money.
Technical details
File Info:
crc32: 68605AFBmd5: 9d46b464bb366a13b30088931b79c591name: 9D46B464BB366A13B30088931B79C591.mlwsha1: 7e049decddbc6fc426e0f0650d9063fa1a8345f8sha256: 5b2223d29e2c0fe5faeb3779687715b11bab39548f990ac554026eafa90ca803sha512: 0a262738d42a3a54f90637cd9b922ec2028d6b5991f2f1f31c502e9a137775395d7f605f98008dc9f030bea68c3c4f25645ec4f825adf3f36ea35a5508938e10ssdeep: 3072:L7DhdC6kzWypvaQ0FxyNTBfhP7GapQjb7HCb6xiNh+hYM1yjEXC45J551r/EssNZ:LBlkZvaF4NTB5zGavIfyjWpRHWfdYaVtype: PE32 executable (console) Intel 80386, for MS WindowsVersion Info:
LegalCopyright: 2137InternalName: Corona virusFileVersion: 1,0,0,0CompanyName: ChinaProductName: Covid18 ransomwareProductVersion: 1,0,0,0FileDescription: corona virus ransomwareTranslation: 0x0000 0x04e4
Win32/KillMBR.NDS also known as:
| GridinSoft | Trojan.Ransom.Gen |
| Bkav | W32.AIDetect.malware2 |
| Elastic | malicious (high confidence) |
| DrWeb | Trojan.KillMBR.24848 |
| Cynet | Malicious () |
| ALYac | Trojan.Ransom.Filecoder |
| Cylance | Unsafe |
| Sangfor | Trojan.Win32.Killmbr.mt |
| CrowdStrike | win/malicious_confidence_100% (W) |
| Alibaba | Trojan:Win32/Killmbr.49ee14b4 |
| Cybereason | malicious.4bb366 |
| Cyren | W32/Fuery.P.gen!Eldorado |
| Symantec | ML.Attribute.HighConfidence |
| ESET-NOD32 | a variant of Win32/KillMBR.NDS |
| Avast | Win32:Malware-gen |
| Kaspersky | HEUR:Trojan.Win32.Generic |
| BitDefender | Trojan.GenericKD.36334892 |
| NANO-Antivirus | Trojan.Win32.KillMBR.ilrirc |
| ViRobot | Trojan.Win32.Z.Killmbr.353280 |
| MicroWorld-eScan | Trojan.GenericKD.36334892 |
| Tencent | Win32.Risk.Malware.Huze |
| Ad-Aware | Trojan.GenericKD.36334892 |
| Sophos | Mal/Generic-R |
| BitDefenderTheta | Gen:NN.ZexaF.34628.vu0@a0iTBe |
| VIPRE | Trojan.Win32.Generic!BT |
| TrendMicro | TROJ_GEN.R002C0DBC21 |
| McAfee-GW-Edition | BehavesLike.Win32.Generic.fh |
| FireEye | Generic.mg.9d46b464bb366a13 |
| Emsisoft | Trojan.GenericKD.36334892 (B) |
| Webroot | W32.Trojan.Gen |
| eGambit | Unsafe.AI_Score_98% |
| Microsoft | Trojan:Win32/Killmbr |
| Arcabit | Trojan.Generic.D22A6D2C |
| GData | Trojan.GenericKD.36334892 |
| McAfee | Artemis!9D46B464BB36 |
| MAX | malware (ai score=89) |
| VBA32 | Trojan.Wacatac |
| Malwarebytes | Malware.Heuristic.1008 |
| Panda | Trj/CI.A |
| TrendMicro-HouseCall | TROJ_GEN.R002C0DBC21 |
| Rising | Trojan.KillMBR!8.F58 (CLOUD) |
| Ikarus | Trojan.Win32.KillMBR |
| Fortinet | W32/KillMBR.NDS!tr |
| AVG | Win32:Malware-gen |
Alexander Ross has covered the video game industry for a decade, writing deep dives on game design, esports tournaments, VR developments, and gaming culture.
