
Win32/Kryptik. Hljk

What Is Win32/Kryptik. Hljk Infection? in This Short Article You Will Discover About the Meaning of Win32/Kryptik. Hljk and Also Its Unfavorable Effect on Your...
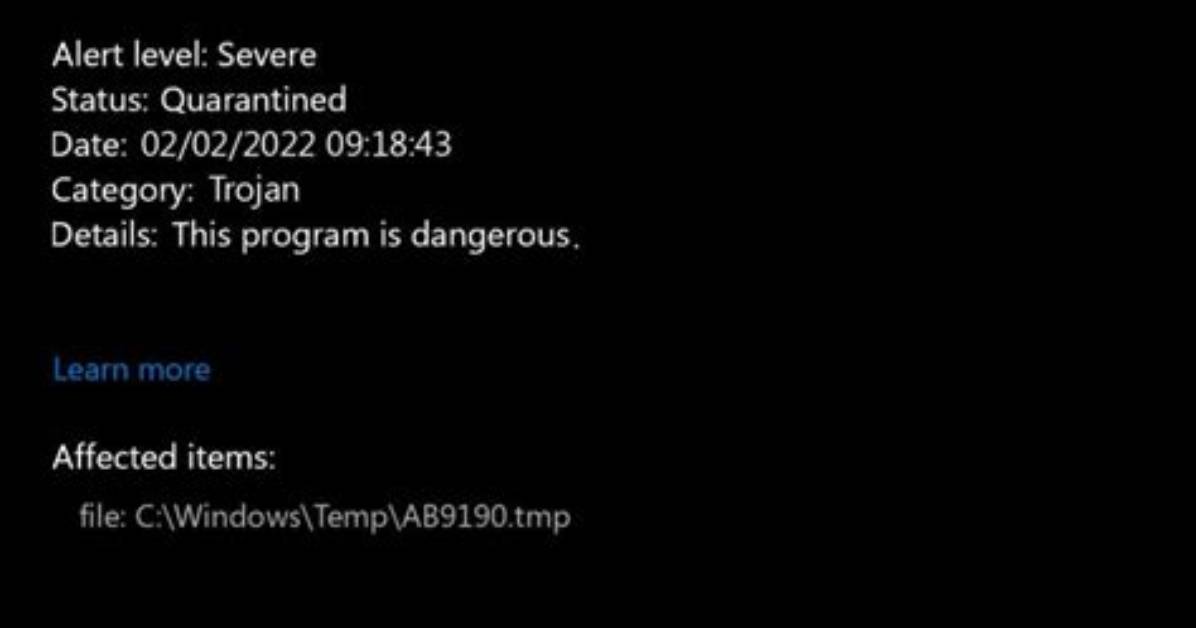
What is Win32/Kryptik.HLJK infection?
In this short article you will discover about the meaning of Win32/Kryptik.HLJK and also its unfavorable effect on your computer system. Such ransomware are a form of malware that is specified by on-line fraudulences to require paying the ransom money by a target.
Most of the instances, Win32/Kryptik.HLJK virus will certainly instruct its targets to start funds transfer for the purpose of counteracting the modifications that the Trojan infection has presented to the victim’s tool.
Win32/Kryptik.HLJK Summary
These adjustments can be as adheres to:
- Executable code extraction;
- Creates RWX memory;
- Unconventionial language used in binary resources: Oriya;
- The binary likely contains encrypted or compressed data.;
- Network activity detected but not expressed in API logs;
- Anomalous binary characteristics;
- Ciphering the records found on the target’s disk drive — so the victim can no longer utilize the information;
- Preventing normal access to the victim’s workstation;
Win32/Kryptik.HLJK
The most common networks whereby Win32/Kryptik.HLJK Ransomware Trojans are injected are:
- By ways of phishing emails;
- As an effect of individual ending up on a source that hosts a harmful software application;
As quickly as the Trojan is effectively injected, it will certainly either cipher the data on the sufferer’s PC or protect against the gadget from operating in an appropriate way – while likewise putting a ransom money note that mentions the need for the sufferers to effect the repayment for the objective of decrypting the papers or recovering the documents system back to the preliminary condition. In a lot of instances, the ransom note will come up when the customer reboots the COMPUTER after the system has already been damaged.
Win32/Kryptik.HLJK distribution networks.
In various corners of the globe, Win32/Kryptik.HLJK expands by leaps and also bounds. Nonetheless, the ransom money notes and methods of obtaining the ransom money amount might vary relying on certain regional (regional) settings. The ransom money notes as well as methods of obtaining the ransom amount might vary depending on certain neighborhood (local) setups.
As an example:
Faulty signals regarding unlicensed software application.
In certain locations, the Trojans typically wrongfully report having actually found some unlicensed applications enabled on the sufferer’s gadget. The alert after that requires the individual to pay the ransom money.
Faulty statements about prohibited material.
In countries where software program piracy is less preferred, this approach is not as efficient for the cyber frauds. Alternatively, the Win32/Kryptik.HLJK popup alert may incorrectly assert to be deriving from a police organization and also will report having situated kid porn or various other unlawful information on the device.
Win32/Kryptik.HLJK popup alert might falsely claim to be acquiring from a legislation enforcement establishment and will certainly report having situated kid porn or other prohibited information on the device. The alert will likewise include a demand for the individual to pay the ransom.
Technical details
File Info:
crc32: 3B3504D0md5: ed3f7af80a20441c4ec9cfd7e6a05057name: ED3F7AF80A20441C4EC9CFD7E6A05057.mlwsha1: 3f52176af2d5abf15ab6d4f5686f7a5558a82a7esha256: 79483b08967ab9788038c345291a6fe61ba4f65b3594de2d4f47b50a486accbasha512: eec817df0ed1da6eb5b8f5ac554eb83fef9e2e30dd0a03df282dc19aae78ab6dc626f008c584351715f362b49fb01cc61bc20de6cc2f579829c2434cd76be8d9ssdeep: 6144:YQbkL3USjObO/lEn+gzctCpI+Jatn7PLI+UtzBnyWCXn6hzXG:YQbkL3DObO/qpw80PLIptzRyWMztype: PE32 executable (GUI) Intel 80386, for MS WindowsVersion Info:
Translations: 0x37a5 0x013b
Win32/Kryptik.HLJK also known as:
| GridinSoft | Trojan.Ransom.Gen |
| Bkav | W32.AIDetect.malware1 |
| Elastic | malicious (high confidence) |
| DrWeb | Trojan.PWS.Siggen3.96 |
| Cynet | Malicious () |
| McAfee | GenericRXAA-AA!ED3F7AF80A20 |
| Cylance | Unsafe |
| Sangfor | Trojan.Win32.Save.a |
| CrowdStrike | win/malicious_confidence_100% (D) |
| K7GW | Hacktool ( 700007861 ) |
| Cybereason | malicious.af2d5a |
| Cyren | W32/Kryptik.EIP.gen!Eldorado |
| Symantec | ML.Attribute.HighConfidence |
| ESET-NOD32 | a variant of Win32/Kryptik.HLJK |
| APEX | Malicious |
| Avast | Win32:PWSX-gen [Trj] |
| ClamAV | Win.Malware.Pwsx-9872132-0 |
| Kaspersky | HEUR:Trojan-Spy.Win32.Stealer.gen |
| BitDefender | Trojan.GenericKDZ.75887 |
| MicroWorld-eScan | Trojan.GenericKDZ.75887 |
| Ad-Aware | Trojan.GenericKDZ.75887 |
| Sophos | ML/PE-A |
| BitDefenderTheta | Gen:NN.ZexaF.34738.yuW@a0T!b!lG |
| McAfee-GW-Edition | BehavesLike.Win32.BadFile.fh |
| FireEye | Generic.mg.ed3f7af80a20441c |
| Emsisoft | Trojan.GenericKDZ.75887 (B) |
| SentinelOne | Static AI – Malicious PE |
| Jiangmin | Trojan.PSW.Racealer.cln |
| eGambit | Unsafe.AI_Score_97% |
| Microsoft | Trojan:Win32/Azorult!ml |
| Gridinsoft | Ransom.Win32.STOP.ko!se5543 |
| GData | Trojan.GenericKDZ.75887 |
| AhnLab-V3 | Trojan/Win.MalPE.R425971 |
| Acronis | suspicious |
| VBA32 | BScope.Trojan.Sabsik.FL |
| MAX | malware (ai score=82) |
| Malwarebytes | Trojan.MalPack.GS |
| Panda | Trj/Genetic.gen |
| Rising | Malware.Heuristic!ET#85% (RDMK:cmRtazrsMIAGRS+cmMO+rapouKvL) |
| Ikarus | Trojan.Win32.Crypt |
| Fortinet | W32/GenKryptik.FGOR!tr |
| AVG | Win32:PWSX-gen [Trj] |
Marcus Vance is a cybersecurity auditor and technology writer dedicated to educating the public about online safety, data privacy regulations, enterprise security, and emerging cyber threats.
